BRIEFGov / MilitaryhighP42
Dox of an NSA employee posted on underground forum
NSA
Detected16 October 2026 · 19:56 UTC
A threat actor posted a dox of an alleged NSA employee on DarkForums roughly seven hours before discovery. Doxxing government personnel exposes personal data that enables harassment, social engineering and physical targeting. It is US-focused rather than AR-LATAM, but relevant to government/military threat monitoring.
CategoryGov / Military
Severityhigh
Priority score42
Detected16 October 2026 · 19:56 UTC
Gov / Military● 90
Filtración de base de datos de la Secretaría de Salud de MéxicoA threat actor is exposing a database attributed to Mexico's federal Secretariat of Health, a core government body handling citizens' sensitive medical data. Such records typically include personal identifiers, clinical data and contact details, creating serious privacy and fraud risk. Posted minutes ago, this is a live, time-sensitive leak affecting Mexican government and healthcare defenders.Gov / Military● 55
Filtración de datos del Ministerio Coordinador de Asuntos Económicos de IndonesiaA database attributed to Indonesia's Coordinating Ministry for Economic Affairs surfaced on a dark web forum within hours of posting. Government ministry records can contain officials' and citizens' PII and internal contact data. If authentic, it raises targeted-phishing and intelligence-collection risks against a national economic body.Gov / Military● 66
Base de datos del Ministerio de Defensa de Israel a la ventaA dataset attributed to the Israeli Ministry of Defense is being offered on the forum, which if genuine would expose sensitive defense personnel or systems data. Offers like this fuel state-level targeting and credential abuse. Defenders should monitor for credential reuse and linked access sales.Gov / Military● 70
Filtración de código fuente de un programa del Gobierno del PSOE (psoe.es)Over 2 GB of source code from a Spanish government program tied to the PSOE party (psoe.es) has been posted on a dark web forum. Code exposure can reveal internal logic, hardcoded credentials and API endpoints, enabling follow-on intrusion. Spanish public-sector defenders should verify the exposure and rotate any secrets present in the code.
Gov / Military● 90
Base de datos sde.gob.ar con 800.000 registros publicadaA second thread by 'Returnero' advertises roughly 800,000 records from the Argentine government domain sde.gob.ar. The volume and government nature of the data raise the risk of mass identity misuse, credential abuse and social engineering against public entities. This should be treated as a fresh, high-impact leak requiring urgent analysis.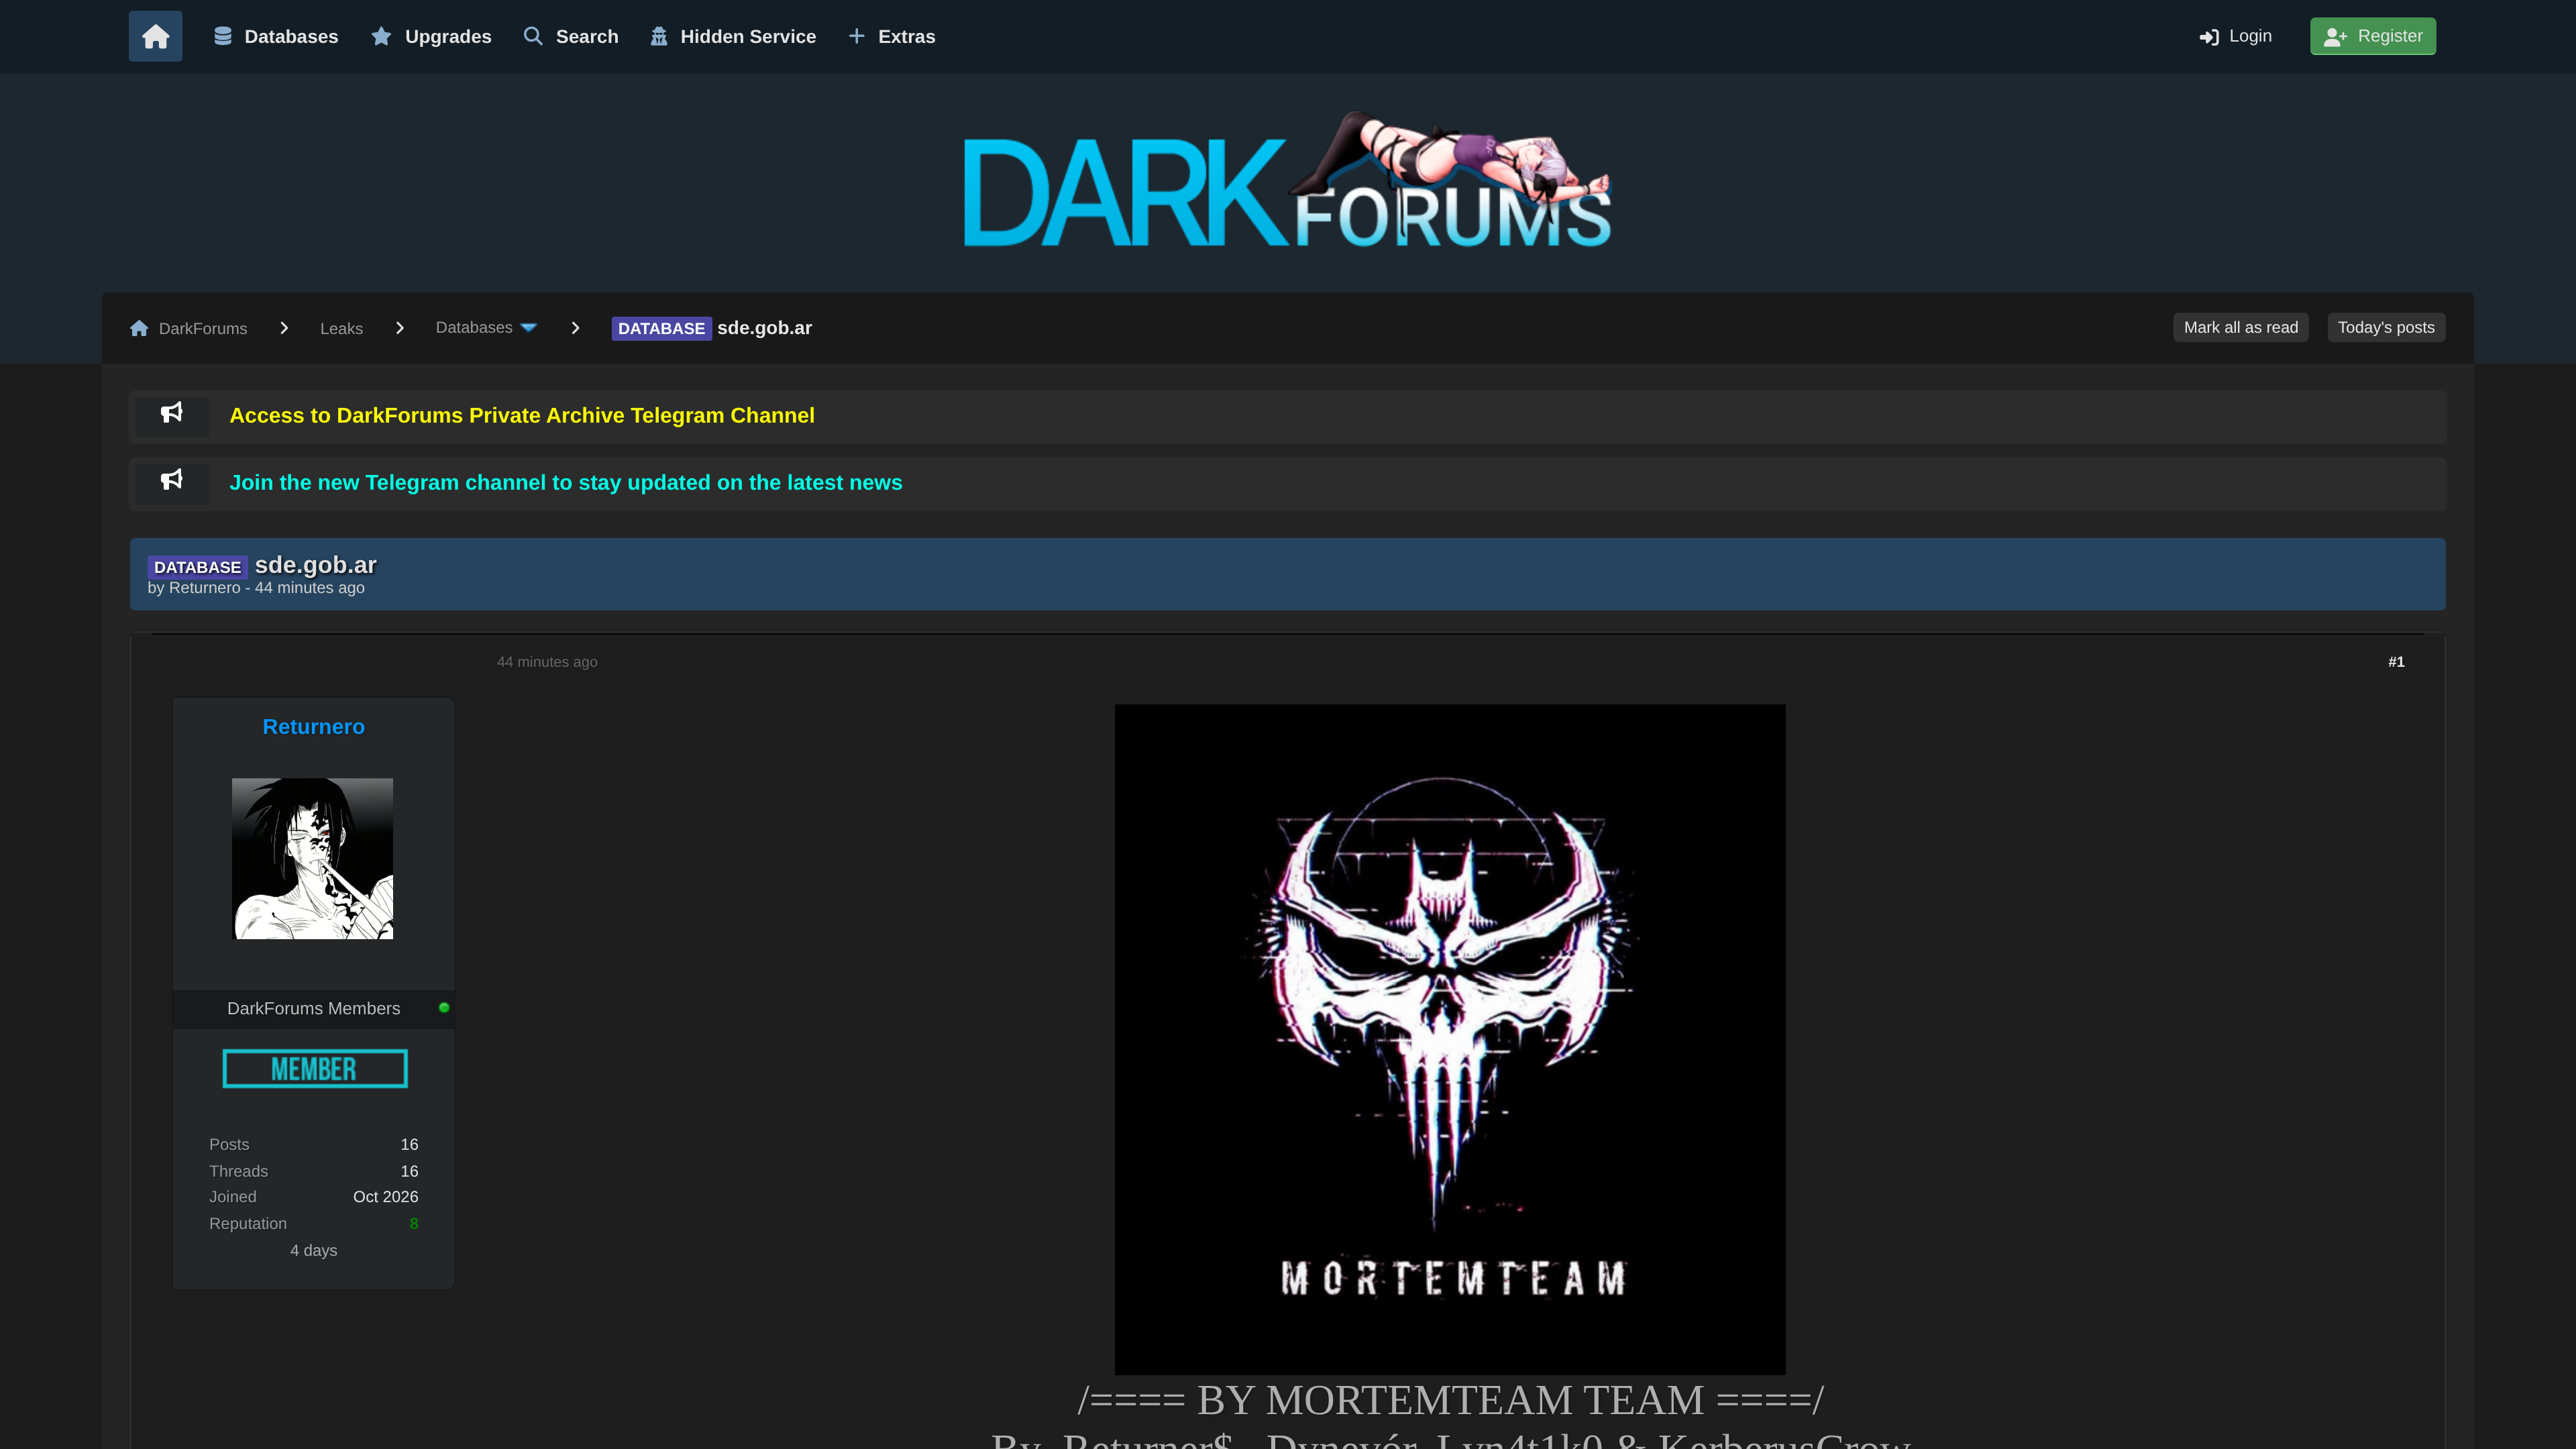
Gov / Military● 92
Filtración de base de datos del dominio gubernamental sde.gob.arThe actor 'Returnero' published a database from the Argentine government domain sde.gob.ar on a criminal forum just minutes ago. Exposure of a .gob.ar entity can enable targeted phishing, impersonation and further intrusion against state systems. Given its government origin, it warrants immediate verification and notification to Argentine authorities.