BRIEFLeakhighP63
Leak of 700,000 CUPS records from Spain's energy sector
Sector energético español (CUPS)
Detected22 October 2026 · 20:36 UTC
A 700K-record database of Spanish CUPS electricity supply-point codes paired with mobile phone numbers has been posted for download. CUPS codes uniquely identify energy contracts and premises, so combining them with phones enables targeted phishing, fraud and account takeover against utility customers. Defenders in the Spanish energy sector should treat this as a confirmed exposure and warn affected customers.
CategoryLeak
Severityhigh
Priority score63
Detected22 October 2026 · 20:36 UTC
Leak● 73
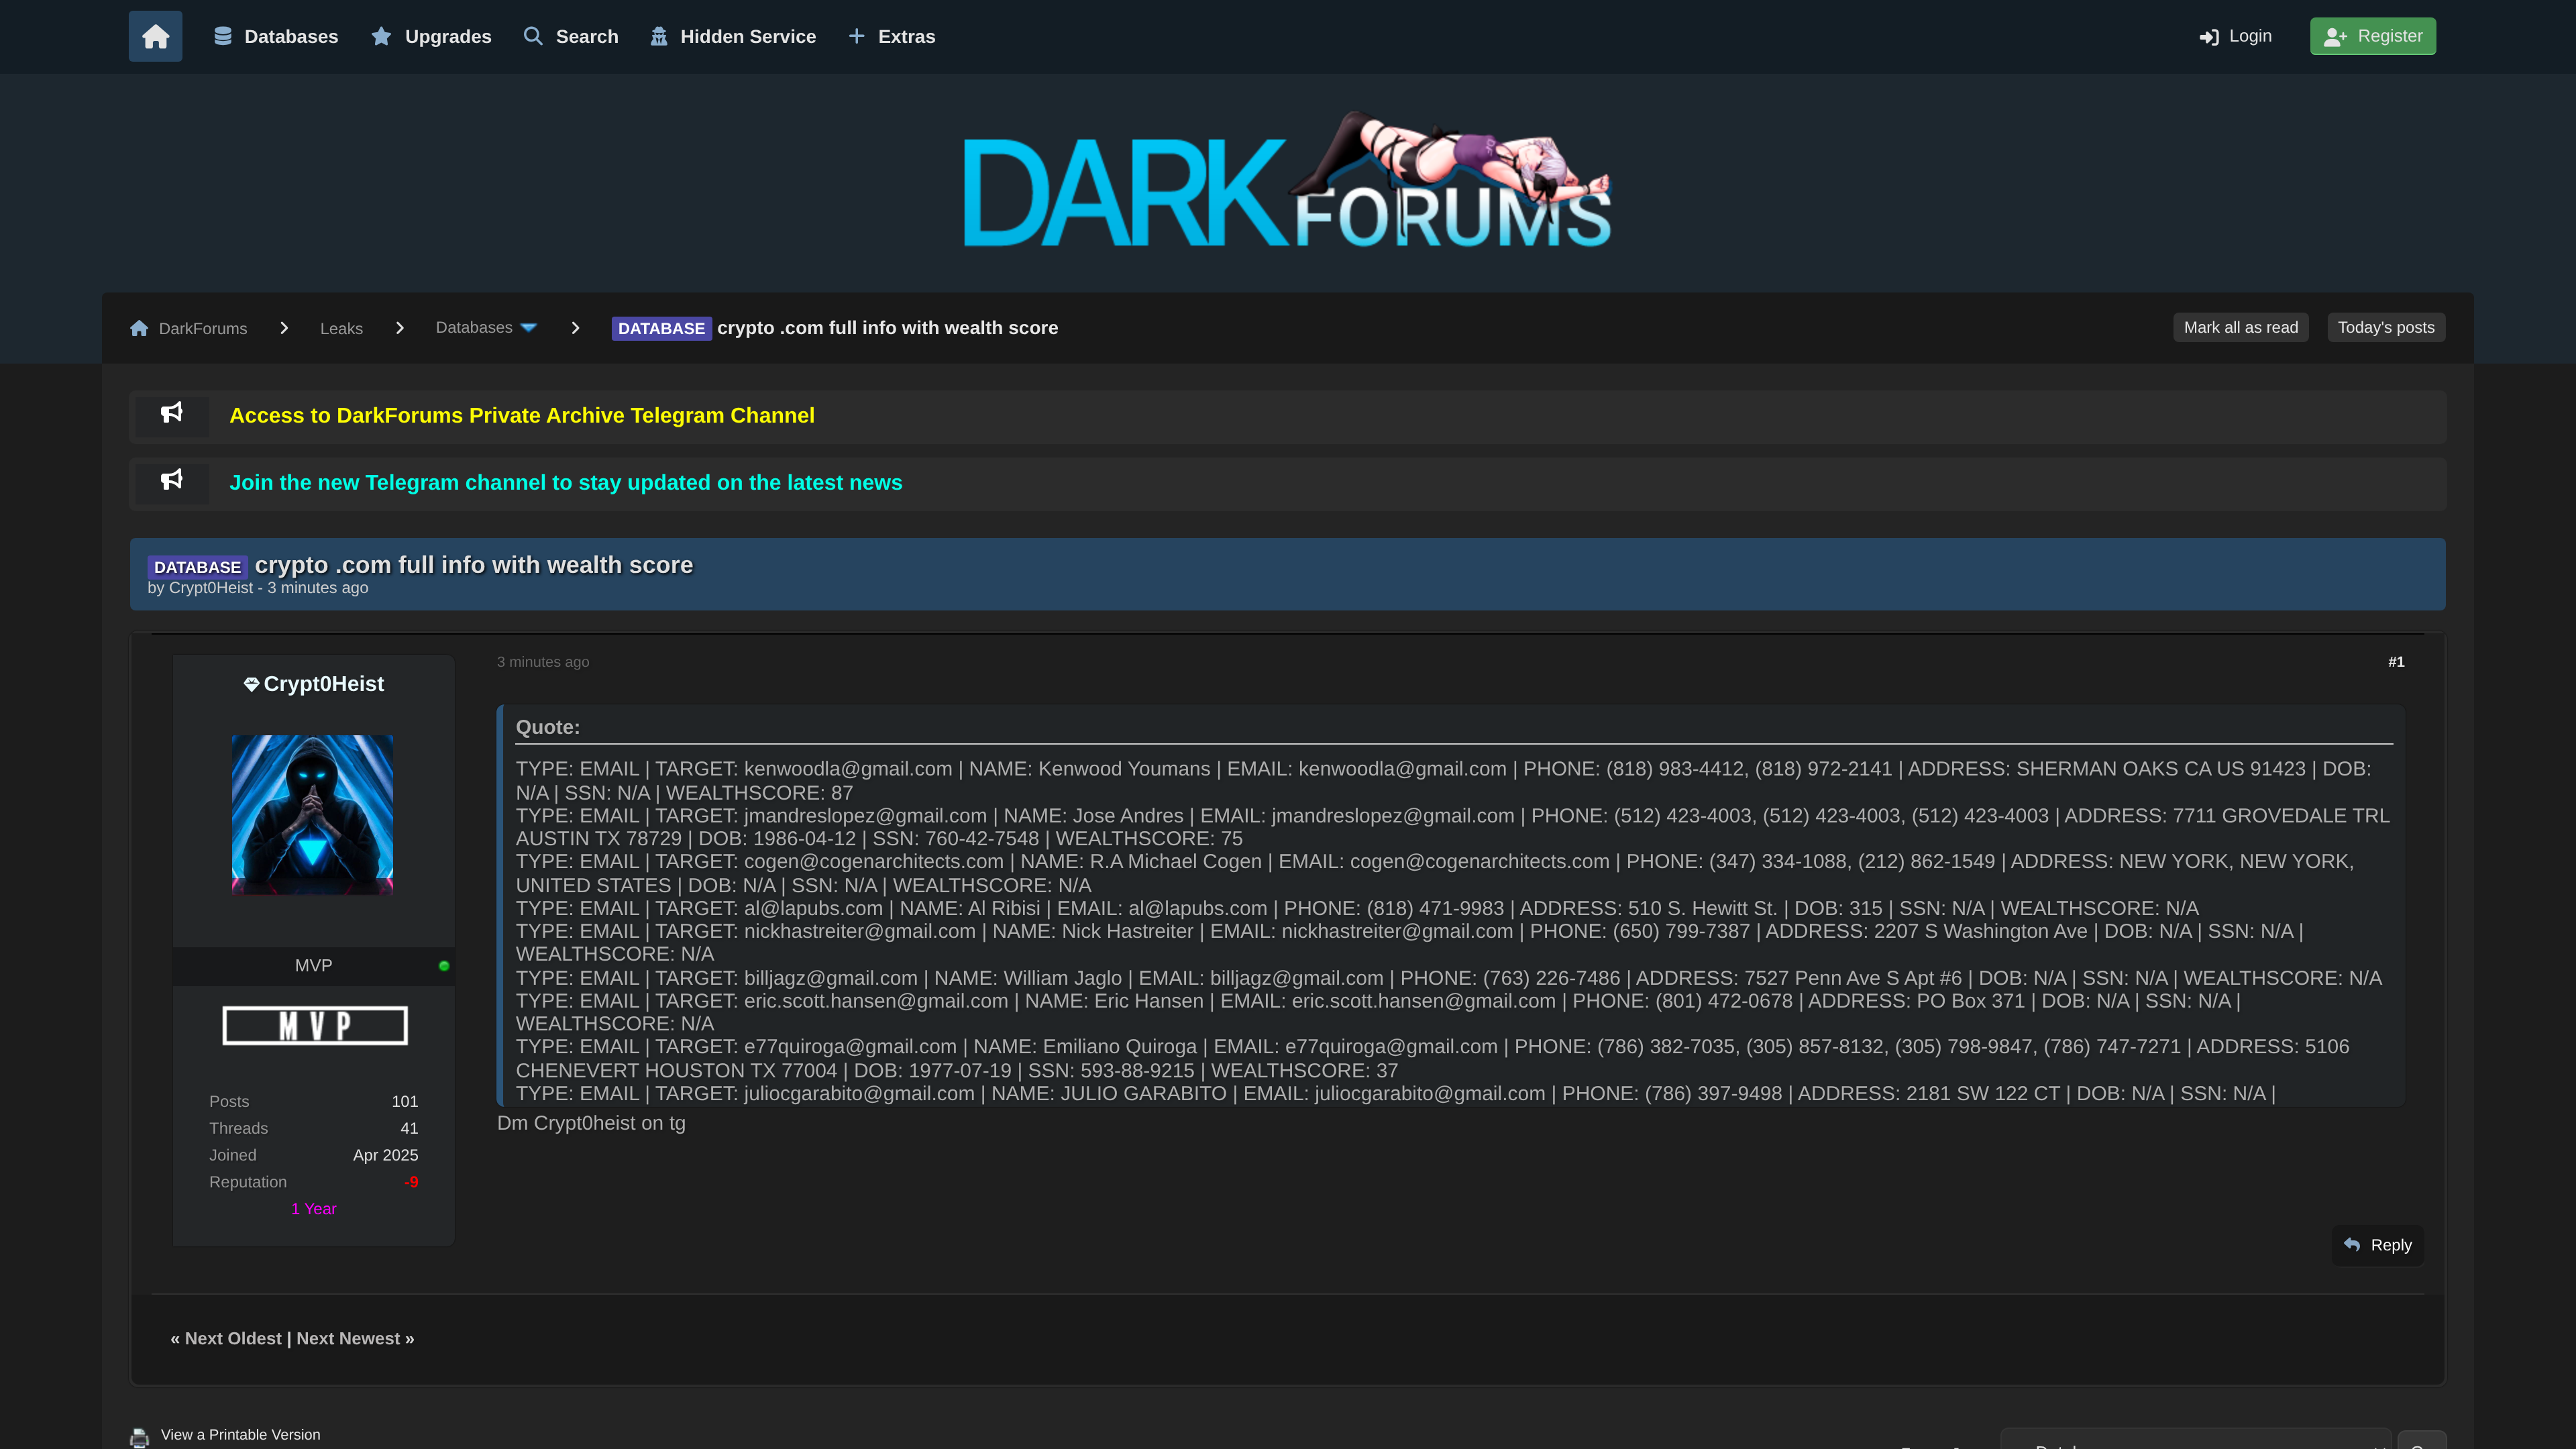
Base de datos de usuarios de Crypto.com con info completa a la ventaA seller posted a Crypto.com user database containing full personal details plus a 'wealth score', freshly published on 22 Oct 2026. This lets attackers rank and prioritize high-net-worth exchange account holders for phishing, SIM-swap and account-takeover attempts against crypto funds. Exchange customer data is high-value because it enables direct financial theft and targeted social engineering.Leak● 44
Base de datos del sistema sanitario de farmacias de Turquía filtradaA repost claims to leak a database from Türkiye's pharmacy/health system, exposing sensitive patient and prescription-related data. Health records are high-value for fraud, identity theft and social engineering, and the data likely persists across mirror reposts. The 'repost' framing suggests it is not fresh, so it is worth monitoring rather than alerting urgently.Leak● 35
Filtración de archivos del Gobierno de Coahuila, MéxicoA repost of a file/document leak attributed to the Government of Coahuila, Mexico, first surfaced around late 2022. It exposes internal public-sector documents relevant to defenders tracking Mexican government exposure. However, the material is years old, so treat it as historical context rather than a fresh incident.Leak● 36
Volcado de 4,4 millones de registros URL:LOG:PASS a la ventaA 4.4 million line corpus of URL:login:password entries, described as private and UHQ, is being distributed on NulledBB; this format matches infostealer log output rather than a single-vendor breach. Because entries are keyed to specific login URLs, they can be replayed directly against corporate VPN, webmail and SaaS portals. There is no named victim or date, so treat it as background credential-stuffing risk rather than an incident.Leak● 55
Filtración de datos de la turca Tera Group por hacktivistasA leak-section post published roughly 35 minutes ago claims that data from Tera Group, a Turkish industrial/energy conglomerate, was stolen and released by the 'MLKP Revolutionary Justice Hackers' collective. The thread cites press coverage and is presented as a full data dump, which in hacktivist cases often includes internal documents, email archives and employee information. Even though the victim is outside Latin America, ideologically motivated leaks of critical-infrastructure-adjacent firms frequently seed follow-on intrusion and credential abuse.Leak● 63
Filtración de la base de datos de Westrock CoffeeA forum user published a downloadable database allegedly belonging to Westrock Coffee, a US coffee trading and manufacturing company, under a 2026 tag. The posting is brand new (uploaded minutes ago), so contents and record count are still unverified, but corporate datasets of this type typically carry employee accounts, business contacts and internal operational data. Defenders at food-and-beverage or commodity supply-chain firms should treat it as a potential credential and partner-data exposure and monitor for reuse.