BRIEFLeaklowP20
Texas-Blooms.com customer database leaked
Texas-Blooms.com
Detected11 September 2026 · 15:12 UTC
A customer database for the flower retailer Texas-Blooms.com was posted for free download, apparently including customer contact and order data. The target is a small US e-commerce site and the post is dated early 2026, so it is stale and low priority. The leaked PII still presents a phishing and account-takeover risk for affected customers.
CategoryLeak
Severitylow
Priority score20
Detected11 September 2026 · 15:12 UTC
Leak● 50
Filtración de base de datos del Central Bank of IndiaA user 'KillerRabbit' claims to have shared a compromised database of India's Central Bank of India containing addresses, phone numbers, and email addresses. If authentic, this exposes customer and contact data of a major state-owned bank, enabling phishing and account-takeover attempts. Recency is unconfirmed, but the named financial target makes it worth validating.Leak● 70
Base de datos de leads de Bittools.es (España) de 8,2M+ a la ventaA forum user (Mr_Racco...) is advertising an 8.2M+ Spanish business/lead database derived from Bittools.es on BreachForums. The dataset likely contains company and contact records usable for targeted phishing and B2B fraud across Spain. Sales of large curated lead sets enable widespread social engineering against Spanish organizations.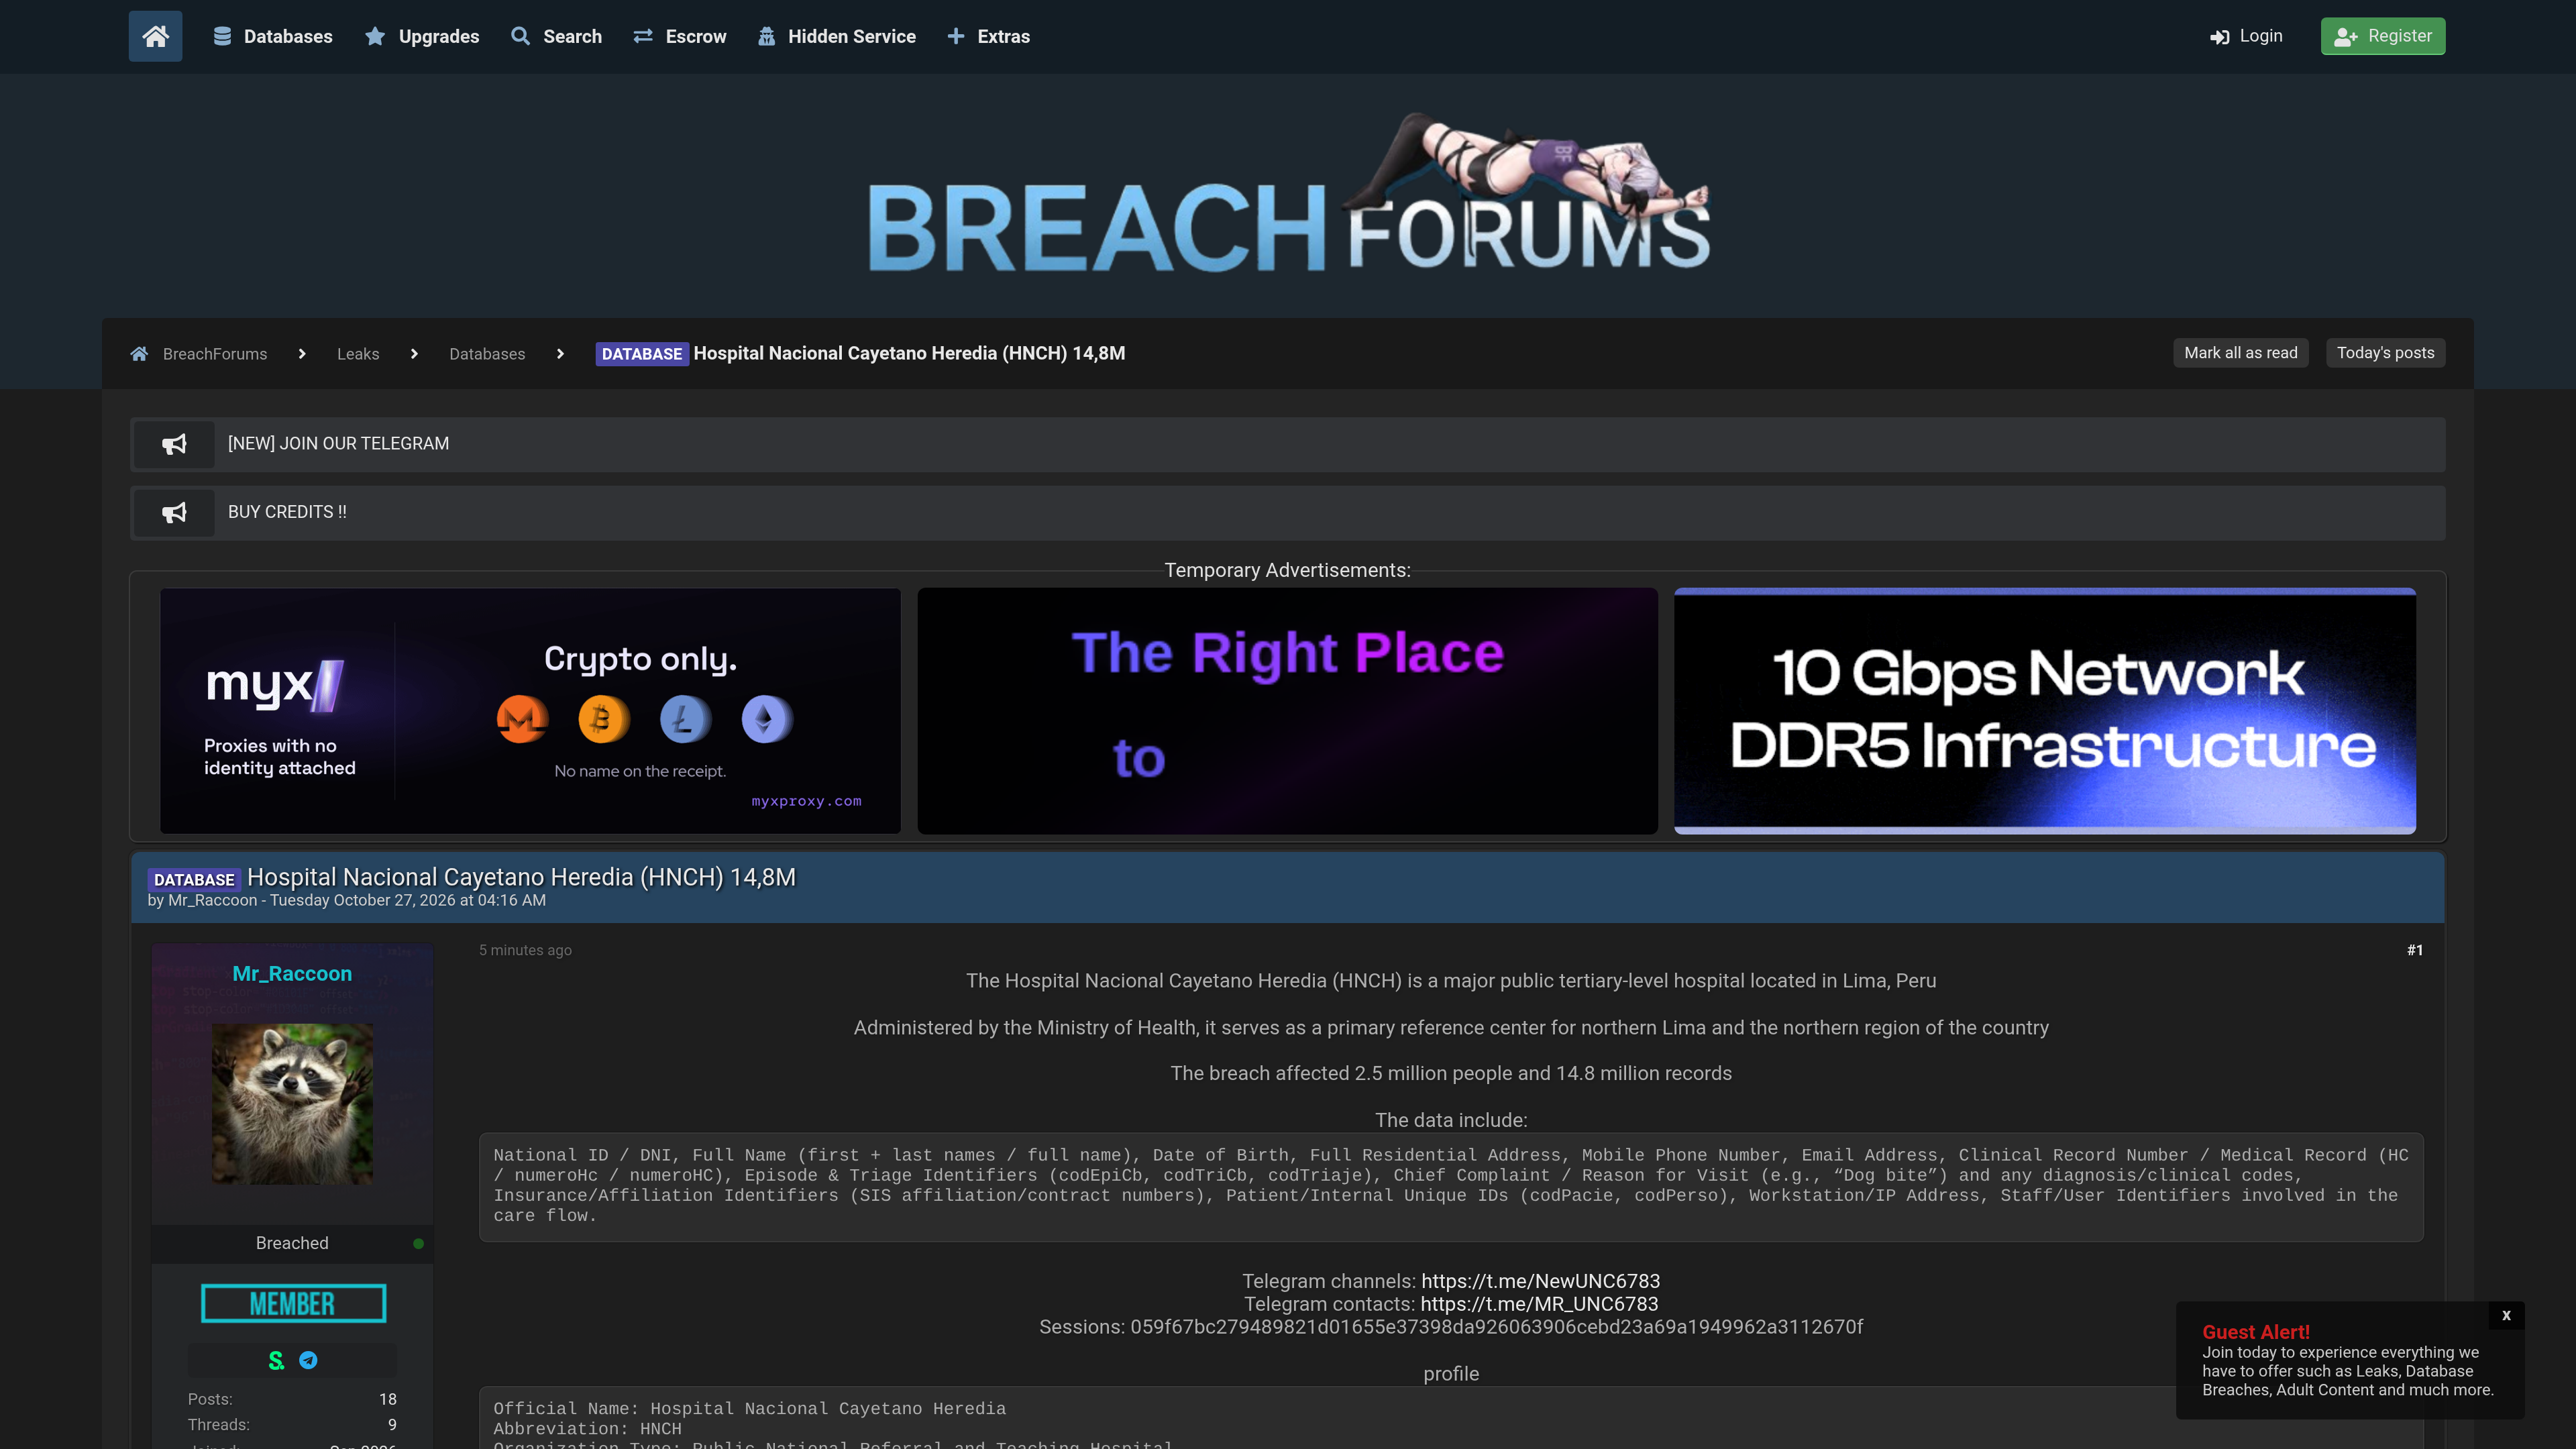
Leak● 82
Filtración de base de datos del Hospital Nacional Cayetano Heredia (Perú)A 14.8M-record database attributed to Peru's Hospital Nacional Cayetano Heredia, a major public reference hospital, has been posted on BreachForums. The volume suggests patient and staff records, including potentially sensitive health and identity data. This is critical-infrastructure health data in Latin America and warrants immediate exposure assessment and notification planning.Leak● 28
Volcado de 44 GB con más de 60.000 archivos en NulledBBA 44 GB archive containing over 60,000 files was posted to the NulledBB dump section, potentially bundling large volumes of stolen or leaked data. The source and affected entities are not stated, so its relevance to any specific organization is unclear. Analysts should sample the archive and search for known corporate domains before dismissing it.Leak● 38
Combo privado de 11,7M URL:LOG:PASS circula en ForumTeamA private 11.7 million-line URL:LOG:PASS credential combo is being shared on the ForumTeam forum, giving attackers a large pool for credential-stuffing and account takeover against web-facing logins. No specific organization, sector or country is named, so the exposure is broad and untargeted. It still enables automated attacks against any service whose users reuse these credentials.Leak● 72
Filtración de base de datos de usuarios de 1win EcuadorA BreachForums user publishing as 'pheisito' posted a thread titled 'DATABASE 1WIN ECUADOR HACKEADO' on 27 October 2026, offering a customer database belonging to the betting platform's Ecuadorian operation. Although the exact record count is not visible, betting-platform dumps typically contain names, identity documents, phone numbers, emails and payment details of local users. For defenders in Ecuador this is a fresh, potentially large PII exposure that enables account takeover and identity fraud against a broad consumer base.