Underground · what matters today
The underground stories that broke through this window. Gov/mil, access sales, ransomware, leaks, stealers. Screenshots and context on each.
Distribution by category · window
- Gov / Military51
- Access sale27
- Ransomware17
- Leak382
- Stealer0
- Other4
Window
Category
Severity
Venta de brecha del Centro Médico Especializado OSI de Perú
Centro Médico Especializado OSI (Perú)
An actor is selling data from Centro Médico Especializado OSI, a Peruvian healthcare provider, exposing patient and clinical information. Health-sector breaches in LATAM enable medical fraud and targeted extortion, and this one hits a regional critical-service provider. Confirm the scope and date to assess urgency.
Venta de brecha de Meducar, telemedicina y gestión de pacientes (3,1 M)
Meducar
A seller offers 3.1 million records from Meducar, a telemedicine and patient-management platform, indicating a large exposure of clinical and personal data. Healthcare records are high-value for fraud and extortion, and the breach affects a LATAM-facing provider. Verify the dataset's authenticity and whether local patients are implicated.
Venta de 1,73 TB del sistema de telemedicina ConsultorioMovil
ConsultorioMovil
An actor is selling 1.73 TB from ConsultorioMovil, a telemedicine and healthcare-management system used across Latin America, likely including patient records and clinical data. This is a large, sensitive health-sector dataset that enables identity theft and targeted fraud. Defenders should verify whether their organization's data is included and prepare patient notifications.
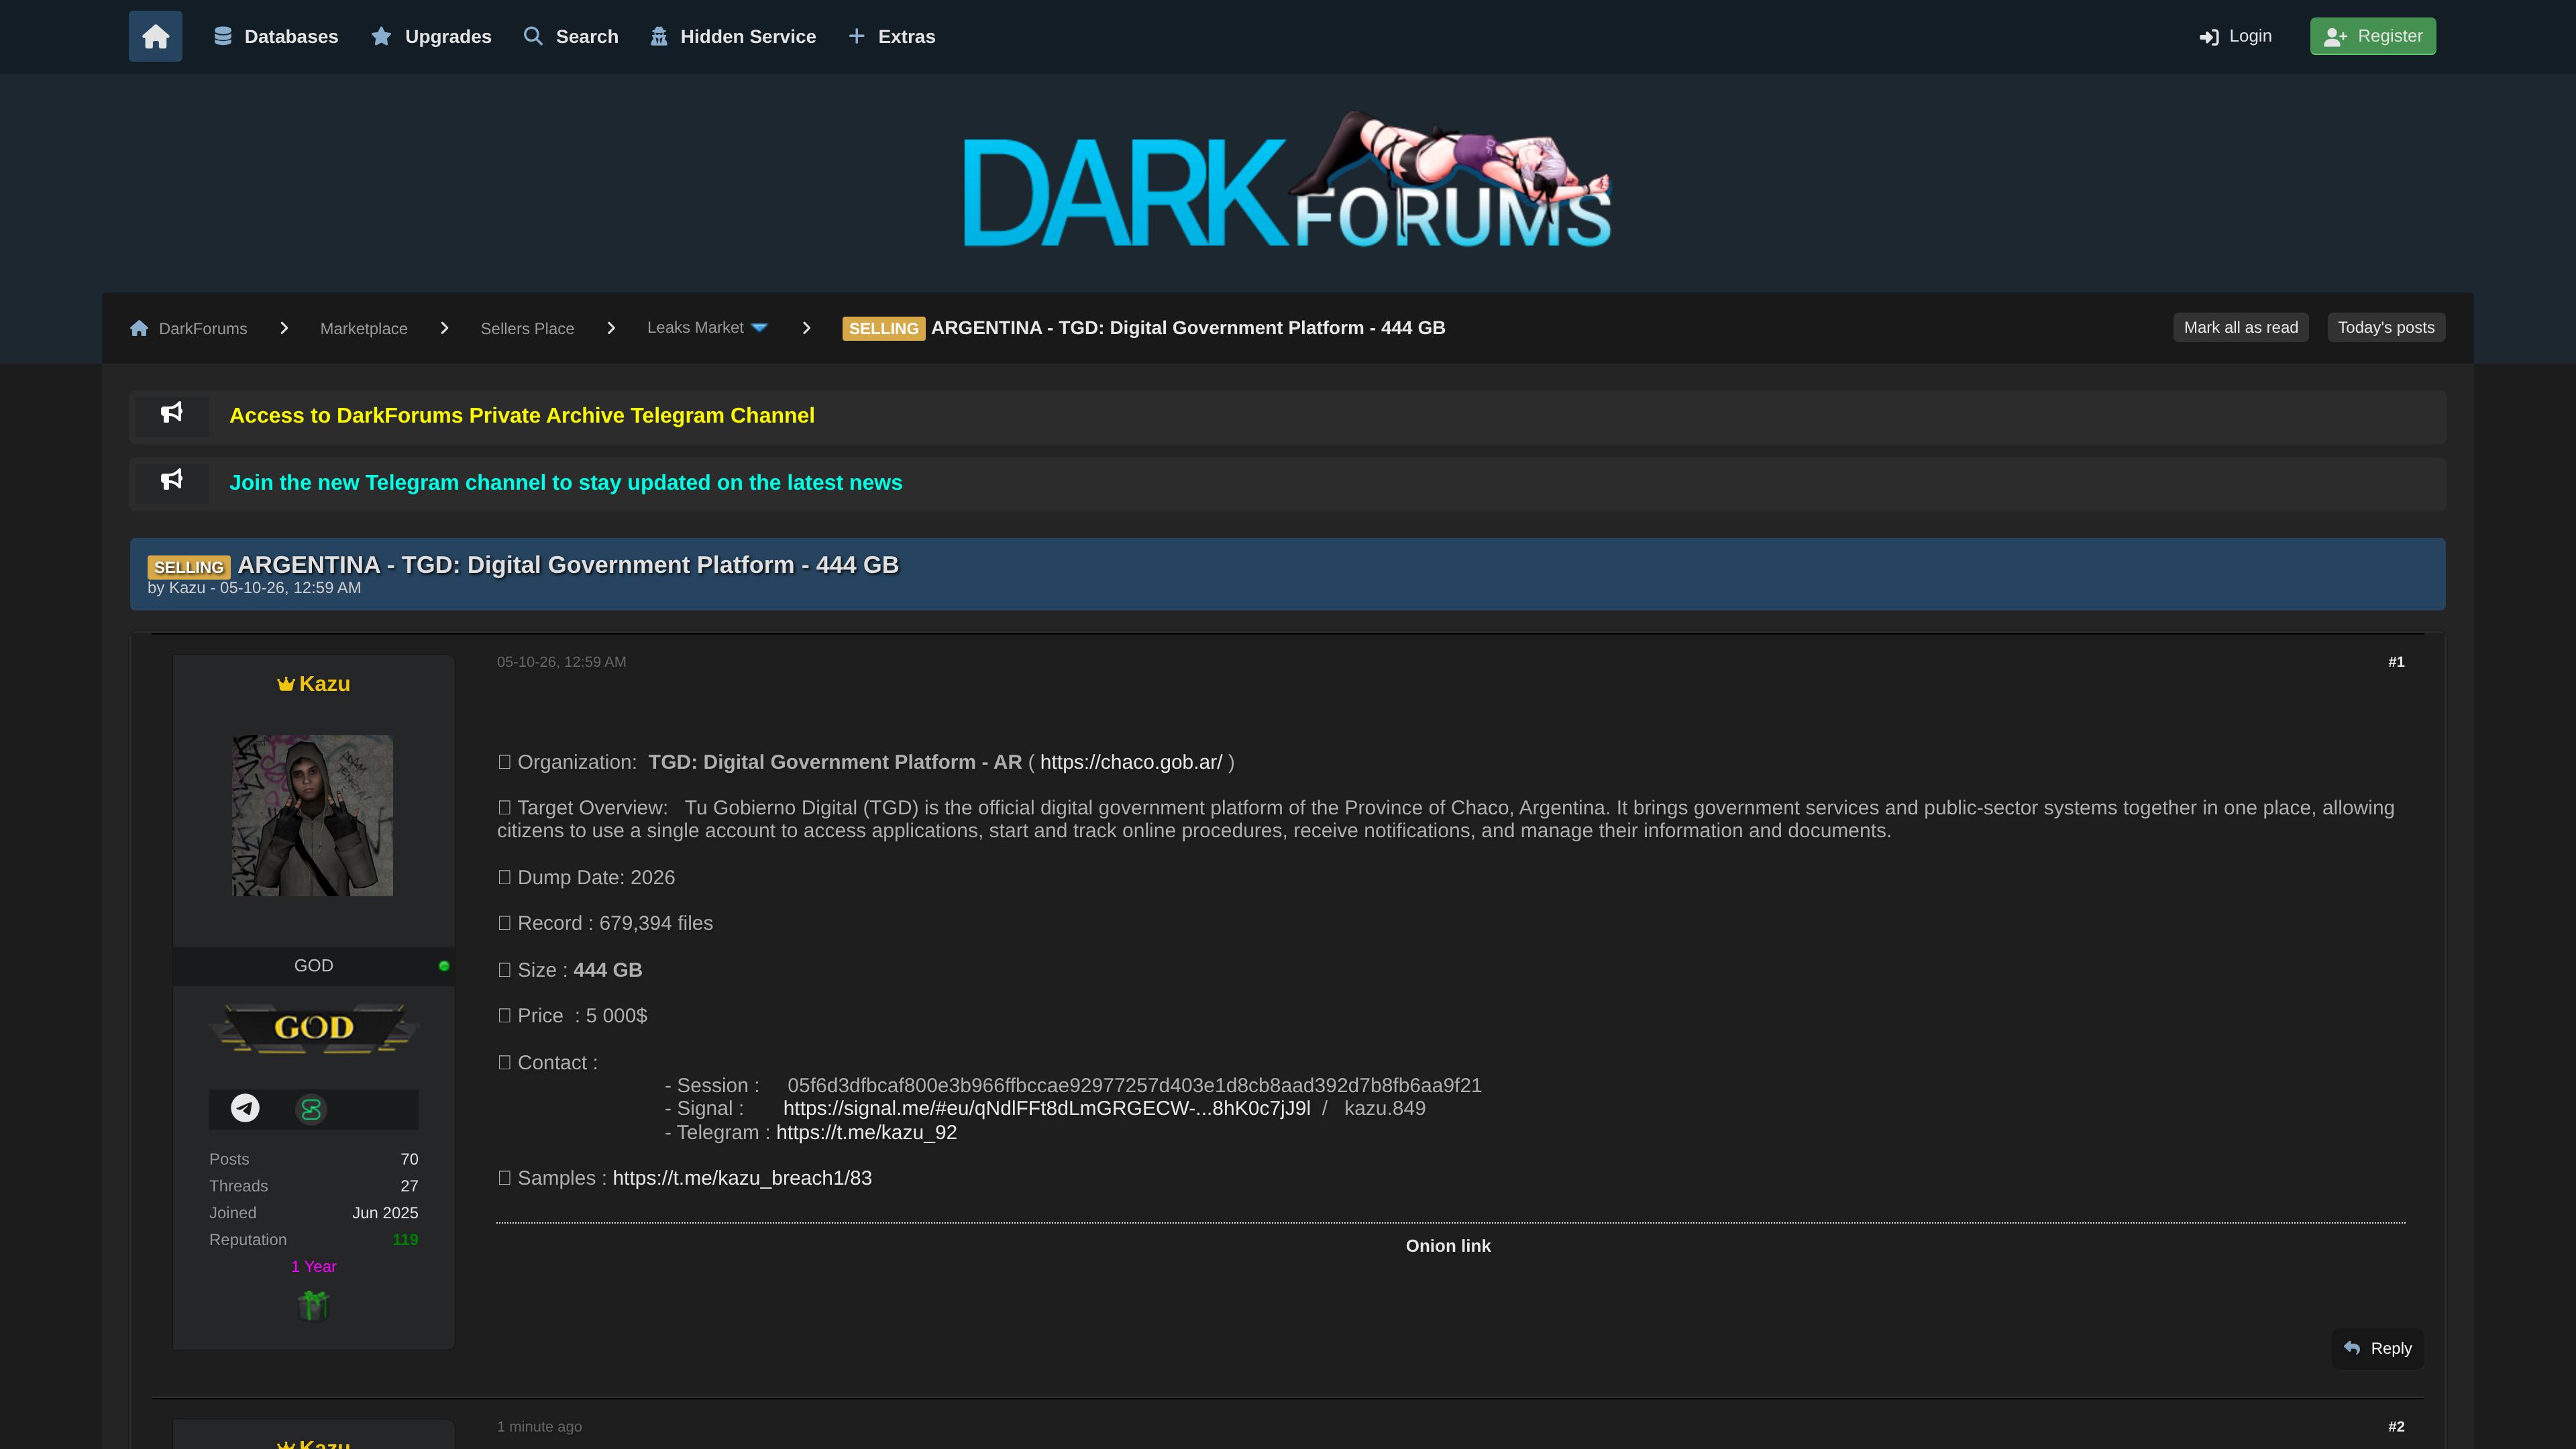
Venta de 444 GB de la plataforma de gobierno digital TGD de Argentina
Argentina - TGD Digital Government Platform
An actor is selling 444 GB allegedly taken from Argentina's TGD digital government platform, which could contain citizen records, credentials and internal administrative systems. This is national-level critical infrastructure, so if authentic it demands urgent verification, access-log review and credential-reset planning. Confirm the leak date and scope to gauge the real exposure.
Venta de base de datos sanitaria PappyJoe India (413 GB)
PappyJoe (India)
A 413 GB database attributed to PappyJoe, an Indian healthcare-management system, is being sold online. Health-sector data of this size can expose patient records and provider credentials, fuelling fraud and downstream attacks. It is relevant for defenders tracking large medical-data leaks, though outside LATAM.
Venta de la base de datos de HealthDaq Irlanda (431 GB)
HealthDaq (Irlanda)
A 431 GB dataset linked to Ireland's HealthDaq is listed for sale. Large health and insurance datasets can expose patient and policyholder information, enabling identity theft and targeted scams. It is worth noting for defenders monitoring major health-data leaks, even though it sits outside LATAM.
Venta de la base de datos de Yocale Canadá (6M registros)
Yocale (Canadá)
A threat actor is selling the database of Yocale, a Canadian appointment-management platform, with roughly 6 million records. Such data typically includes names, emails, phone numbers and scheduling details usable for phishing and account takeover. It matters as a sizable leak of a real SaaS provider, though it is outside the LATAM region.
Venta de la base de datos de MyVete (5,5M usuarios)
MyVete
The MyVete platform's database, reportedly covering 5.5 million users, is listed for sale. If confirmed, it exposes customer names, contact details and account data usable for phishing and account takeover. It matters as a sizable consumer-data leak, potentially of a Spanish-speaking user base.
Venta de datos del portal Statistics South Africa (154 GB)
Statistics South Africa
An actor is selling a 154 GB dataset attributed to Statistics South Africa, the national statistics agency. Government statistical data of this size can expose citizens' records and internal systems, aiding social engineering against public institutions. It is relevant to defenders tracking government-sector leaks, though outside LATAM.
Venta de una base de datos del gobierno de Israel
Gobierno de Israel
A dataset described as belonging to the Israeli government is being offered on BreachForums, posted today. Government data leaks can expose citizen records, official accounts and sensitive documents used for espionage and social engineering. It warrants attention for defenders tracking state-targeted leaks, even though it is outside the LATAM region.
Venta de datos del gobierno provincial de Gauteng (3,8 TB)
Gobierno Provincial de Gauteng
A 3.8 TB breach attributed to the Gauteng Provincial Government in South Africa is being offered for sale, an unusually large public-sector dataset. Such leaks expose citizen records, staff accounts and internal documents, enabling targeted attacks and social engineering against public services. It matters for defenders monitoring government-sector leaks, though it is outside LATAM.
Filtración de la brasileña Mobilemed: 52 millones de registros (23,5 TB)
Mobilemed (Brasil)
A seller offers 52 million records and 23.5 TB from Brazilian healthcare provider Mobilemed, implying massive exposure of patient and medical data. Health data is highly sensitive and regulated, and a leak this size enables fraud, extortion and phishing at scale. Though posted in July 2026, its scale keeps it operationally relevant for Brazil/LATAM defenders.
Base de datos de 64 GB con cuentas bancarias de EAU a la venta
A fresh DarkForums post advertises a 64 GB dataset of UAE bank account numbers, national IDs and phone numbers. The volume and the mix of financial and personal data make it prime material for account takeover, identity fraud and downstream BEC. Banks and KYC providers should expect credential-stuffing and fraud spikes tied to this data.
Filtración de la base de datos de Luxottica para descarga
Luxottica
A RaidForums thread spanning multiple pages is distributing a downloadable database attributed to Luxottica, the global eyewear group behind Ray-Ban and Oakley. If genuine, it exposes customer and business data of a major multinational, usable for phishing, credential abuse and fraud. Identity and retail defenders should verify the exposure and monitor for downstream abuse.
Base de datos francesa UNSS con más de 7 millones filtrada
UNSS (French school sports union)
A database labeled 'UNSS' with over 7 million records is being shared, likely tied to French school/university sport. Millions of records can include names, addresses, dates of birth and contact data of students and staff. Its scale makes it a valuable asset for identity fraud and phishing even if posted months ago.
Colección de filtraciones de federaciones deportivas francesas
French sports federations
A collection of leaked databases from multiple official French sports federations has been posted for download. These federations hold member, licensing, medical and staff records, so aggregating them amplifies exposure across several organizations at once. It matters for tracking a coordinated leak campaign against French sporting bodies.
Base de datos del bufete Prater & Ridley filtrada
Prater & Ridley Attorneys At Law
A database belonging to the US law firm Prater & Ridley Attorneys at Law has been posted for download on a RaidForums mirror. Law-firm data typically contains client identities, matter details and contact records, exposing legal-sensitive information. It matters for defenders tracking law-firm targeting, a common ransomware and BEC precursor.
Filtración de datos KYC del casino LeoVegas (2025)
LeoVegas
An actor is sharing 1,300+ files from LeoVegas containing KYC documents, account balances, emails and source code. KYC and balance data are high-sensitivity and feed identity theft and account takeover against a regulated gambling operator. Dated 2025, it is a stale leak for alerting but still useful as background on the operator's exposure.
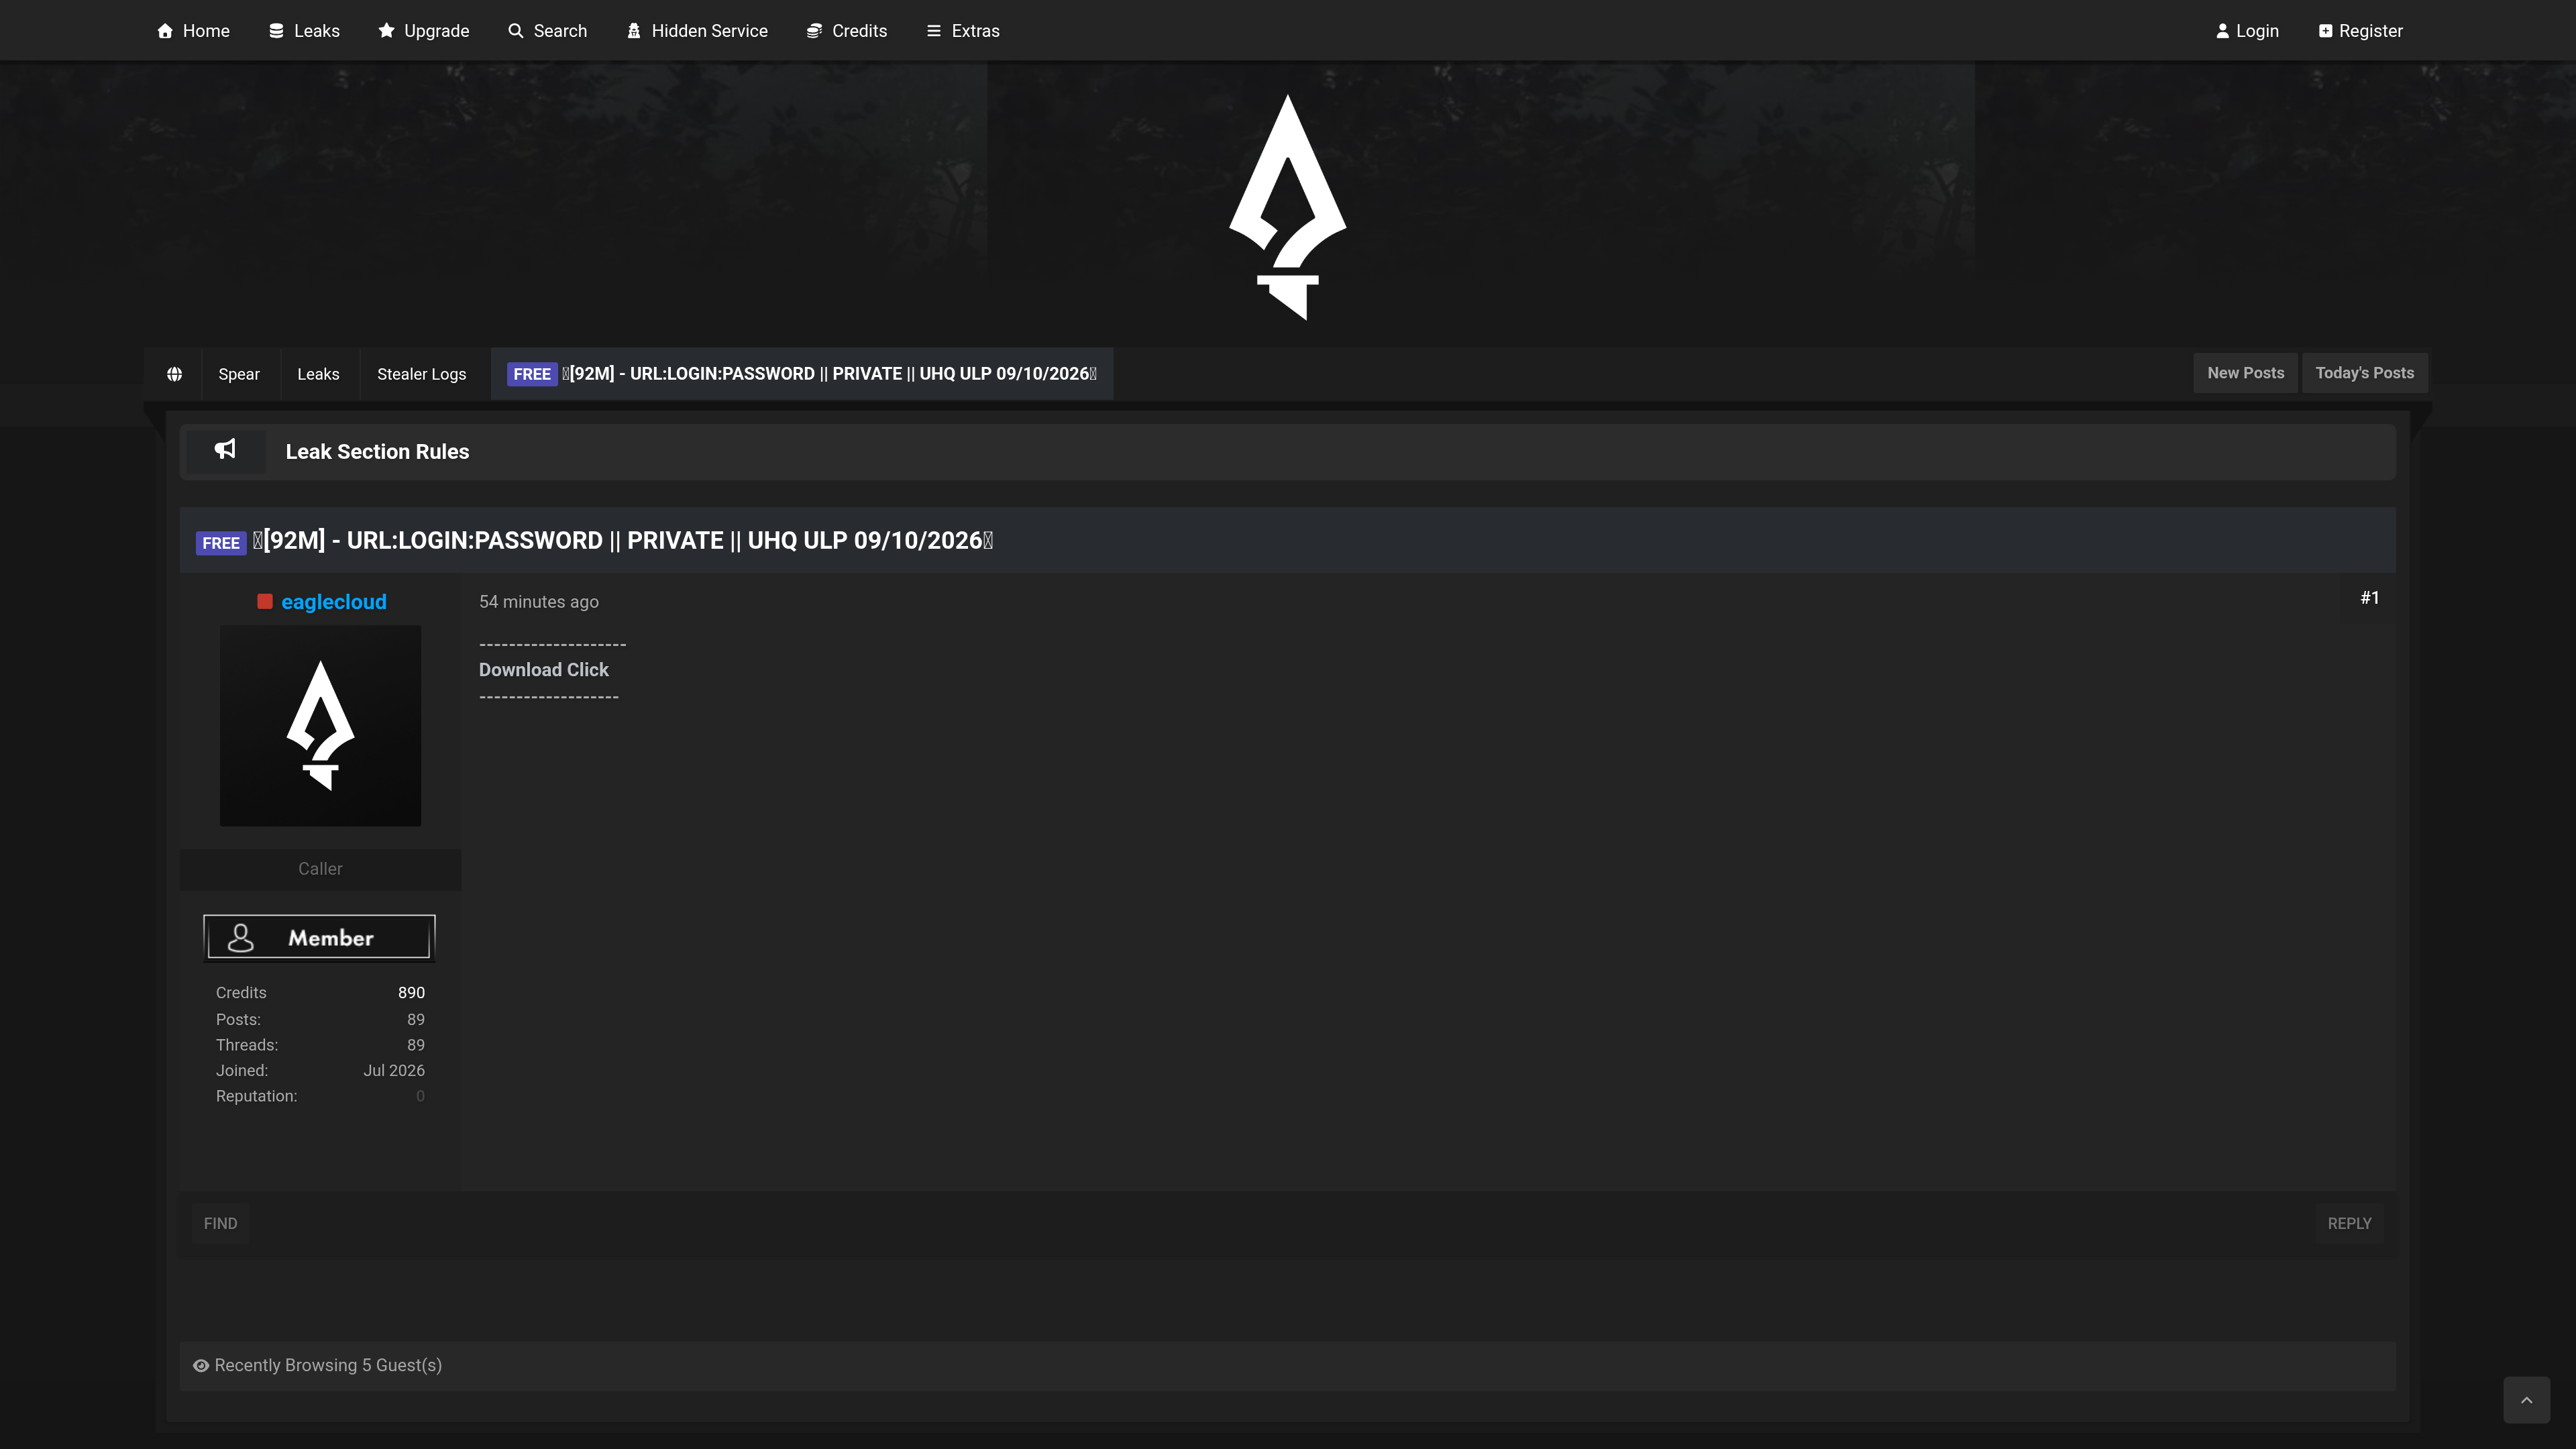
Filtración de 92 millones de credenciales URL:login:password
A freshly posted dump of roughly 92 million URL:login:password (ULP) records, harvested from infostealer logs, was released privately and marked as high quality. A set this large and recent fuels credential-stuffing, account takeover and session hijacking across web services worldwide. Defenders should hunt for reuse of these credentials and force resets on any exposed corporate accounts.
Filtración de base de datos de Vodafone 2026
Vodafone
A forum thread offers a Vodafone database leak dated mid-2026, a major global telecom operator. While the content could be significant, the post is roughly four months old, so it is not a fresh alert. It still matters for defenders tracking subscriber-data exposure across telecom providers.
Brecha de datos sanitarios de la empresa Woundtech
Woundtech
A raid forum thread advertises a fresh healthcare data breach at Woundtech, a US wound-care provider. Healthcare data is among the most sensitive, including patient identities and possibly medical records. Fresh medical leaks enable medical identity theft and targeted extortion, warranting immediate triage for defenders.
Base de datos de Phone House con más de 13 millones de registros
Phone House
A raid forum post published today offers a Phone House database of more than 13 million records. Phone House is a large European mobile-phone retailer operating in Spain and other countries, so the leak likely exposes customer names, contact details and purchase data. Such a volume is high-value for fraud, credential-stuffing and targeted phishing campaigns.
Filtración de datos de 7,5 millones de clientes de Momentum Telecom
Momentum Telecom
A forum database dump claims 7.5 million customer PII records from Momentum Telecom, a large US business-ISP and voice provider. The data appears fresh (posted the previous day) and typically includes names, addresses and contact details. Leaked telecom subscriber data fuels SIM-swap, phishing and account-takeover attacks, so it matters for defenders in the sector.
Filtración de historiales de pacientes del grupo portugués CUF
www.cuf.pt
A dataset of roughly 263,000 patient records from Portuguese healthcare group cuf.pt is being offered, including contact and demographic data. Health data is among the most sensitive categories, enabling targeted fraud and extortion. It is a confirmed named-organization healthcare leak worth surfacing.