Underground · what matters today
The underground stories that broke through this window. Gov/mil, access sales, ransomware, leaks, stealers. Screenshots and context on each.
Distribution by category · window
- Gov / Military50
- Access sale28
- Ransomware17
- Leak385
- Stealer0
- Other4
Window
Category
Severity
Base de datos del FCI Bank filtrada en foro
FCI Bank
A fresh DarkForums post advertises a leaked FCI Bank database, implying exposure of financial customer records. Banking datasets enable fraud, identity theft and credential attacks against the institution and its clients. The affected region and exact entity are unclear, so it is flagged for verification but still worth surfacing as a named financial leak.
Filtración de datos internos de Uber (uberhub, 20 M)
Uber (uberinternal.com)
A thread advertises data tied to uberhub.uberinternal.com with a claimed scale of over 20 million records. Internal corporate infrastructure data of this size can expose employee accounts, MDM and internal tooling, aiding lateral movement and follow-on intrusions. It merits attention for access and leak monitoring even though Uber is not a LATAM entity.
Filtración de datos de Air Miles España (travelclub.es)
Air Miles España S.A (travelclub.es)
A database belonging to Air Miles España (travelclub.es), a Spanish loyalty and travel programme, is offered in a DarkForums leak thread. Such datasets typically contain personal data and account credentials of many members, enabling fraud, phishing and loyalty-point abuse. It matters for Spanish-speaking victims and for tracking a named corporate leak.
Filtración completa de la operadora Odido (Países Bajos)
Odido (Países Bajos)
A post claims a full leak of Odido, a major Dutch telecom operator, a critical-infrastructure sector where data exposure is especially damaging. Telecom breaches expose subscriber data, SIM and account controls, enabling fraud and SIM-swap attacks. Even outside Latin America it is directly relevant to access/leak monitoring and worth surfacing for peer telecom defenders.
Filtración de base de datos de la brasileña Privalia
Privalia (Brasil)
A large set of roughly 1.8 million Privalia Brasil credentials (URL and password) is being shared on DarkForums, indicating a substantial retail database leak in Latin America. Privalia is a major fashion e-commerce brand in Brazil, so the exposed logins enable account takeover, fraud and reuse against other services. Regional defenders should force resets and watch for credential-stuffing and phishing leveraging this dataset.
Filtración de datos de Santander México: 7 millones
Santander México
A threat actor is re-sharing a database allegedly holding 7 million Santander México customer records, with a new download link posted recently. Santander is one of Mexico's largest banks and part of the financial critical infrastructure, so exposure of customer and financial data fuels fraud, account takeover and targeted phishing. Defenders should treat this as an active redistribution and monitor for credential-stuffing against banking services.
Filtración de base de datos del sitio español airedefiesta.es
airedefiesta.es
A database belonging to Spanish site airedefiesta.es is offered. It is a small services site, so impact is limited, but Spanish-language victim data retains regional relevance. It should be verified and, if confirmed, reported for data-protection follow-up.
Volcado masivo de 384 bases de datos SQL (31GB)
A 31GB bundle of 384 SQL database dumps is posted. Aggregated dumps of this size often underpin credential-stuffing and account-takeover waves. Targets are unattributed, so the value lies in monitoring whether regional entities appear among the dumps.
Base de datos de Canva publicada a la venta
Canva
A 'Canva.com database' is being posted for sale or leak. Canva is a global design platform with hundreds of millions of users, so authentic customer data would enable phishing and credential reuse. The post appears to be a repost of older material, so treat as stale until freshness is confirmed.
Base de datos de clientes de la marca Under Armour a la venta
Under Armour (underarmour.com)
A customer database linked to US sportswear brand underarmour.com is offered for sale. Retail customer records support credential stuffing, phishing and account-takeover campaigns. Scale is unconfirmed, but the brand's size makes it worth monitoring for downstream fraud.
Filtración de cédulas de identidad de Trinidad y Tobago
Trinidad and Tobago citizens
A leak of Trinidad and Tobago citizens' national ID cards and scans is being offered. Government-issued identity documents enable identity theft, synthetic-identity fraud and bypass of KYC controls. Although outside Spanish-speaking LatAm, it is a sovereign identity breach that regional partners should track.
Filtración de 20 millones de registros de clientes del ISP Free.fr
Free.fr (Iliad)
A 43.5GB dataset containing roughly 20 million Free.fr (Iliad) customer records is being redistributed for free. Telecom customer data at this scale fuels SIM-swap fraud, credential stuffing and targeted phishing against subscribers. As critical telecom infrastructure, this warrants immediate validation and notification planning.
Filtración de base de datos del Instituto Nacional de Deportes de Chile
Instituto Nacional de Deportes de Chile (IND)
A poster is distributing a 1.72M-record database tied to Chile's National Sports Institute (IND, ind.cl), a public body under the Ministry of Sports. The dump likely exposes citizens' personal and contact data, creating phishing, impersonation and credential-stuffing risk. Chilean government defenders should verify the exposure, notify affected users and hunt for any leaked internal credentials.
Datos de 18.000 usuarios de Coinbase en foro de hacking
Coinbase
Roughly 18,000 records allegedly tied to Coinbase are being shared on DarkForums as a leaked archive. The volume is small relative to major breach dumps, but the crypto-exchange context raises credential-stuffing and account-takeover risk for affected users. Marginal priority; worth noting only for user-protection monitoring.
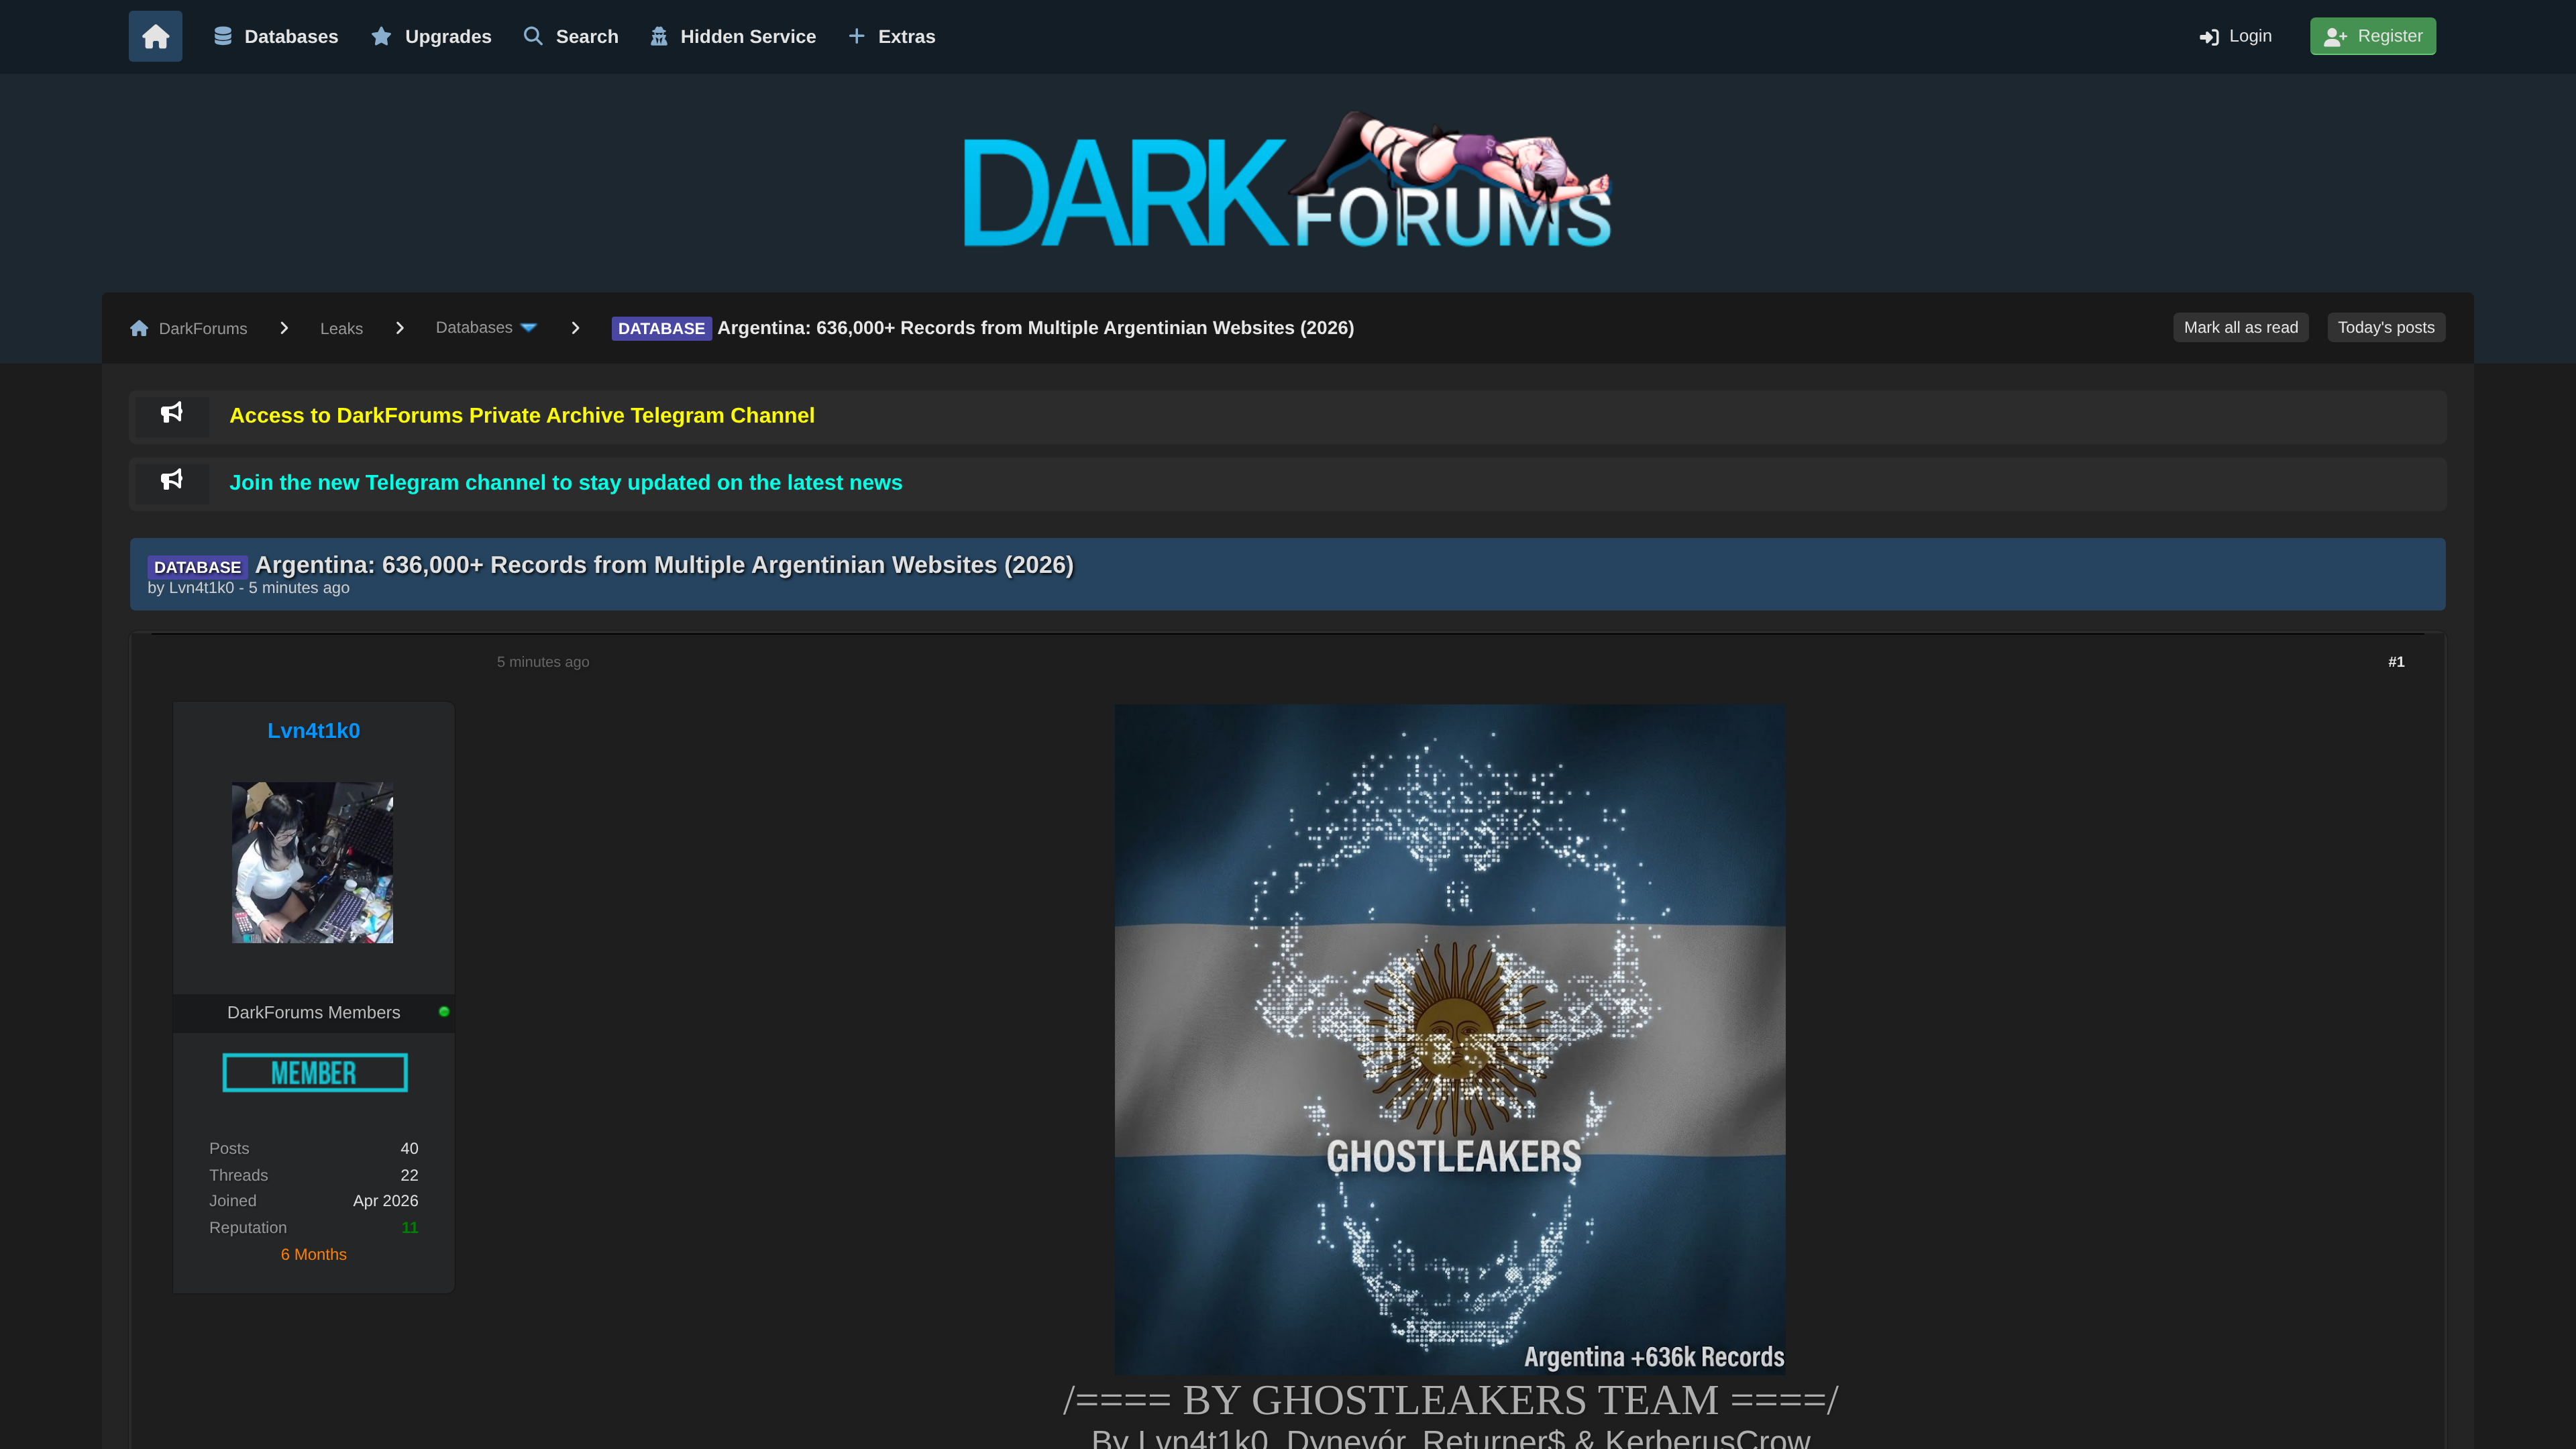
Filtración de 636.000 registros de sitios web argentinos
Múltiples sitios web de Argentina
A database of 636,000+ records allegedly aggregated from multiple Argentinian websites is being shared on DarkForums, dated 2026. Its scale and multi-source nature suggest credentials and personal data affecting local users and possibly public-sector portals, making it the most relevant item in this batch. Argentinian defenders should treat it as a fresh leak, correlate against their user bases and force credential resets.
Base de datos de la plataforma de reservas rolzo.com filtrada
rolzo.com
A fresh database belonging to rolzo.com, described as a premium booking platform, was posted on DarkForums by seller 'hundov' minutes ago. It likely contains customer accounts, emails and booking/PII data of the platform's users. If any of those credentials are reused, they expand the attack surface for account takeover and downstream fraud.
Filtración del código fuente privado de McDonald's
McDonald's
A threat actor is sharing what they claim is McDonald's private source code on a leak forum. Proprietary code can reveal internal logic, vulnerabilities and potentially embedded secrets or credentials, aiding follow-on attacks. The company should assess whether any keys or credentials were exposed.
Base de datos de lindyproperty.com (EE. UU.) a la venta
lindyproperty.com
A seller on Spear Forums is offering a 92,000-record database of the US real estate firm lindyproperty.com. Although the victim is outside Latin America, it is a real organization's customer/lead data going to market, useful for tracking broker activity and cross-referenced B2B phishing. Lower priority for AR-LATAM defenders but worth noting for regional brokers using the same data pipelines.
Filtración de la base de datos de Salesfloor.net
Salesfloor.net
A full database dump of Salesfloor.net, a US retail workforce platform, has been published on a leak forum. This exposes customer and employee data of a real company, enabling phishing and credential abuse against its users. Defenders should monitor for reuse of leaked identities in account-takeover attempts.
Filtración de base de datos de colaborador de Iberdrola (zirconite.es)
zirconite.es / Iberdrola
A 153,000-row database of zirconite.es, advertised as an official collaborator of Iberdrola — Spain's largest energy utility — is being shared on Spear Forums. The set exposes usernames, emails and likely client/contract records of a supplier to critical energy infrastructure. Treat this as supply-chain risk that could feed phishing or credential attacks against the Iberdrola ecosystem.
Brecha en LexisNexis expone datos de agencias gubernamentales de EE.UU. y despachos legales
LexisNexis
A threat actor claims a fresh breach of LexisNexis, exposing legal-intelligence data tied to US government agencies and law firms. This is high-value material that enables targeted social engineering, doxxing and credential abuse against legal and public-sector targets. Organizations relying on LexisNexis should watch for downstream phishing and verify account integrity.
Combolist de 1 millón de credenciales mexicanas
México (credenciales email:pass)
A recently posted combolist contains about one million email:password pairs reportedly tied to Mexico. While generic combolists are common, a dataset of this size focused on one country still fuels credential stuffing and account takeover against Mexican users and organizations. Defenders should enforce credential hygiene and block reused passwords.
Venta de datos de DNI y correos de ciudadanos argentinos
Argentina (DNI y correos)
A newly posted offer advertises Argentine lead data combining national ID numbers (DNI) with email addresses. DNI is a core national identifier, so this dataset is highly usable for identity theft, phishing and account takeover against Argentine residents and services. Defenders should monitor for credential abuse and warn affected individuals.
Filtración de 1,55 millones de datos de clientes de KFC Venezuela
KFC Venezuela
A fresh post offers roughly 1.55 million records of confidential information linked to KFC Venezuela, a major food-service operator in the country. The volume and recency suggest a recent breach exposing customer and possibly payment or identity data. Regional defenders and the company should treat this as an active leak and check for reuse of exposed data in fraud.