Underground · what matters today
The underground stories that broke through this window. Gov/mil, access sales, ransomware, leaks, stealers. Screenshots and context on each.
Distribution by category · window
- Gov / Military53
- Access sale41
- Ransomware53
- Leak411
- Stealer0
- Other10
Window
Category
Severity
Reportan compromiso de Gcore a través del panel ISPsystem
Gcore
A hosting community thread claims Gcore, a global cloud/CDN and hosting provider, was compromised through an ISPsystem control panel. If accurate, this means attacker control over provisioning infrastructure used by many downstream customers, including regional resellers and hosted services in Latin America. The claim is unverified and undated, so treat it as a lead to validate against Gcore's own advisories rather than confirmed fact.
Filtración de 780K registros de Brasil, parte 1 del lote de América Latina
Brasil (lote de datos de América Latina)
A forum actor is releasing a 780K-record Brazilian dataset explicitly framed as the first part of a Latin America collection, meaning further country batches (possibly Argentina) are likely to follow. Consumer and possibly corporate PII of this size fuels credential stuffing, phishing and identity fraud against regional users and service providers. Defenders in the region should treat it as an early warning and prepare for follow-on batches.
Datos de la OTAN supuestamente filtrados por SiegedSec
OTAN (NATO)
A fresh forum post claims the group SiegedSec has leaked NATO data, though the scale and contents are unverified and could be recycled material. Even so, a claimed leak tied to a defense/military alliance warrants rapid authenticity checks given past data-reuse by actors. Analysts should validate the dataset and monitor for downstream publication before treating it as confirmed.
Base de datos del gobierno de Sindh (Pakistán) con 10,6 millones de registros a la venta
Gobierno de Sindh, Pakistán (registro vehicular)
A forum user is offering a 10.6-million-record database tied to the Sindh provincial government (vehicle registration), posted within the last day. The scale indicates a mass exfiltration of citizen PII such as names, IDs, and registration details, enabling identity fraud and targeted attacks. Defenders in government vehicle/licensing services should verify the authenticity and treat exposed identifiers as compromised.
Base de datos de 109 millones de Turquía a la venta
Turkey (unspecified)
An onion forum offers a 109 million-record Turkish database for sale. The content and provenance are unverified because the thread is behind a login wall. If genuine, it is one of the largest national datasets in circulation and could fuel mass fraud and credential attacks.
Base de datos de 50 millones de Zenith Bank a la venta
Zenith Bank
A seller claims to be offering a 50 million-record database from Zenith Bank, a major Nigerian financial institution. The listing sits behind a forum login wall, so provenance and freshness are unverified. If authentic, a banking dataset of this scale would enable account-takeover, fraud and credential-stuffing campaigns.
Filtración de datos de Coca-Cola FEMSA en foro clandestino
Coca-Cola FEMSA
A forum user posted a leak labeled Coca-Cola FEMSA, one of Latin America's largest bottlers and a significant Mexican industrial player. The post appears fresh (October 19, 2026) but the record count and data types are not yet detailed. Defenders should validate exposure claims and watch for reuse of company or customer credentials.
Facturas del IMOVEQROO de Quintana Roo publicadas en foro
Instituto de Movilidad del Estado de Quintana Roo (IMOVEQROO)
A second thread advertises leaked invoices from IMOVEQROO, the Quintana Roo state mobility institute, reinforcing that a real government dataset is circulating. Invoice dumps expose personal, fiscal and contact data useful for fraud and social engineering against citizens. Confirms an active government exposure requiring incident review.
Filtración de facturas del Instituto de Movilidad de Quintana Roo
Instituto de Movilidad del Estado de Quintana Roo (IMOVEQROO)
Invoices (facturas) belonging to IMOVEQROO, a Quintana Roo state government mobility agency, were posted on DarkForums. Billing data typically exposes names, tax IDs (RFC), addresses and amounts, enabling identity fraud and targeted phishing against citizens and providers. As a government body, the claim warrants verification, notification and monitoring for reuse of the exposed records.
Filtración de datos de prisioneros del Gobierno de Irak
Gobierno de Irak (registros de prisioneros)
A dataset described as an Iraqi prisoner-related leak has surfaced on a hacking forum. Detention and prisoner records are highly sensitive government data whose exposure can endanger individuals and reveal institutional details. Relevant for government and human-rights risk monitoring, though the scale is unconfirmed.
Filtración de documento interno de SpaceX sobre la constelación Starshield
SpaceX (Starshield)
An internal SpaceX document describing the Starshield constellation's technical baseline and architecture has been posted for sale. Starshield is SpaceX's defense-focused satellite line, so exposure of architecture details could help adversaries studying US military space capabilities. Relevant for defense and space-sector threat monitoring.
Filtración de la base de datos de Norauto Francia
Norauto (Francia)
A database belonging to French automotive service chain Norauto has been posted on a hacking forum. Such leaks expose customer identities and contact data that enable phishing and account takeover. Retail and automotive-service defenders should watch for follow-on fraud and brand impersonation campaigns.
Filtración de base de datos de la Comisión Nacional de Salud de China
China National Health Commission (NHC)
A threat actor is offering a database allegedly belonging to China's National Health Commission, a central government health authority. Leaks from national health bodies can expose citizen records and internal accounts useful for follow-on intrusions. Government and health-sector defenders should watch for credential reuse and targeted phishing.
Filtración de 4,1 millones de datos de Chronopost (Francia)
Chronopost (Francia)
A dataset of more than 4.1 million records attributed to French parcel carrier Chronopost has been posted. Names, addresses and contact details at that scale enable convincing delivery-scam phishing and fraud against consumers and business partners. Defenders should prepare for credential-stuffing and brand-impersonation campaigns.
A la venta dataset de identidad nacional de India con 850M registros
India (dataset nacional de identidad, HITEK)
A 109GB dataset allegedly containing 850 million Indian nationwide identity records is being advertised on a hacking forum. At this scale it ranks among the largest identity exposures, enabling mass fraud, KYC bypass and highly targeted attacks. It is critical for fraud, identity-verification and financial-sector defenders to monitor.
Base de datos de escuelas de Argentina a la venta
A database described as an 'Argentina School Database' was posted to DarkForums today, indicating a possible fresh leak of Argentine educational records. Student and staff PII from the region is sensitive and enables targeted attacks, fraud and credential abuse. Argentine defenders should validate the claim and scope the exposure.
Base de datos completa de acclimited.com con 4,6M de registros
acclimited.com
A full database for acclimited.com is being offered on DarkForums, claiming 4,624,461 records posted minutes ago. If genuine, it exposes customer and organizational data that can fuel phishing, account takeover and fraud. The claim should be verified and affected users monitored for credential abuse.
Base de datos de La Reserva Club Sotogrande con 3,5M de clientes
La Reserva Club Sotogrande
A 2025 database of La Reserva Club Sotogrande, an exclusive Spanish golf and residential club, is offered for sale claiming over 3.5 million wealthy client records. This high-net-worth PII enables targeted phishing, fraud and extortion. Spanish-facing entities should treat affected individuals as high-value targets.
Base de datos de Morgan Stanley con 892M de registros a la venta
Morgan Stanley
A full database attributed to Morgan Stanley is being offered on DarkForums, claimed to hold over 892 million records of US consumer intelligence. If authentic, it exposes massive volumes of client PII and financial data tied to a major global bank. Defenders should verify the claim and monitor for downstream fraud, phishing and credential-stuffing abuse.
Base de datos con 148.288 ciudadanos noruegos expuestos
A database of 148,288 Norwegian citizens including phone numbers, names and vehicle licence plates is advertised on an onion forum. The combination enables identity fraud, vehicle-targeting crime and highly convincing SMS phishing, though it is a vehicle-registry-type leak outside Latin America. It matters mainly as a supply source for social-engineering campaigns, not as a regional alert.
Combolist de 6,86 M de URL:LOG:PASS atribuida a DAXUS.PRO
A stealer-log style dataset of roughly 6.86 million URL:login:password entries attributed to the DAXUS.PRO cloud is being shared on an underground forum. Volumes of this size drive credential stuffing and session hijacking against corporate SSO, VPN and webmail portals, so organisations should hunt for matching corporate domains. It is generic, unattributed to a specific victim, and undated, so it ranks well below named access sales or regional breaches.
Base de datos china de 6,4 GB con DNI y tarjetas (parte 3)
A 6.4 GB multi-part dataset containing Chinese national ID cards, credit card data and business information is being distributed on a major leak forum. The multinational card data creates downstream fraud and BIN-attack risk for issuers and acquirers worldwide, including Latin American banks processing cross-border transactions. Because it is part three of a series with no clear date, it is lower priority than fresh regional incidents.
Acceso y SQL de 962 MB de la Fundación ADINA (hospital y universidad)
ADINA Foundation
The actor claims full compromise of the ADINA Foundation, which operates university and hospital services, and is offering a 962 MB SQL dump containing national ID numbers (CNICs), domains and likely patient and student data. Compromised healthcare and education estates allow both data monetisation and follow-on ransomware deployment. Defenders in the region's healthcare sector should check for the same indicators of database exposure and weak perimeter controls.
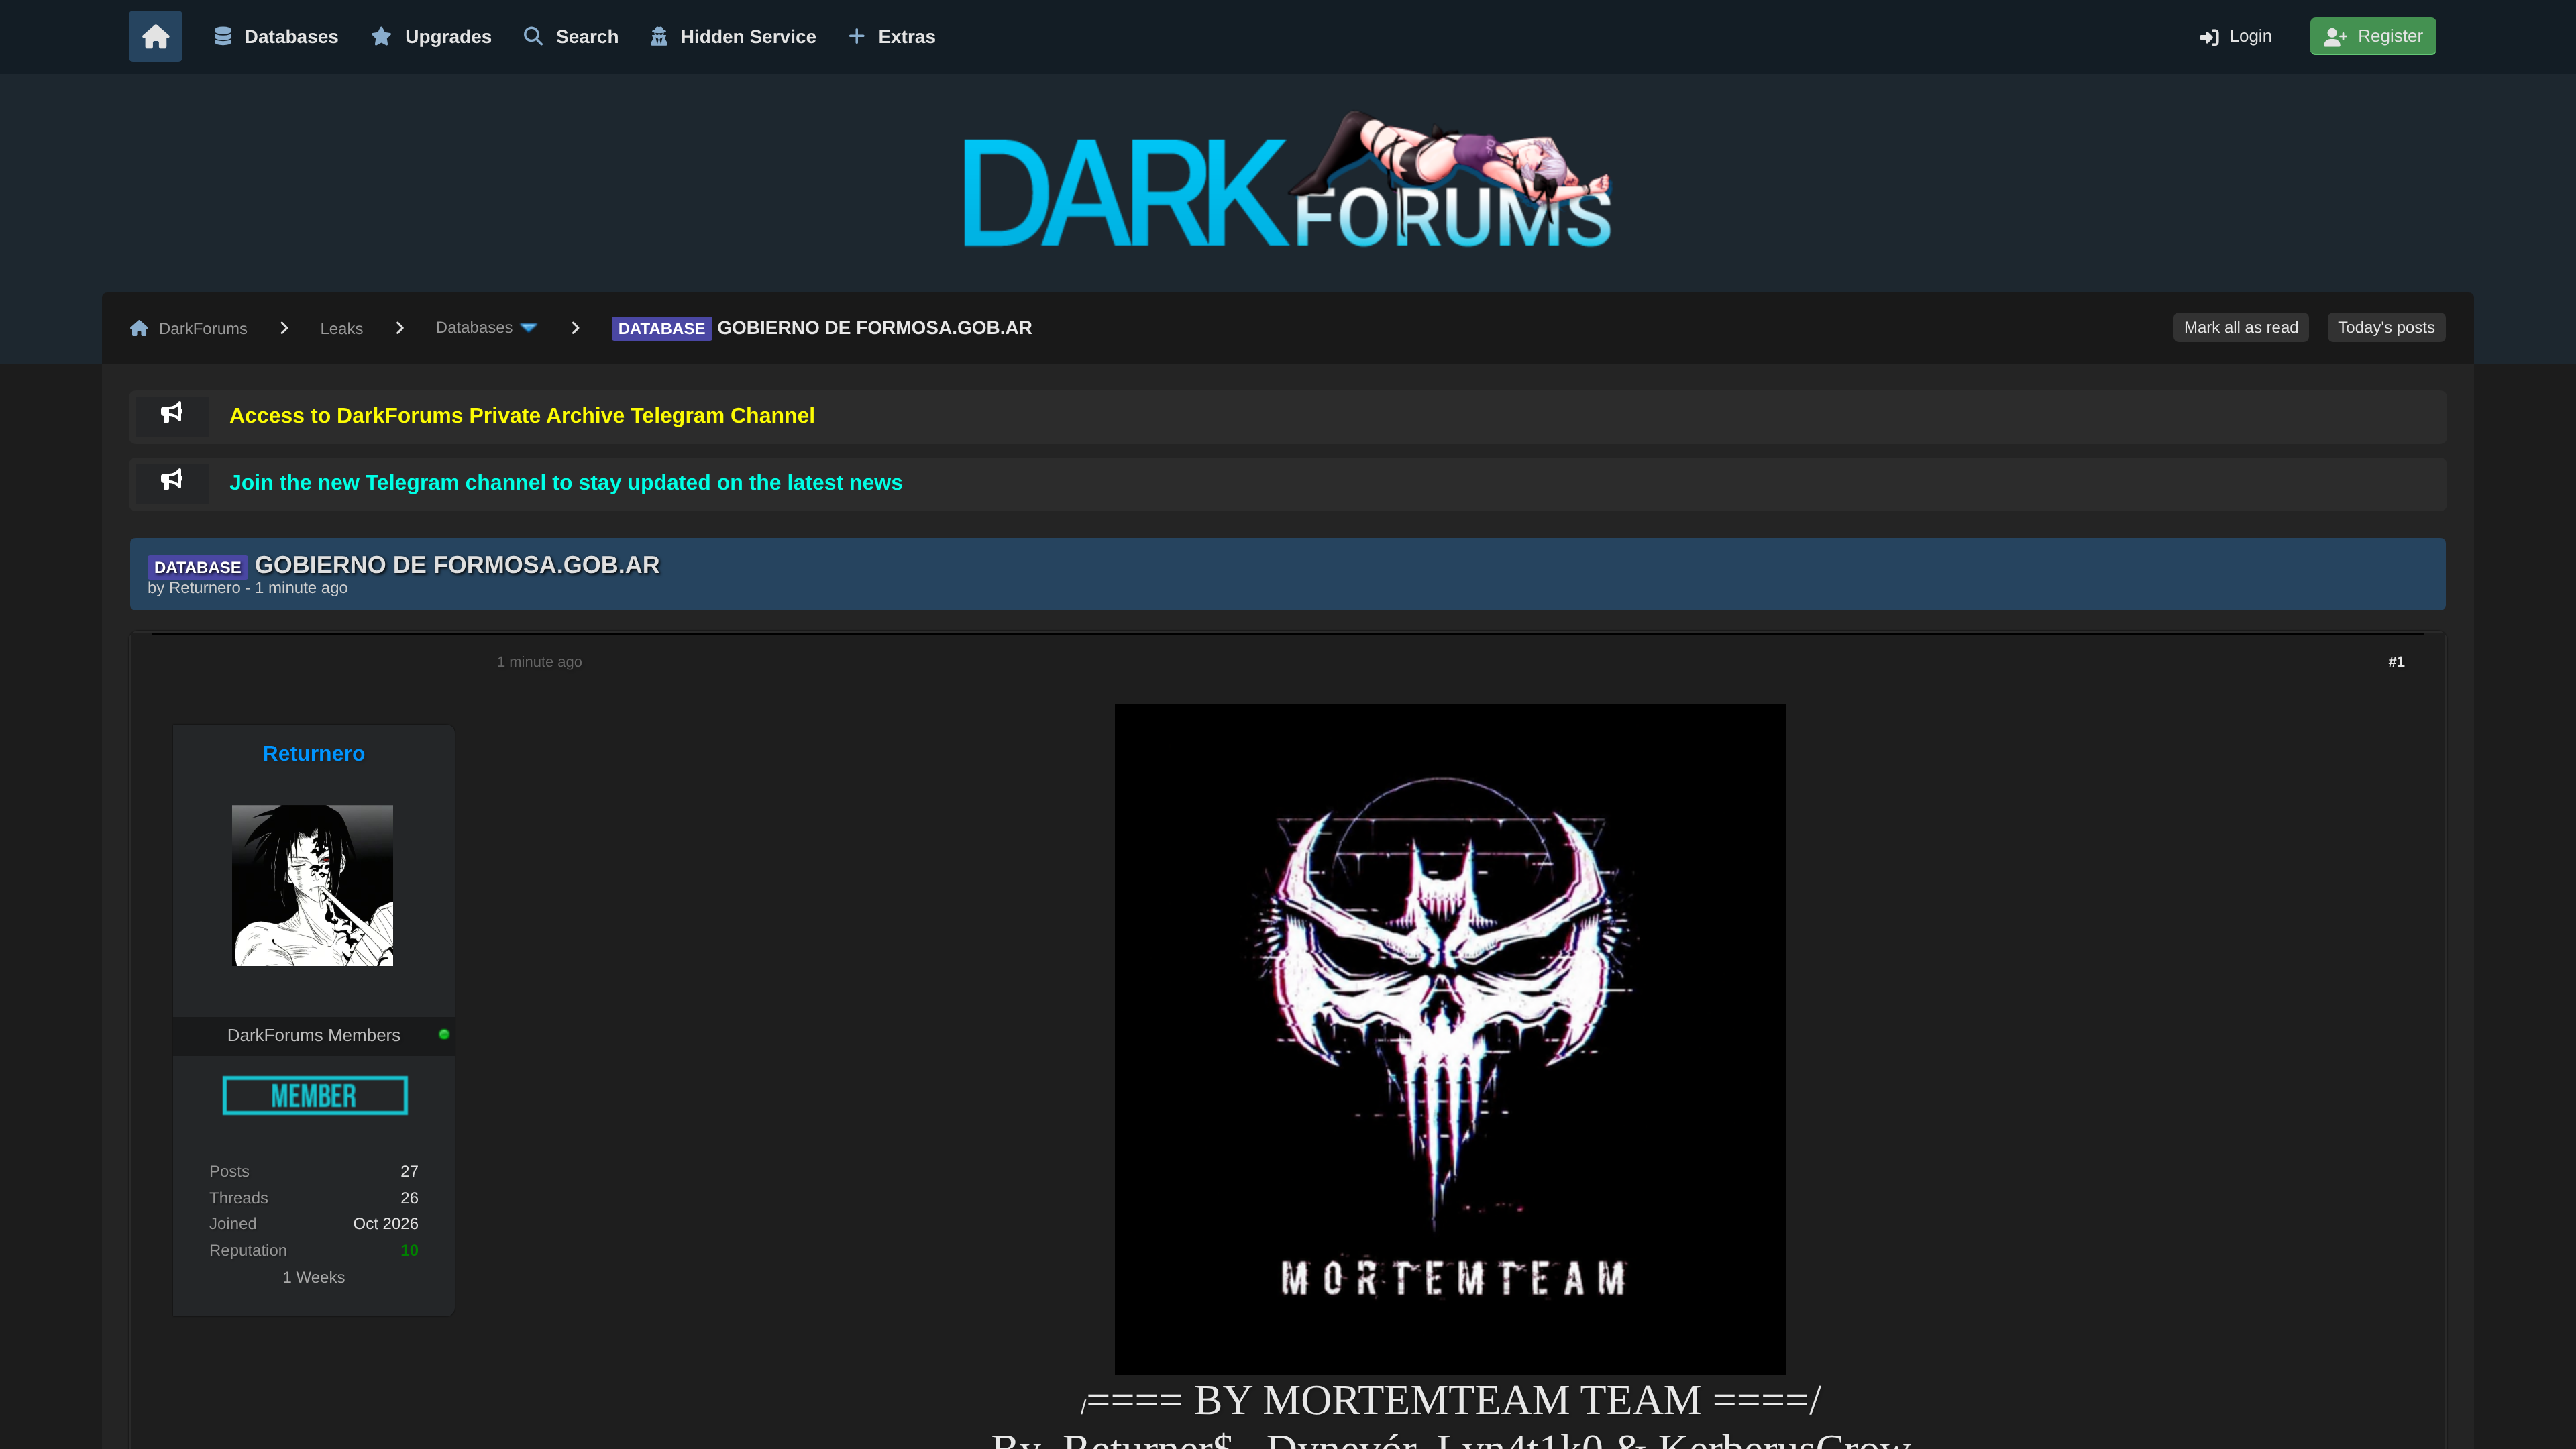
Base de datos del Gobierno de Formosa (gob.ar) filtrada
Gobierno de la Provincia de Formosa (gob.ar)
A threat actor published a database allegedly belonging to the Formosa provincial government domain (gob.ar), posted minutes ago. If the dump is genuine it exposes internal government data usable for phishing campaigns against provincial staff, credential stuffing on public services and further intrusion into provincial infrastructure. Argentine public-sector entities are high-value targets for both cybercriminals and state-nexus actors, so this should be validated against the real systems immediately.