Underground · what matters today
The underground stories that broke through this window. Gov/mil, access sales, ransomware, leaks, stealers. Screenshots and context on each.
Distribution by category · window
- Gov / Military54
- Access sale41
- Ransomware50
- Leak415
- Stealer0
- Other10
Window
Category
Severity
Base de datos de openrouter.ai con 252K usuarios y API keys
openrouter.ai
A dump of openrouter.ai is posted with roughly 251,996 users and 207,847 API keys. Exposed API keys allow abuse of paid AI services, quota theft and, where billing is linked, direct financial loss. Organizations using the platform should rotate keys immediately and audit usage.
Base de datos del Ministerio de Defensa de Israel a la venta
Israel Ministry of Defense
A thread advertises a database attributed to the Israel Ministry of Defense, though the content sits behind a login wall and is unverified. If authentic, this would be a nation-state-grade leak of sensitive personnel or systems data. Treat as unconfirmed but monitor, as defense-related leaks attract high demand.
Filtración de base de datos de Aflac Japón
Aflac Japan
A forum thread claims a database leak from Aflac Japan, the local arm of a major insurer. If genuine, it exposes customer and policy data under strict Japanese privacy rules. Insurers are high-value for fraud and downstream identity theft, so sample verification and notification are advised.
Filtrado el sistema de correo del Servicio Geológico Mexicano
Servicio Geológico Mexicano
A forum post advertises a leak from the official email system of the Servicio Geológico Mexicano, a federal technical-scientific body dependent on Mexico's economy ministry. Exposed mail infrastructure gives attackers a credible channel for internal phishing, password resets and lateral movement toward federal systems. Mail-system data should be treated as sensitive even when only addresses and credentials are exposed.
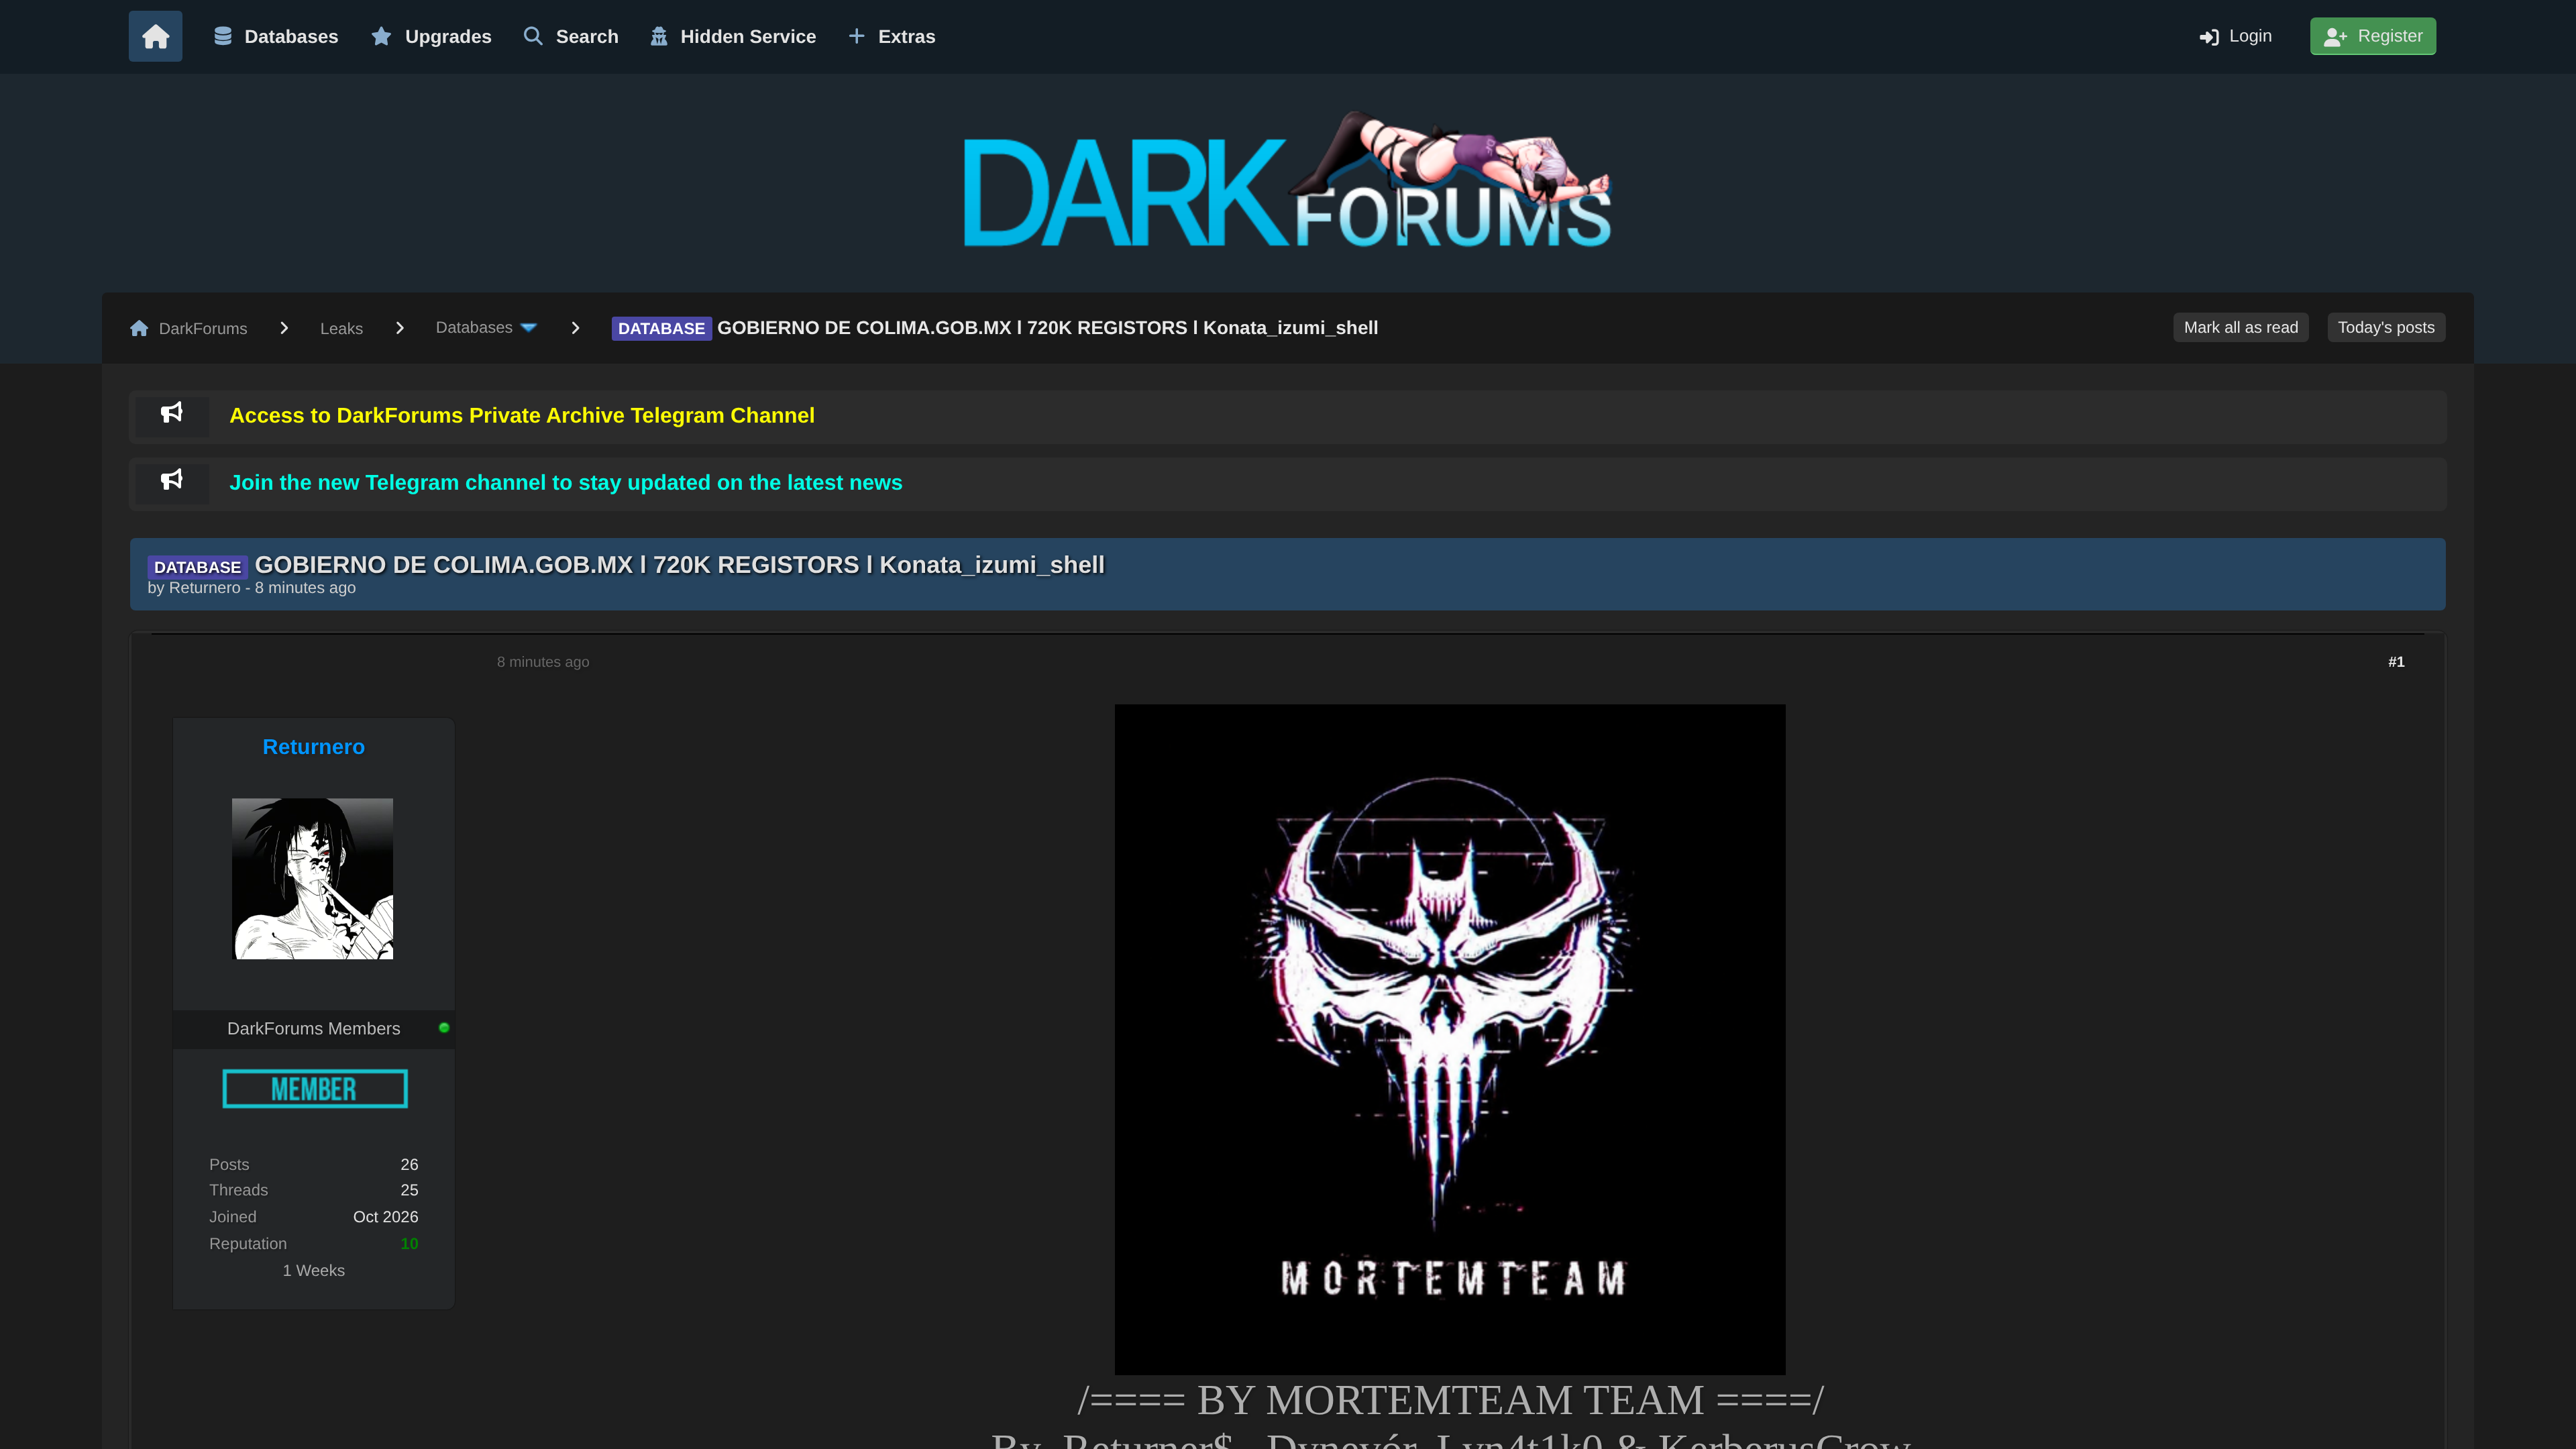
Base de datos del Gobierno de Colima con 720K registros filtrada
Gobierno del Estado de Colima (gob.mx)
An actor is publishing a database from the Colima state government portal (gob.mx) with roughly 720,000 records, allegedly obtained via a webshell. It affects a Mexican government entity and exposes citizen and procedure data, enabling fraud and targeted phishing. Requires notification, server access review and hunting for the referenced webshell.
Filtración de la base de datos completa del CONALEP Morelos (24.000+ registros)
CONALEP Morelos (México)
A full database of CONALEP Morelos, a Mexican public technical-education institution, was posted for download with more than 24,000 records. Exposed education-sector data usually includes student and staff PII, enrollment identifiers and institutional accounts, which enable targeted phishing and credential reuse against a .edu/.gob ecosystem. The post dates from August 2026, so it is not a fresh alert but still a confirmed public-sector leak in the region.
Base de datos de la operadora brasileña Claro con 46 millones de líneas
Claro Brasil (América Móvil)
BreachForums hosts a reposted dump claiming 46,033,380 lines of Claro Brazil customer data. Claro is a major telecom and critical-infrastructure operator, so subscriber, contact and contract records expose millions of Brazilian users and enable phishing, SIM-swap and account-takeover campaigns. The 'REPOST' tag signals a resurfacd batch, so freshness should be validated before treating it as a new incident.
Filtración de datos del Gobierno Autónomo de Santa Cruz (INOCUIDAD), Bolivia
Gobierno Autónomo Departamental de Santa Cruz – INOCUIDAD (Bolivia)
A public-sector Bolivian departmental government entity, INOCUIDAD (food-safety authority of Santa Cruz), has a database published for free on a leak forum. The post does not state record volume, but gov records typically include staff accounts, internal contacts and inspection data usable for phishing and credential stuffing against .gob infrastructure. Even if the dump is partial, it gives attackers a verified internal naming and email map of a regional government body.
Datos de 4.000 efectivos militares de la India publicados
Indian Armed Forces personnel
A poster claims to hold 2026 data on roughly 4,000 Indian military personnel, offered on DarkForums. Personal records of service members support identity fraud, targeting and social engineering against defence staff. The volume is small and unverified, so this is context rather than an actionable regional alert.
Base de datos del gobierno local de Binh Duong (Vietnam) a la venta
Binh Duong provincial government (mail.tinhuybinhduong.vn)
A DarkForums listing offers a database plus certifications tied to the Vietnamese provincial government domain mail.tinhuybinhduong.vn. Government mail accounts and certificate material enable impersonation, credential reuse and deeper intrusion into provincial systems. Impact is limited to one locality, but the asset type (mail + certs) is directly exploitable.
Filtración de datos de reclutamiento de la Real Fuerza Aérea de Malasia
Royal Malaysian Air Force
A thread offers '264 access' records apparently taken from the Royal Malaysian Air Force career and recruitment portal. Recruitment databases hold applicant identities, national ID numbers and contact details that are ideal for spear-phishing military candidates. The small volume and lack of a visible date lower urgency, but the military context keeps it relevant.
Venta de acceso al sistema de nóminas de las Fuerzas Armadas de Malasia
Malaysian Armed Forces
A seller advertises access (233 entries) to the Malaysian Armed Forces payroll system, a military HR and finance platform. Payroll access exposes service members' identities, bank account details and salary data, enabling fraud and intelligence collection against military staff. Although outside Latin America, a named armed-forces payroll compromise warrants tracking and cross-referencing.
Filtración del archivo del proyecto Hull 230 del USACE
US Army Corps of Engineers (USACE)
A user has just posted the 'USACE Hull 230 MCHD Project Archive', engineering documentation belonging to the US Army Corps of Engineers. Project archives typically contain drawings, site plans, schedules and contract data useful for intrusion or physical targeting. Confirming what was exposed is necessary to assess risk to a military-linked infrastructure program.
Filtración antigua (datos de 2020) de la aseguradora mexicana Ahorro Seguros
ahorroseguros.mx
A DarkForums post revives a dump attributed to the Mexican insurance site ahorroseguros.mx, but the data itself is labelled Q1 2020, so it is a re-release rather than a new breach. It likely contains client, policy and contact records useful for insurance-related fraud and phishing in Mexico, but the victims have had years to rotate and the value today is limited. Treat it as background context for Mexican financial-sector exposures, not as a fresh alert requiring incident response.
Filtración de datos del Ministerio Coordinador de Economía de Indonesia
Kementerian Koordinator Bidang Perekonomian (Indonesia)
A recently posted thread claims to leak data from Indonesia's Coordinating Ministry for Economic Affairs, a central government body. Ministry datasets usually contain staff directories, internal contacts and policy documents that support phishing and influence operations. Government leaks of this type are frequently reused for follow-on targeting of regional institutions.
Filtración de datos de Crunchbase publicada en foro criminal
Crunchbase
A PwsForums thread posted today offers a Crunchbase leak; the platform aggregates corporate contacts, funding, employee and executive data for hundreds of thousands of companies. Even a partial dump is a high-quality targeting list for BEC, investor-fraud and executive spear-phishing, and it can be cross-referenced with stealer logs to find corporate logins. Organisations whose staff emails appear in the set should expect targeted phishing and should monitor for credential stuffing against SaaS and investor-relations portals.
Base de datos completa y SQLi de Conexus Mobile a la venta
Conexus Mobile (conexusmobile.com)
The seller N0VEMBER is advertising a full database dump for conexusmobile.com together with a working SQL injection vulnerability, posted minutes ago. A live SQLi on a telecom/mobile-services provider means the breach is ongoing and can be re-exploited for subscriber data, SIM-related account actions and customer PII. Defenders of that platform, and peers in the MVNO/telecom space, should treat the SQLi as active, hunt for injection traffic in WAF and DB logs and patch before the dump is weaponised further.
Filtración de datos de la Caja de Salud de la Banca Privada (Bolivia)
Caja de Salud de la Banca Privada (CSBP), Bolivia
A fresh DarkForums thread (seconds old) offers a database attributed to CSBP, a Bolivian private-banking health insurer, and the same dump is being mirrored on other forums. Health insurers hold member identities, medical records and payment data, making this a critical-infrastructure level exposure for the region. Defenders should verify scope and warn the entity before the data is monetized.
Acceso al correo institucional de una autoridad agrícola de Paraguay
Autoridad agrícola del Estado paraguayo (MAG/SENAVE)
A thread on DarkForums advertises the official email system of a Paraguayan government agricultural authority, implying access to institutional mailboxes or the accounts that control them. Compromise of a ministry-level mail tenant enables business email compromise against suppliers and other state bodies, credential reuse into connected government services, and exfiltration of internal documents. Defenders in the Paraguayan public sector should verify MFA coverage, impossible-travel and mail-forwarding rules on this domain immediately.
Base de datos de RENIEC Perú con 31M de ciudadanos reeditada
RENIEC (Perú)
A forum post re-shares a 31 million-record database attributed to Peru's national identity registry RENIEC, tagged 2023. Despite the scale and sensitivity of national ID data, the dataset is clearly old and has circulated before, so it is not a fresh breach alert. It remains relevant background for identity-fraud and impersonation risk against Peruvian citizens.
Base de datos del Consejo de la Judicatura de Ecuador publicada
Consejo de la Judicatura de Ecuador
A threat actor posted a database attributed to Ecuador's Consejo de la Judicatura, the body that administers the country's judiciary, on a dark web forum within the last minutes. If authentic, it could expose judicial personnel and case-related records, enabling targeted phishing and social engineering against the justice system. Defenders in Ecuador's public sector should treat this as a fresh government data exposure and verify scope.
Filtración de datos del gobierno de China
China government (unspecified)
A DarkForums thread posted about six hours ago advertises a leak attributed to a Chinese government body. Government data leaks of this kind can contain internal records, credentials and citizen PII, valuable for espionage and fraud supply chains. It is off-region for AR-LATAM defenders and unverified, so lower priority but worth tracking for dataset indicators.
Filtración de datos de cointracker.io
cointracker.io
A DarkForums poster claims a leak of the cryptocurrency portfolio-tracking service cointracker.io, published roughly eight hours ago. Such a leak could expose user emails, wallet-linked holdings and account data, raising phishing, account-takeover and targeted-theft risk for crypto holders. Fresh and tied to a named real service, so worth validating the dataset sample and size.
Venta de bases de datos brasileñas en BreachForums
Brazil (unspecified organizations)
A seller in BreachForums' marketplace is advertising an 'updated' set of databases sourced from Brazil, a LATAM jurisdiction of direct interest. If genuine, this represents bulk exfiltrated records of Brazilian organizations being monetized, enabling fraud, credential stuffing and downstream intrusion. The post is undated and vague on volume and victims, so scope needs confirmation before treating as fresh.