Underground · what matters today
The underground stories that broke through this window. Gov/mil, access sales, ransomware, leaks, stealers. Screenshots and context on each.
Distribution by category · window
- Gov / Military55
- Access sale43
- Ransomware47
- Leak419
- Stealer0
- Other10
Window
Category
Severity
Venta de 30 millones de registros del banco nigeriano Zenith Bank
Zenith Bank
A forum actor advertises 30 million records allegedly belonging to Zenith Bank, one of Nigeria's largest financial institutions, likely containing customer identities, account data and contact details. A dataset of that scale in the financial sector fuels account takeover, business email compromise and cross-border mule operations. The post carries no date, so authenticity and freshness need verification before treating it as a confirmed breach.
Venta de 366 GB de datos de la aseguradora Rand Mutual (Sudáfrica)
Rand Mutual Assurance
A seller is offering 366 GB of data attributed to Rand Mutual Assurance, a South African workers' compensation insurer, which would include medical, claim and identity records of policyholders and claimants. The volume suggests a full-scale database theft rather than a small scrape, making it valuable for identity fraud, insurance fraud and extortion. It is outside the AR/LATAM region but represents a genuinely large corporate leak worth tracking.
Filtración de datos KYC de la fintech Revolut
Revolut
A BreachForums post advertises a 'fresh 2026' leak of Revolut KYC data — the identity-verification records a bank holds on customers, such as IDs, selfies and addresses. KYC leaks of this kind directly fuel account takeover, synthetic identity and targeted fraud. Financial-sector defenders should watch for credential and identity abuse tied to the exposed records.
Filtración de 200.000 clientes de Getir y BiTaksi
Getir / BiTaksi
A forum actor is distributing a new dump of roughly 200,000 Getir and BiTaksi customers, posted on 19 October 2026. The records cover users of Turkey's largest delivery and ride-hailing apps, exposing contact and account data useful for credential stuffing and SMS phishing. It matters to defenders outside the region only as a source of reused-credential exposure and fraud infrastructure.
Presunta filtración KYC de Revolut de 2026 a la venta
Revolut
A forum user claims to hold a fresh 2026 Revolut KYC dataset, posted today and still unverified. If genuine, KYC material (ID documents, selfies, addresses) is far more damaging than ordinary account data because it fuels full identity takeover and passes liveness checks. Treat as unconfirmed but monitor for correlated Revolut phishing and account-takeover activity.
Filtración de datos de 345.209 clientes del Banco Santa Fe
Banco Santa Fe (Argentina)
A 345,209-record Banco Santa Fe customer database is circulating with names, CUIT, DNI, email, phone and VIP-status flags. As the province's state-owned bank, the exposure enables identity fraud, account-takeover attempts and targeted phishing against provincial taxpayers and public employees. DNI+CUIT pairs are prime pretext material for social engineering against both the bank and the provincial government.
Base de datos de 128K de kiassure.com a la venta
kiassure.com
A seller lists a 128K-record database attributed to kiassure.com, a relatively small dataset compared with major breaches. Even a mid-size dump of emails, hashes or PII enables credential stuffing and targeted phishing campaigns. The company's profile and the data's authenticity are unconfirmed, keeping overall impact limited.
Filtración de datos de la operadora francesa SFR
SFR
A thread titled 'SFR.FR' offers what it describes as a leaked dataset from SFR, one of France's main telecom operators. Telecom subscriber data can fuel SIM-swap, phishing and account-takeover attacks, and telecoms are designated critical infrastructure. The snippet is truncated and gives no record count, so scope and veracity remain unverified.
Base de datos de Carrefour ofrecida en filtración
Carrefour
A thread titled 'DATABASE CARREFOUR DATABASE' offers what is claimed to be a Carrefour database dump. Carrefour is a major retailer with significant operations in Argentina, Brazil, Spain and across Latin America, so any genuine leak of customer or employee records carries regulatory and fraud risk in the region. The post is behind a login wall with no sample or record count, so authenticity is unconfirmed and needs verification.
Venta de acceso completo a servidor vía webshell WSO (Tpadmin)
Tpadmin
A seller is advertising full server access obtained through a WSO webshell, a common upload/persistence mechanism after a web compromise. Full server-level access lets a buyer deploy ransomware, harvest credentials, or pivot into internal networks, so it appeals to access brokers and ransomware affiliates. The victim identity and scope are not disclosed and the thread is behind a login wall, so authenticity is unverified.
Filtración de documentos confidenciales internos de Ferrari
Ferrari
Internal confidential documents and datasheets belonging to Ferrari are being shared for download on DarkForums. Leaked engineering and commercial material can aid corporate espionage, supplier targeting and tailored phishing. The high-profile brand raises lure risk for employees and partners.
Base de datos de 3,9 M de ciudadanos israelíes a la venta
A 3.9 million-record dataset of Israeli citizens' personal data is being offered on DarkForums. The scale indicates a large PII leak likely enabling identity theft, phishing and account takeover. Relevant to fraud and KYC teams even though the source organization is unidentified.
Filtración de base de datos del National Bank of Pakistan
National Bank of Pakistan
A forum user claims to have leaked a database belonging to the National Bank of Pakistan, a state-owned financial institution. If authentic, exposed customer and account data would enable fraud, phishing and business email compromise against banking customers. The post provides no record count or sample, so the leak needs corroboration before being treated as a confirmed breach.
Base de datos y CRM del sistema de pagos PaySysLabs a la venta
PaySysLabs
A CRM and database belonging to PaySysLabs, described as Pakistan's instant payment system, is being advertised for sale. Compromise of a payment platform exposes merchant and transaction records and enables downstream fraud. Financial-sector defenders should treat this as a priority lead for abuse monitoring.
Ransomware Qilin publica a la víctima mexicana SEPIVER
SEPIVER
The Qilin ransomware group has listed SEPIVER, a victim located in Mexico, on its leak site. Fresh publication signals an active breach with data-extortion risk for a Latin American entity. Regional defenders should investigate and warn any connected suppliers or clients.
Base de datos de clientes del bróker Avatrade (España) a la venta
Avatrade (España)
A seller listed a Spain-focused Avatrade customer database on 19 October 2026 on a leak forum. Trading-platform customer data usually includes identity documents, contact details and account information valuable for financial fraud and account takeover. The brokerage and Spanish financial authorities should confirm scope, notify affected clients and watch for credential-stuffing against client portals.
Doxeo del director del IMSS, Zoé Robledo Aburto
Zoé Robledo Aburto (IMSS, México)
A fresh dox thread targets Zoé Robledo Aburto, director of Mexico's IMSS, published within minutes of collection. Such releases typically bundle personal identifiers, contact data and sometimes credentials, which fuel social engineering and phishing against a senior health-sector official and his institution. Mexican public-health entities should brief the official's team and monitor for credential exposure.
Base de datos del Gobierno de Colombia ofrecida en venta
Gobierno de Colombia
A threat actor posted on 19 October 2026 a claimed Colombian government database on a major leak forum. The agency and record count are not yet confirmed, but any dump of citizen or official data from a national government enables phishing, impersonation of public entities and credential reuse against .gov infrastructure. Colombian public entities should verify exposure, rotate privileged credentials and monitor for follow-on access sales.
LockBit5 publica a la minorista turca Istanbul Foodstuff Trading
Istanbul Foodstuff Trading Co LLC
LockBit5 added Istanbul Foodstuff Trading Co LLC, a Turkish retail/computer-peripherals firm, to its leak site, indicating an active ransomware intrusion with likely data theft. The victim is outside the AR-LATAM region, so direct impact is limited, but it shows LockBit5's continued targeting of small and mid-size commerce. Worth noting for tracking the group's activity and TTPs.
Filtración de la base de datos de la Policía de Chihuahua (EEPOL)
Policía de Chihuahua (EEPOL), México
A forum user published the EEPOL database tied to Chihuahua State Police in Mexico, posted minutes ago, implying a live, fresh release. Law-enforcement personnel records expose officers' identities and contact data, enabling doxxing, targeted phishing and physical threats. Any government agency in the region should treat this as a high-priority incident and monitor for correlated leaks.
Venta de exploit RCE de Chromium para Windows 10/11 (cadena completa)
A seller is offering a full Chromium renderer RCE chain affecting Windows 10/11 browsers, posted 21 Oct 2026. Weaponized browser exploits enable drive-by initial access, compromising endpoints without user interaction and bypassing many perimeter controls. Fresh, possibly unpatched browser RCE capabilities are prime enablers of intrusion and ransomware campaigns.
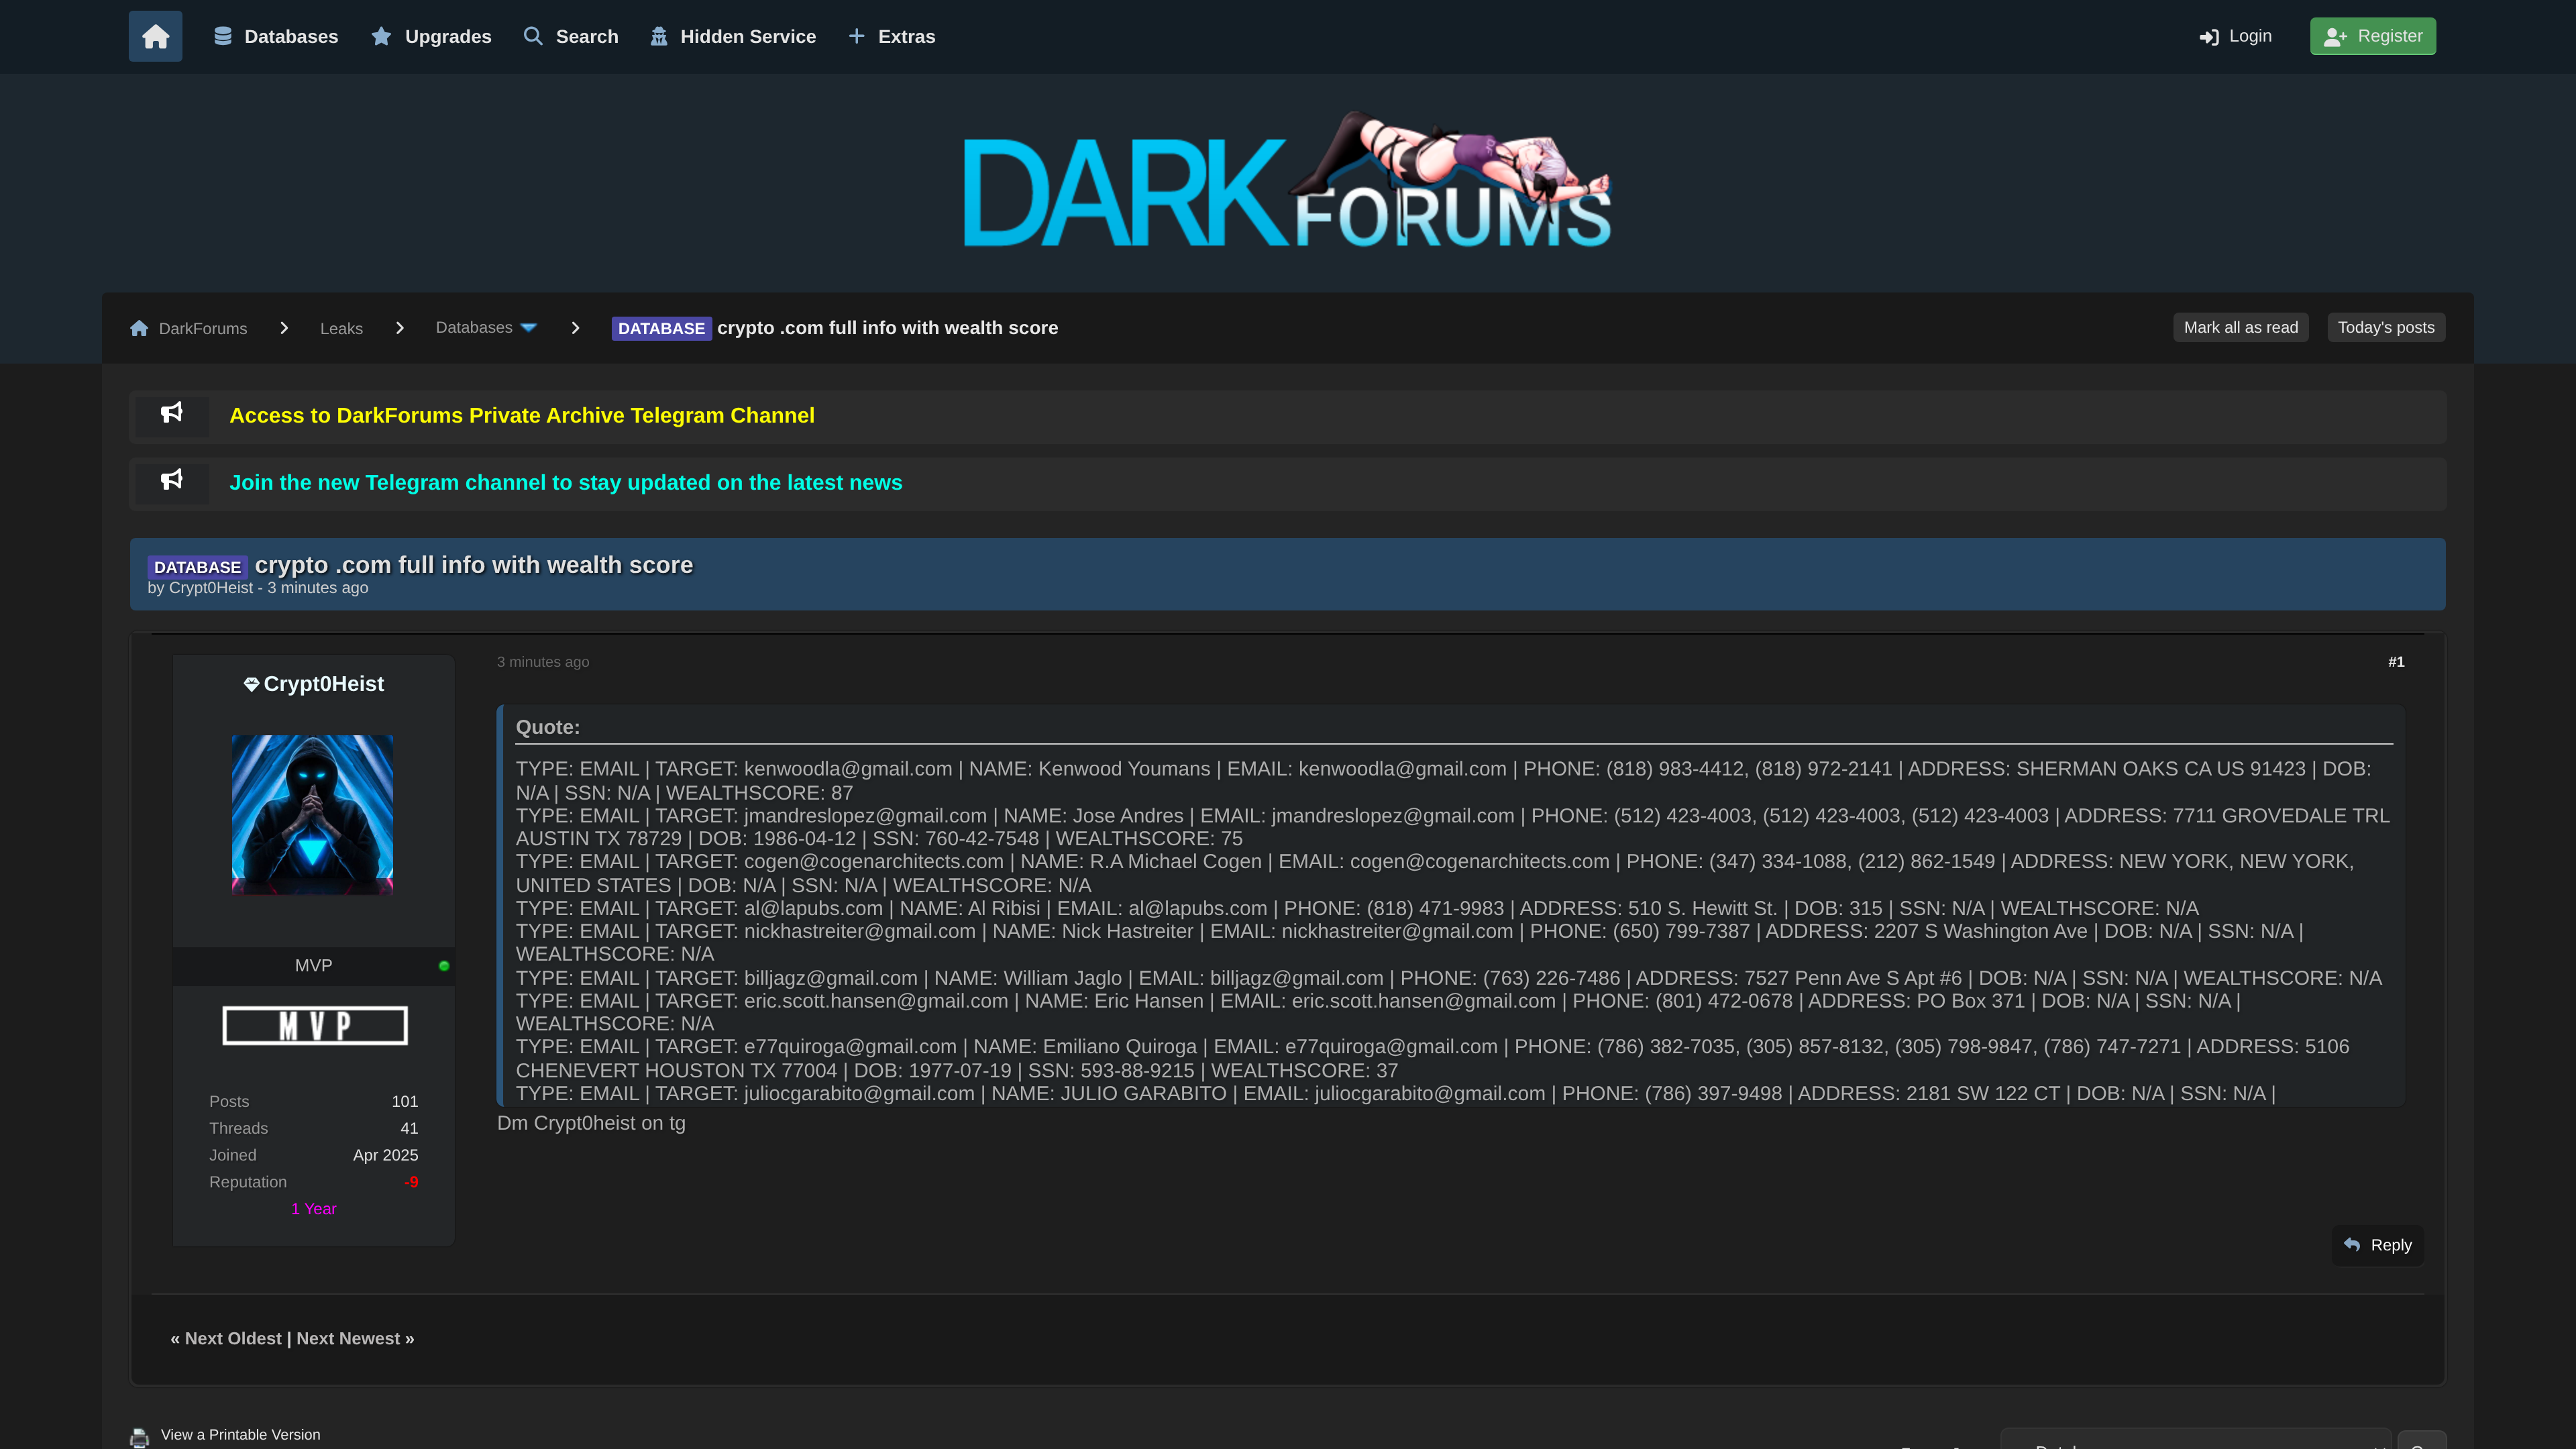
Base de datos de usuarios de Crypto.com con info completa a la venta
Crypto.com
A seller posted a Crypto.com user database containing full personal details plus a 'wealth score', freshly published on 22 Oct 2026. This lets attackers rank and prioritize high-net-worth exchange account holders for phishing, SIM-swap and account-takeover attempts against crypto funds. Exchange customer data is high-value because it enables direct financial theft and targeted social engineering.
Base de datos del sistema sanitario de farmacias de Turquía filtrada
Sistema sanitario de farmacias de Turquía
A repost claims to leak a database from Türkiye's pharmacy/health system, exposing sensitive patient and prescription-related data. Health records are high-value for fraud, identity theft and social engineering, and the data likely persists across mirror reposts. The 'repost' framing suggests it is not fresh, so it is worth monitoring rather than alerting urgently.
Filtración de 700.000 registros de CUPS del sector energético español
Sector energético español (CUPS)
A 700K-record database of Spanish CUPS electricity supply-point codes paired with mobile phone numbers has been posted for download. CUPS codes uniquely identify energy contracts and premises, so combining them with phones enables targeted phishing, fraud and account takeover against utility customers. Defenders in the Spanish energy sector should treat this as a confirmed exposure and warn affected customers.