Underground · what matters today
The underground stories that broke through this window. Gov/mil, access sales, ransomware, leaks, stealers. Screenshots and context on each.
Distribution by category · window
- Gov / Military54
- Access sale43
- Ransomware49
- Leak421
- Stealer0
- Other10
Window
Category
Severity
Base de datos del Gobierno de Colombia ofrecida en venta
Gobierno de Colombia
A threat actor posted on 19 October 2026 a claimed Colombian government database on a major leak forum. The agency and record count are not yet confirmed, but any dump of citizen or official data from a national government enables phishing, impersonation of public entities and credential reuse against .gov infrastructure. Colombian public entities should verify exposure, rotate privileged credentials and monitor for follow-on access sales.
LockBit5 publica a la minorista turca Istanbul Foodstuff Trading
Istanbul Foodstuff Trading Co LLC
LockBit5 added Istanbul Foodstuff Trading Co LLC, a Turkish retail/computer-peripherals firm, to its leak site, indicating an active ransomware intrusion with likely data theft. The victim is outside the AR-LATAM region, so direct impact is limited, but it shows LockBit5's continued targeting of small and mid-size commerce. Worth noting for tracking the group's activity and TTPs.
Filtración de la base de datos de la Policía de Chihuahua (EEPOL)
Policía de Chihuahua (EEPOL), México
A forum user published the EEPOL database tied to Chihuahua State Police in Mexico, posted minutes ago, implying a live, fresh release. Law-enforcement personnel records expose officers' identities and contact data, enabling doxxing, targeted phishing and physical threats. Any government agency in the region should treat this as a high-priority incident and monitor for correlated leaks.
Venta de exploit RCE de Chromium para Windows 10/11 (cadena completa)
A seller is offering a full Chromium renderer RCE chain affecting Windows 10/11 browsers, posted 21 Oct 2026. Weaponized browser exploits enable drive-by initial access, compromising endpoints without user interaction and bypassing many perimeter controls. Fresh, possibly unpatched browser RCE capabilities are prime enablers of intrusion and ransomware campaigns.
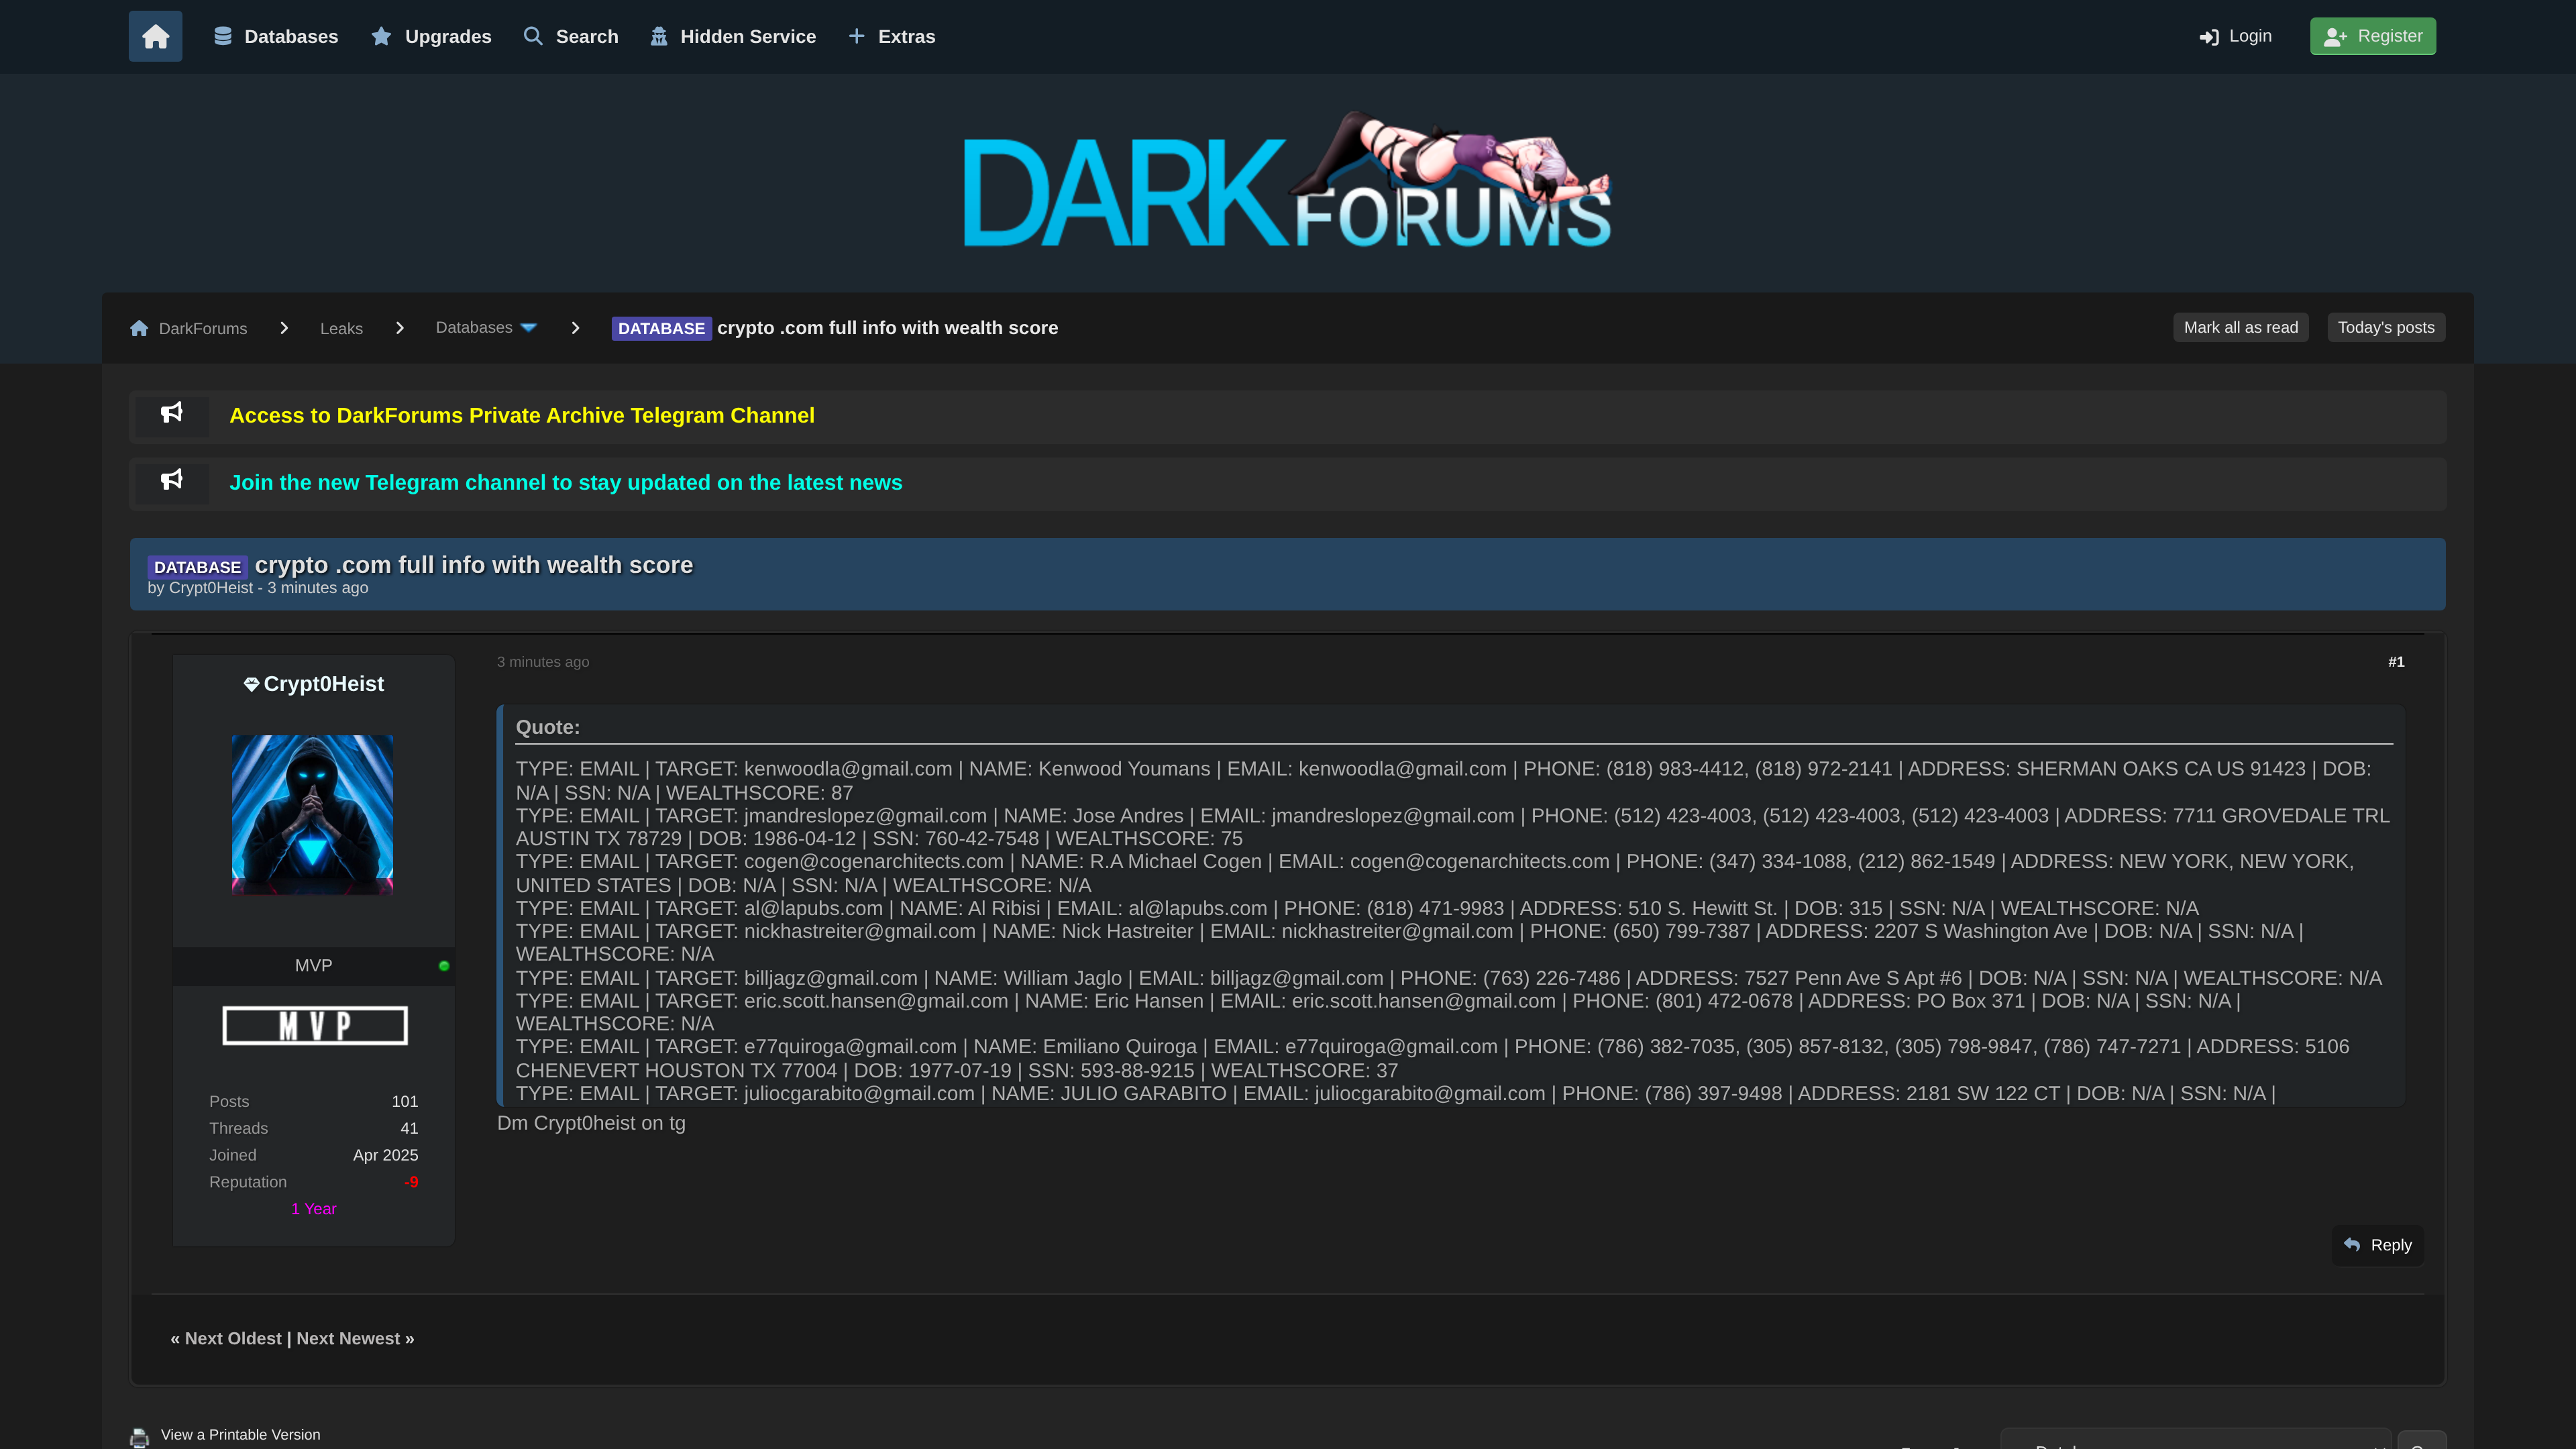
Base de datos de usuarios de Crypto.com con info completa a la venta
Crypto.com
A seller posted a Crypto.com user database containing full personal details plus a 'wealth score', freshly published on 22 Oct 2026. This lets attackers rank and prioritize high-net-worth exchange account holders for phishing, SIM-swap and account-takeover attempts against crypto funds. Exchange customer data is high-value because it enables direct financial theft and targeted social engineering.
Base de datos del sistema sanitario de farmacias de Turquía filtrada
Sistema sanitario de farmacias de Turquía
A repost claims to leak a database from Türkiye's pharmacy/health system, exposing sensitive patient and prescription-related data. Health records are high-value for fraud, identity theft and social engineering, and the data likely persists across mirror reposts. The 'repost' framing suggests it is not fresh, so it is worth monitoring rather than alerting urgently.
Filtración de 700.000 registros de CUPS del sector energético español
Sector energético español (CUPS)
A 700K-record database of Spanish CUPS electricity supply-point codes paired with mobile phone numbers has been posted for download. CUPS codes uniquely identify energy contracts and premises, so combining them with phones enables targeted phishing, fraud and account takeover against utility customers. Defenders in the Spanish energy sector should treat this as a confirmed exposure and warn affected customers.
Filtración de archivos del Gobierno de Coahuila, México
Gobierno de Coahuila (México)
A repost of a file/document leak attributed to the Government of Coahuila, Mexico, first surfaced around late 2022. It exposes internal public-sector documents relevant to defenders tracking Mexican government exposure. However, the material is years old, so treat it as historical context rather than a fresh incident.
Volcado de 4,4 millones de registros URL:LOG:PASS a la venta
A 4.4 million line corpus of URL:login:password entries, described as private and UHQ, is being distributed on NulledBB; this format matches infostealer log output rather than a single-vendor breach. Because entries are keyed to specific login URLs, they can be replayed directly against corporate VPN, webmail and SaaS portals. There is no named victim or date, so treat it as background credential-stuffing risk rather than an incident.
Filtración de datos de la turca Tera Group por hacktivistas
Tera Group
A leak-section post published roughly 35 minutes ago claims that data from Tera Group, a Turkish industrial/energy conglomerate, was stolen and released by the 'MLKP Revolutionary Justice Hackers' collective. The thread cites press coverage and is presented as a full data dump, which in hacktivist cases often includes internal documents, email archives and employee information. Even though the victim is outside Latin America, ideologically motivated leaks of critical-infrastructure-adjacent firms frequently seed follow-on intrusion and credential abuse.
Filtración de la base de datos de Westrock Coffee
Westrock Coffee
A forum user published a downloadable database allegedly belonging to Westrock Coffee, a US coffee trading and manufacturing company, under a 2026 tag. The posting is brand new (uploaded minutes ago), so contents and record count are still unverified, but corporate datasets of this type typically carry employee accounts, business contacts and internal operational data. Defenders at food-and-beverage or commodity supply-chain firms should treat it as a potential credential and partner-data exposure and monitor for reuse.
Ransomware bravox publica al bufete estadounidense Barrow & Grimm
Barrow & Grimm
The bravox ransomware group listed Barrow & Grimm, a US litigation law firm, as a victim on its leak site. Law firms hold sensitive client and case data that is attractive for double extortion and downstream attacks. Monitor for related credential and data exposure affecting its clients.
Ransomware bravox publica a la francesa AMSAM (salud)
AMSAM
The bravox ransomware group listed AMSAM, a French healthcare and social-services provider, as a victim on its leak site. Healthcare ransomware threatens patient data and service continuity, making it high-impact for the sector. It is outside Latin America but signals continued targeting of the health and social-care sector.
Hacktivistas filtran datos de la empresa turca Tera Group
Tera Group
The MLKP 'Revolutionary Justice Hackers' announced and leaked data from Turkish company Tera Group. Hacktivist dumps of this kind often include internal documents, employee records and credentials. It is a relevant example of politically motivated data leaks, though outside the Latin American region.
Base de datos del sitio japonés Famm (fotos familiares) a la venta
Famm
A database belonging to Famm, a Japanese family-photo sharing website, is being offered by a forum actor. Such leaks typically expose account details, emails and uploaded media, enabling credential stuffing and privacy harm. Consumer-facing services should check for exposure and force resets.
Filtración de 2,1 GB de datos de la aseguradora Majan Insurance
majaninsure.com
A forum actor posted a 2.1 GB archive allegedly containing leaked data from majaninsure.com, an insurance firm. If authentic it could expose customer PII, policy records and internal documents. Financial and insurance defenders should verify the dump and watch for downstream fraud and credential reuse.
Ransomware Silent Ransom Group publica al bufete Kirkland & Ellis
Kirkland & Ellis LLP
The Silent Ransom Group listed Kirkland & Ellis, one of the world's largest law firms, as a ransomware victim on its leak site. A compromise at this scale threatens highly sensitive M&A, litigation and client data spanning many organizations. It is a high-priority victim even though it sits outside Latin America.
Akira publica a la editorial Bethany Press
Bethany Press International
Akira claims Bethany Press International, a Christian book publisher and distribution services firm, and says it will upload 40GB of corporate data. The claimed material includes employee financial and personal records, customer information, financials and contracts. It is a mid-size US victim, so it ranks below regional incidents but illustrates the ongoing exfiltration pattern.
Akira publica a la alemana Medienwerkstatt
medienwerkstatt ag
Akira added medienwerkstatt ag, a Thurgau-based media and communications provider in the education sector, threatening to release 130GB of corporate data including employee personal information. The volume of exfiltrated HR and client material makes follow-on phishing and business email compromise likely. It is a European victim, so relevance for LATAM defenders is contextual rather than direct.
Akira publica al laboratorio de patología Annapath
Annapath, Inc.
Akira claims Annapath, a surgical and cytopathology laboratory serving Maryland, Delaware, Pennsylvania, DC, Virginia and West Virginia, and threatens to publish 110GB of corporate data. Healthcare diagnostics providers hold sensitive patient and partner data, so the leak would expose clinical relationships and business records. Although outside Latin America, the playbook (VPN/credential abuse against mid-size providers) mirrors regional targets.
Base de datos de Budigadai.com a la venta por 5.000 USD
BUDIGADAI.COM
A seller is offering a 1.7 GiB SQL dump of Budigadai.com for 5,000 USD, a modest-sized database of unclear business importance. No sample or record count is provided, so impact is hard to assess. Worth noting only for credential-reuse and brand-abuse tracking.
Base de datos del vietnamita Moon.vn a la venta
Moon.vn
A fresh post offers a database belonging to Moon.vn, a Vietnamese online education platform. Account, email and possibly enrolment data of students would be at risk if the dump is genuine. It is regionally relevant only to APAC defenders but signals continued targeting of education portals.
Publicado exploit masivo php2shell (CVE-2026-109618/109619)
A forum user posted a PoC tool ('php2shell') for mass exploitation of two recent vulnerabilities, CVE-2026-109618 and CVE-2026-109619, described as a bulk exploit. Public tooling for a fresh CVE sharply shortens the window before opportunistic scanning and web-shell deployment hits PHP-based public sites. Defenders running exposed PHP applications, common in government portals and telco/banking web fronts, should check patch status now.
Ransomware Qilin publica a la española Airtificial
Airtificial
The Qilin group has added Airtificial, a Spanish engineering and robotics technology company, to its leak site. No file listing is shown yet, so the scope of exfiltrated corporate, client or project data is unconfirmed. As a listed Spanish supplier to industrial and public-sector programmes, its compromise can expose partner data and OT/engineering information.