Underground · what matters today
The underground stories that broke through this window. Gov/mil, access sales, ransomware, leaks, stealers. Screenshots and context on each.
Distribution by category · window
- Gov / Military55
- Access sale43
- Ransomware47
- Leak419
- Stealer0
- Other10
Window
Category
Severity
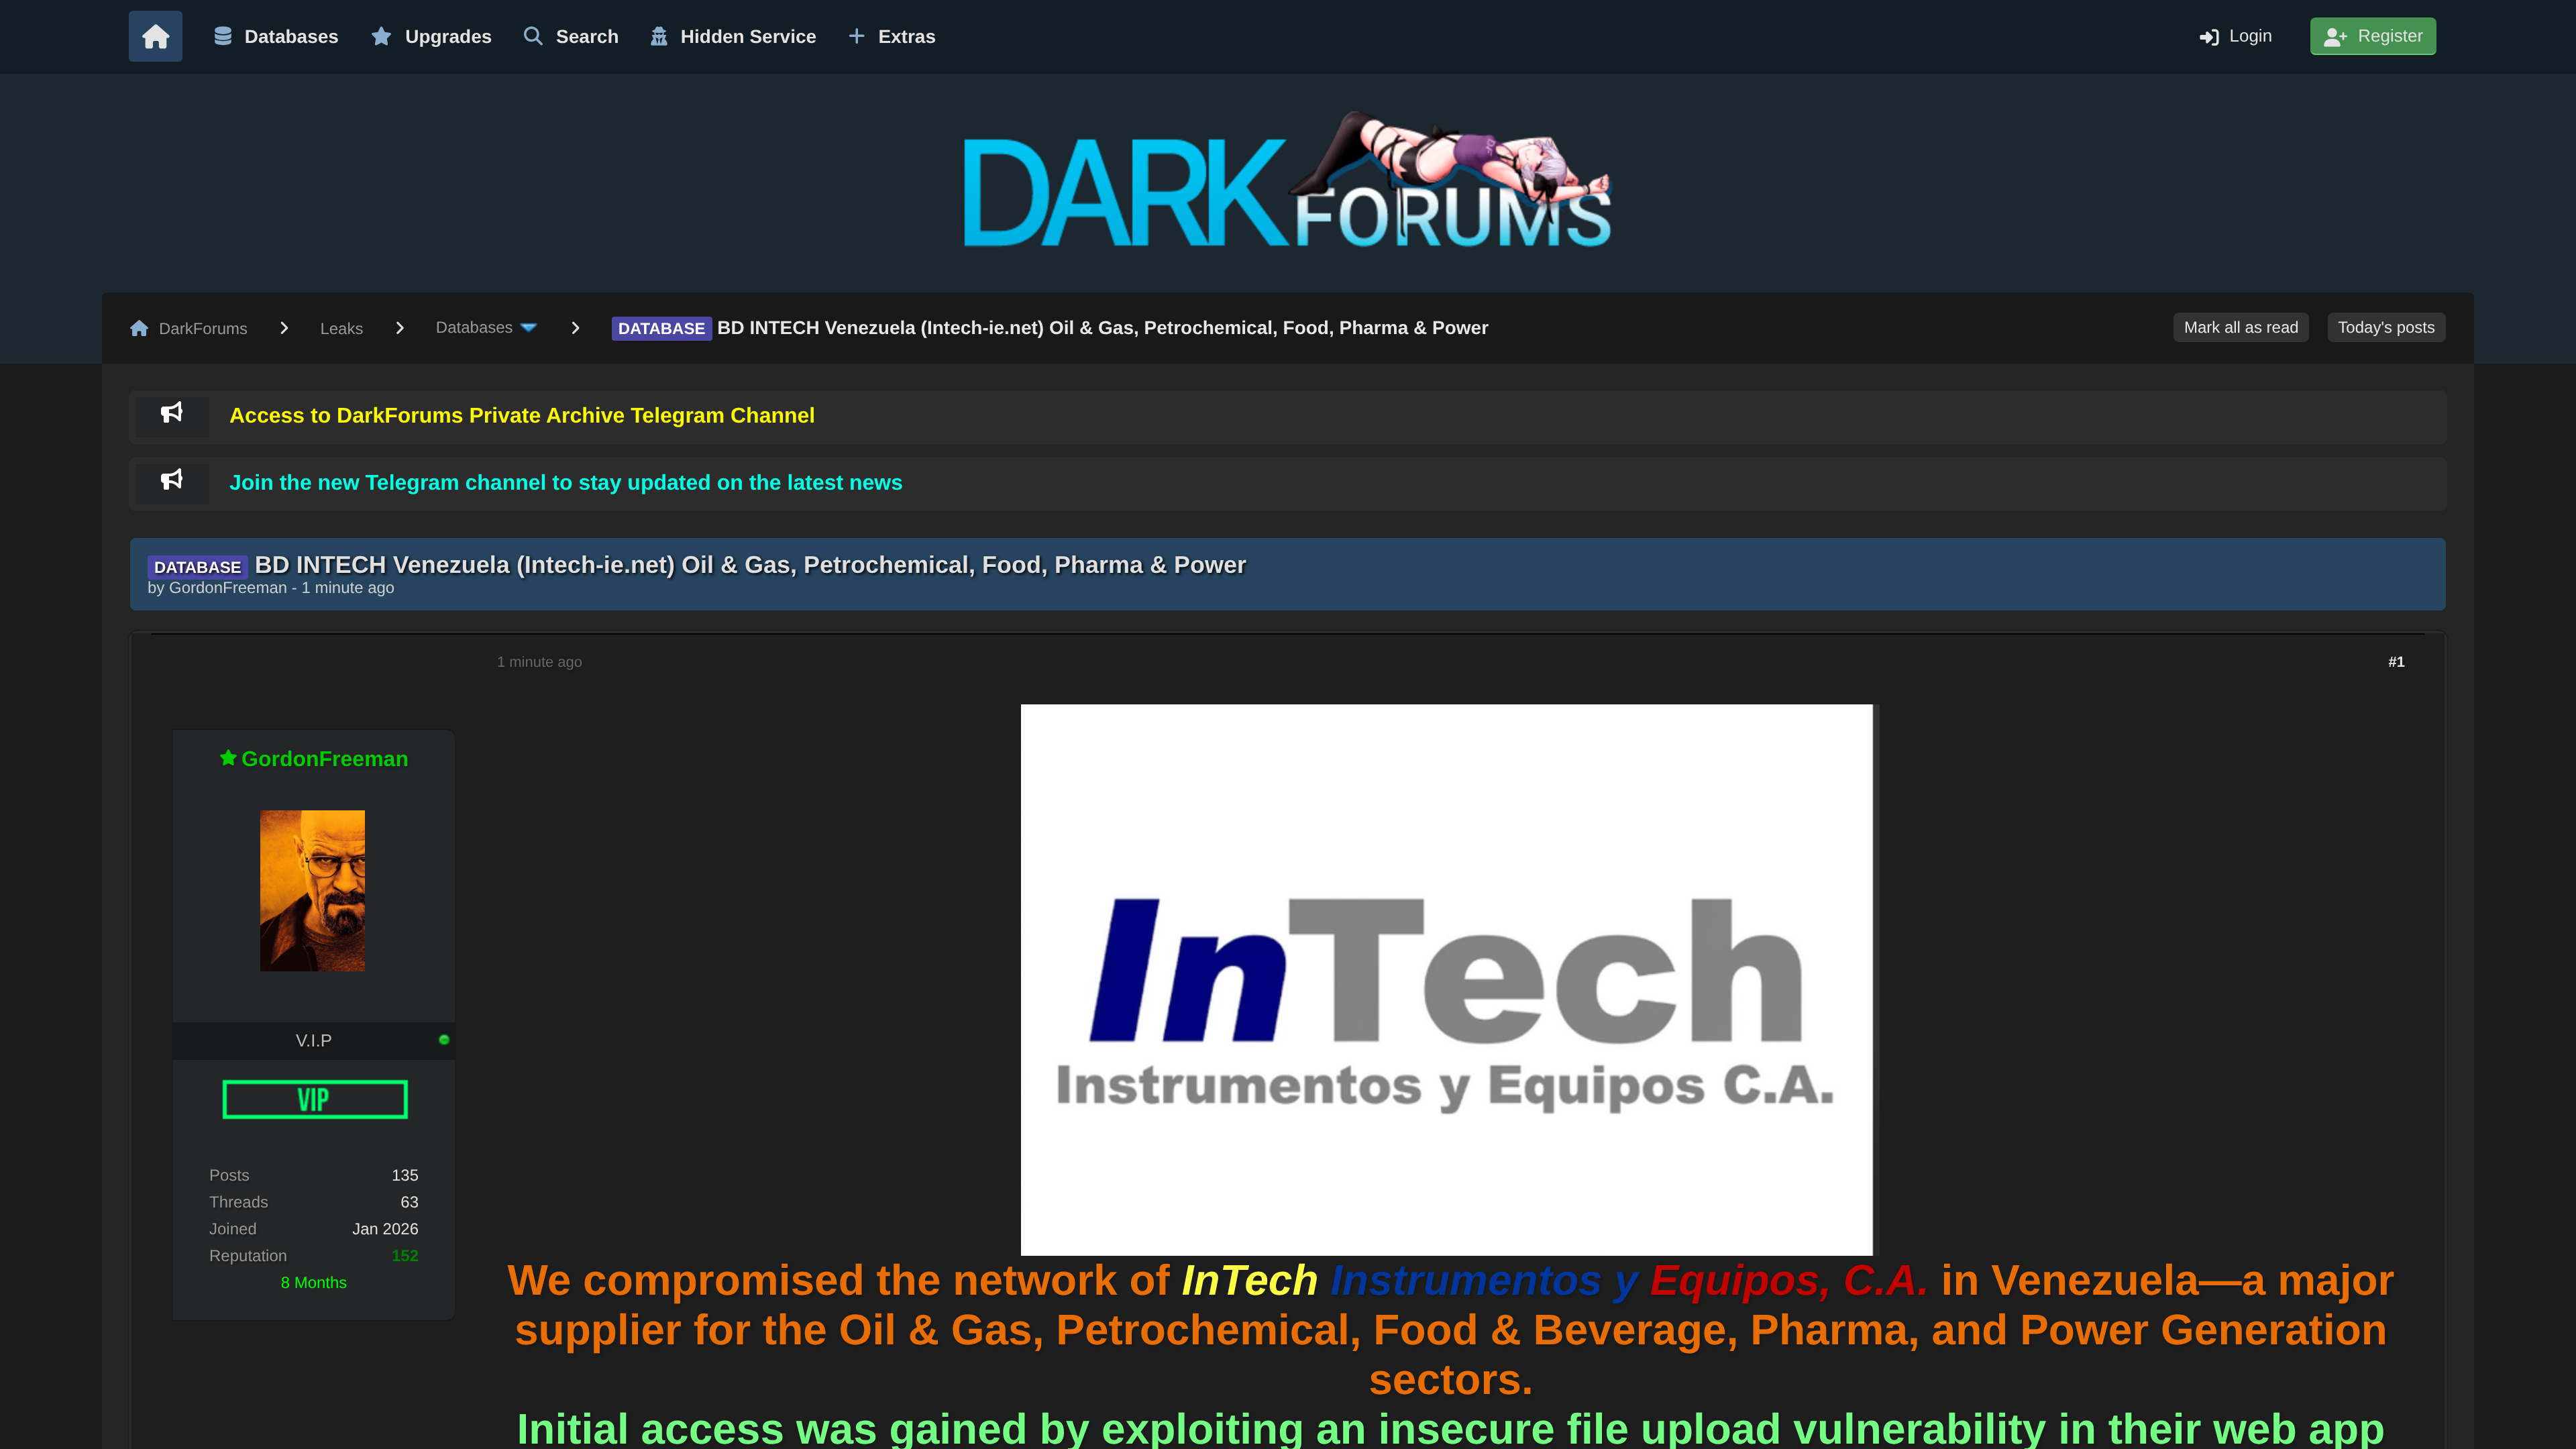
Base de datos de la venezolana Intech (oil & gas, energía) filtrada
Intech Venezuela (intech-ie.net)
A database belonging to Intech (intech-ie.net), a Venezuelan firm serving oil & gas, petrochemical, food, pharma and power sectors, is being offered on DarkForums. Leaked industrial-sector data can expose supplier contacts, system details and corporate credentials useful for spear-phishing or intrusion against regional critical infrastructure. Defenders in Venezuelan energy and industrial sectors should treat this as a likely precursor to targeted attacks.
Base de datos de California Tax Data publicada en foro
California Tax Data
A forum thread advertises a database from californiataxdata.com, a US tax-preparation service, with a record count visible in the mirrored title. Tax-related datasets carry SSNs, addresses and financial identifiers that fuel identity fraud and tax-refund scams. It is not a government body, but firms holding taxpayer data are high-value and worth validation and client notification.
Filtración de la base de datos completa de cyta.com.ar con SQLi
cyta.com.ar (Argentina)
An actor is publishing the full database of cyta.com.ar, an Argentine ISP/telecom provider, together with a working SQL injection on the site. The dump likely contains customer records and credentials, and the live SQLi means the exposure is ongoing rather than historical. Argentine telecom operators are tier-1 critical infrastructure, so this warrants immediate notification, WAF blocking and credential resets.
Filtración de datos de la aerolínea Plus Ultra en España y Latinoamérica
Plus Ultra Líneas Aéreas
A free release claims a roughly 103k-record dataset belonging to Plus Ultra, the Spanish carrier operating routes to Venezuela and across Latin America. Airline data typically includes passenger PII, contact details and booking data useful for fraud and targeted phishing. Despite being a non-government entity, its cross-border LatAm operations make it relevant for regional monitoring.
Servicio vende correos de gobierno y gestiona suspensión de dominios
Government email accounts (unidentified)
A BreachForums vendor advertises access to government email accounts alongside handling of Emergency Disclosure Requests and removal or suspension of domains. If genuine, it implies privileged access to official mailboxes that could be used for impersonation or BEC against public-sector contacts. The listing gives no country or entity, so it is a capability to monitor rather than a confirmed AR/LATAM incident.
Venta de 200 GB de datos privados con 61 GB de documentos confidenciales
A seller on DarkForums is advertising roughly 200GB of private data, of which 61GB are described as confidential documents, without naming the victim. The volume and document-heavy nature suggest an internal file-share or archive from an enterprise or institutional network rather than a simple credential dump. Defenders should track the thread to see if samples later identify a Latin American or government entity.
Brecha de datos de la china MicroPort Scientific
MicroPort Scientific Corporation
A thread advertises a data breach of Chinese medical-device maker MicroPort Scientific. If genuine, it exposes corporate data from a healthcare-technology vendor, a supply-chain-sensitive target. Details are gated behind the forum login, so the impact is unconfirmed.
Filtración de datos de población del gobierno de Banjarbaru (Indonesia)
Gobierno de Banjarbaru (Indonesia)
A database of Banjarbaru civil population data ('Data Kependudukan') has appeared for sale on BreachForums. It exposes citizen identity records held by an Indonesian local government, a sensitive public-sector dataset. Useful for identity fraud and a pattern of government-sector leakage outside LATAM.
Filtración de base de datos de SFR, Bouygues y La Poste en Francia
SFR / Bouygues / La Poste / Free (Francia)
A multi-company database covering French carriers and services (SFR, Bouygues, La Poste, Free) is being shared. If genuine, it aggregates customer records across several major French organizations, enabling large-scale identity and credential fraud. Outside our region but notable as a large multi-organization leak.
Venta de datos de 280.000 empleados de AstraZeneca (Azure)
AstraZeneca
A seller offers 280,000+ AstraZeneca employee records allegedly pulled from Azure, with full names, emails, titles, phones and addresses. This is high-value corporate PII on a major pharmaceutical, ideal for executive phishing and business email compromise. It also hints at possible cloud tenant compromise.
Filtración de 3,2 millones de pedidos de la búlgara EKONT.BG
EKONT.BG
A database of 3,196,563 orders from Bulgarian courier EKONT.BG, covering 2024-2026, has been leaked. The volume and recency point to live operational data including customer names, addresses and order details. It enables targeted phishing and fraud against the courier's customer base.
Venta de base de datos de 36 millones de clientes de Telcel (México)
Telcel (México)
A seller on BreachForums is offering a 36-million-record database from Telcel, Mexico's largest mobile operator. The data reportedly contains sensitive subscriber information, exposing a critical LATAM telecom and its customers. This enables SIM-swap, phishing and fraud at national scale and warrants immediate telco/regulator alerting.
Volcado privado de 16,7 millones de credenciales URL:LOG:PASS
A private 'UHQ' dump of roughly 16.7 million URL:LOG:PASS credential pairs is being shared, combining site URLs, usernames and passwords. Although untargeted, its size makes it a potent credential-stuffing and password-spraying source; defenders should expect increased authentication attacks and check exposure of their domains.
Venta de volcado con 280.000 empleados de AstraZeneca (Azure)
AstraZeneca
A seller is advertising a 280,000+ record Azure-linked employee dump for AstraZeneca containing full names, emails, job titles, phone numbers and addresses. This is high-value corporate PII on a major global pharmaceutical firm, ideal for targeted phishing, business-email-compromise and credential-stuffing against a critical-sector organisation.
Filtración de base de datos de la Universidad de Guadalajara
Universidad de Guadalajara
A database belonging to the University of Guadalajara (Mexico) has been posted for free on a clandestine forum, likely exposing student, faculty and staff records. A leak involving a public Mexican university can hand attackers reusable institutional credentials and large volumes of personal data, enabling phishing, fraud and further intrusion into .mx education networks.
Filtración de 1,1 millones de datos de la Federación Italiana de Tenis
Federazione Italiana Tennis e Padel
A post offers a 1.1-million-record database attributed to the Italian Tennis and Padel Federation. The dump likely contains member and contact records that enable phishing, identity theft and targeted fraud against the federation's community. Sports governing bodies should verify the leak and warn affected members.
Filtración de datos de la Liga MX en foro clandestino
Liga MX
A fresh thread on DarkForums claims to expose data tied to Liga MX, Mexico's top professional football league. If genuine, the records could include fan, partner or staff data usable for phishing and fraud against a high-profile Latin American brand. Mexican sports and media defenders should verify the claim and watch for credential abuse.
Filtración de base de datos de la plataforma Cambridge One
Cambridge University Press & Assessment (Cambridge One)
A thread claims to leak the database of Cambridge One, the educational platform run by Cambridge University Press & Assessment. If real, the data covers a well-known academic brand with global users, enabling credential abuse and targeted phishing against institutions that rely on the platform. Schools and universities using Cambridge One should watch for account-takeover attempts.
Filtración de 4,8 millones de registros de NomadEducation
NomadEducation (FR)
A post advertises a 4.8-million-record database allegedly belonging to French education firm NomadEducation. A leak of this scale exposes large volumes of student and staff personal data suitable for phishing, account takeover and downstream fraud. Organizations in the education sector should verify the claim and monitor for exposed user credentials.
Filtración de datos de 280.000 empleados de AstraZeneca
AstraZeneca
A seller is offering a 280,000-record dump of AstraZeneca employees, seemingly pulled from an Azure directory, with full name, email, job title, phone and address. This volume of verified corporate PII fuels targeted phishing, business email compromise and executive impersonation. Security teams should treat the exposed identities as compromised and reset credentials.
Venta de cuentas de correo de gobiernos y policía de España
Gobiernos y cuerpos policiales de España
A seller is offering email account credentials belonging to Spanish government and law enforcement bodies. Trusted public-sector and police mailboxes enable phishing, impersonation and lateral access into state networks, and can be abused for fraud or disinformation. Defenders in Spanish public administration should force credential resets and monitor for stuffing and anomalous logins.
Base de datos de bordersstore.com publicada
bordersstore.com
A DarkForums thread posted today advertises a database for bordersstore.com, likely an e-commerce store's customer data. No record count or sample is visible yet. If real it could expose shoppers' PII, useful for phishing and card fraud; defenders should confirm the scope.
Venta de base de datos francesa no identificada
A DarkForums user is advertising an unspecified French database for sale with no sample or details provided. If genuine, it could expose French organizations' records, but the lack of specifics makes scale and victim unclear. Worth monitoring for a sample or further claims.
Venta de volcado de 67.000 empleados de Cardinal Health en Azure
Cardinal Health
A forum seller is offering a 67,000+ record Azure employee dump for Cardinal Health with names, emails, titles, phones and addresses. This healthcare personnel data enables targeted phishing, fraud and impersonation. Given its medical supply role, defenders should treat it as elevated risk.