Underground · what matters today
The underground stories that broke through this window. Gov/mil, access sales, ransomware, leaks, stealers. Screenshots and context on each.
Distribution by category · window
- Gov / Military54
- Access sale43
- Ransomware49
- Leak421
- Stealer0
- Other10
Window
Category
Severity
Filtración de base de datos de la plataforma Cambridge One
Cambridge University Press & Assessment (Cambridge One)
A thread claims to leak the database of Cambridge One, the educational platform run by Cambridge University Press & Assessment. If real, the data covers a well-known academic brand with global users, enabling credential abuse and targeted phishing against institutions that rely on the platform. Schools and universities using Cambridge One should watch for account-takeover attempts.
Filtración de 4,8 millones de registros de NomadEducation
NomadEducation (FR)
A post advertises a 4.8-million-record database allegedly belonging to French education firm NomadEducation. A leak of this scale exposes large volumes of student and staff personal data suitable for phishing, account takeover and downstream fraud. Organizations in the education sector should verify the claim and monitor for exposed user credentials.
Filtración de datos de 280.000 empleados de AstraZeneca
AstraZeneca
A seller is offering a 280,000-record dump of AstraZeneca employees, seemingly pulled from an Azure directory, with full name, email, job title, phone and address. This volume of verified corporate PII fuels targeted phishing, business email compromise and executive impersonation. Security teams should treat the exposed identities as compromised and reset credentials.
Venta de cuentas de correo de gobiernos y policía de España
Gobiernos y cuerpos policiales de España
A seller is offering email account credentials belonging to Spanish government and law enforcement bodies. Trusted public-sector and police mailboxes enable phishing, impersonation and lateral access into state networks, and can be abused for fraud or disinformation. Defenders in Spanish public administration should force credential resets and monitor for stuffing and anomalous logins.
Base de datos de bordersstore.com publicada
bordersstore.com
A DarkForums thread posted today advertises a database for bordersstore.com, likely an e-commerce store's customer data. No record count or sample is visible yet. If real it could expose shoppers' PII, useful for phishing and card fraud; defenders should confirm the scope.
Venta de base de datos francesa no identificada
A DarkForums user is advertising an unspecified French database for sale with no sample or details provided. If genuine, it could expose French organizations' records, but the lack of specifics makes scale and victim unclear. Worth monitoring for a sample or further claims.
Venta de volcado de 67.000 empleados de Cardinal Health en Azure
Cardinal Health
A forum seller is offering a 67,000+ record Azure employee dump for Cardinal Health with names, emails, titles, phones and addresses. This healthcare personnel data enables targeted phishing, fraud and impersonation. Given its medical supply role, defenders should treat it as elevated risk.
Venta de volcado de 280.000 empleados de AstraZeneca en Azure
AstraZeneca
A seller is offering a 280,000+ record Azure employee dump for AstraZeneca with full names, emails, job titles, phones and addresses. Such personnel data enables phishing, impersonation and social engineering against a major pharma. Defenders should watch for credential-stuffing and targeted phishing.
Ransomware n0n publica a la brasileña Prafesta Embalagens
Prafesta Ind. e Com. de Embalagens Ltda
n0n ransomware published Prafesta, a Brazilian packaging maker, exposing Sapiens ERP and Vetorh payroll data after an unpaid attack. The leak includes thousands of invoices, worker CPF IDs, bank certificates and eSocial government filings. Exposed CPFs and certs are strong fraud vectors for defenders.
Base de datos de Cultura.com (2,1M, 2024) filtrada
Cultura.com
A 2.1 million-record database attributed to Cultura.com and dated 2024 was posted to DarkForums. Although the data is roughly two years old, records of this size still fuel credential stuffing and phishing against reused accounts. Organisations should check for reuse of these credentials even though the breach is not fresh.
Venta de acceso admin a joacademy.com (Jordania)
joacademy.com
A threat actor is selling administrator access to groups.joacademy.com, a Jordanian education platform. Admin access allows data exfiltration, account takeover and abuse of the site's user base. Website operators in the region should review access controls and rotate privileged credentials.
Venta de acceso al portal gubernamental de Punjab
dsjlahore.punjab.gov.pk
A threat actor is advertising access to dsjlahore.punjab.gov.pk, a Pakistan Punjab government judicial portal. Government portal access enables data theft or defacement and can serve as a foothold for deeper intrusions into public administration networks. Public-sector defenders should audit exposed admin interfaces and rotate credentials.
Base de datos de la francesa Boulanger (132K) a la venta
Boulanger
A 132,000-record customer database attributed to French electronics retailer Boulanger was posted on 16 Oct 2026. Customer PII at this scale enables targeted phishing and account takeover against the retailer's clientele. French retail and fraud teams should confirm scope and alert affected customers.
Filtración de datos de 67.000 empleados de Cardinal Health
Cardinal Health
A seller is offering a 67,000+ record 'Azure employee dump' of US healthcare giant Cardinal Health, including full names, emails, titles, phones and addresses. The scale and corporate PII make it highly valuable for BEC, vishing and credential attacks against a major health-sector target. Directory exposure of this kind is often a precursor to targeted intrusion.
Base de datos de SFR Stargate publicada en BreachForums
SFR (Stargate)
A database labelled 'SFR Stargate' was posted to BreachForums on 16 Oct 2026. SFR is a major French telecom operator and part of critical national infrastructure, so any subscriber or internal data exposure risks fraud, SIM abuse and follow-on intrusion. Telecom defenders should verify the dump's authenticity and watch for credential reuse across their estate.
Filtración de 1M de credenciales email/contraseña de México
A one-million-line email:password combo attributed to Mexico is circulating, posted hours ago. Unlike small combolists, the size makes it usable for credential-stuffing against Mexican organisations and citizens at scale. It is lower impact than a confirmed database breach but still relevant for regional defenders due to its volume.
Venta de acceso admin a portal del gobierno de Filipinas (cda.gov.ph)
Cooperative Development Authority (cda.gov.ph), Filipinas
An actor is selling administrative access to cs.cda.gov.ph, a Philippine government portal belonging to the Cooperative Development Authority. Government-portal admin access enables data theft, defacement or lateral movement into public infrastructure. Although outside the AR-LATAM region, it is a fresh and concrete government initial-access sale worth tracking.
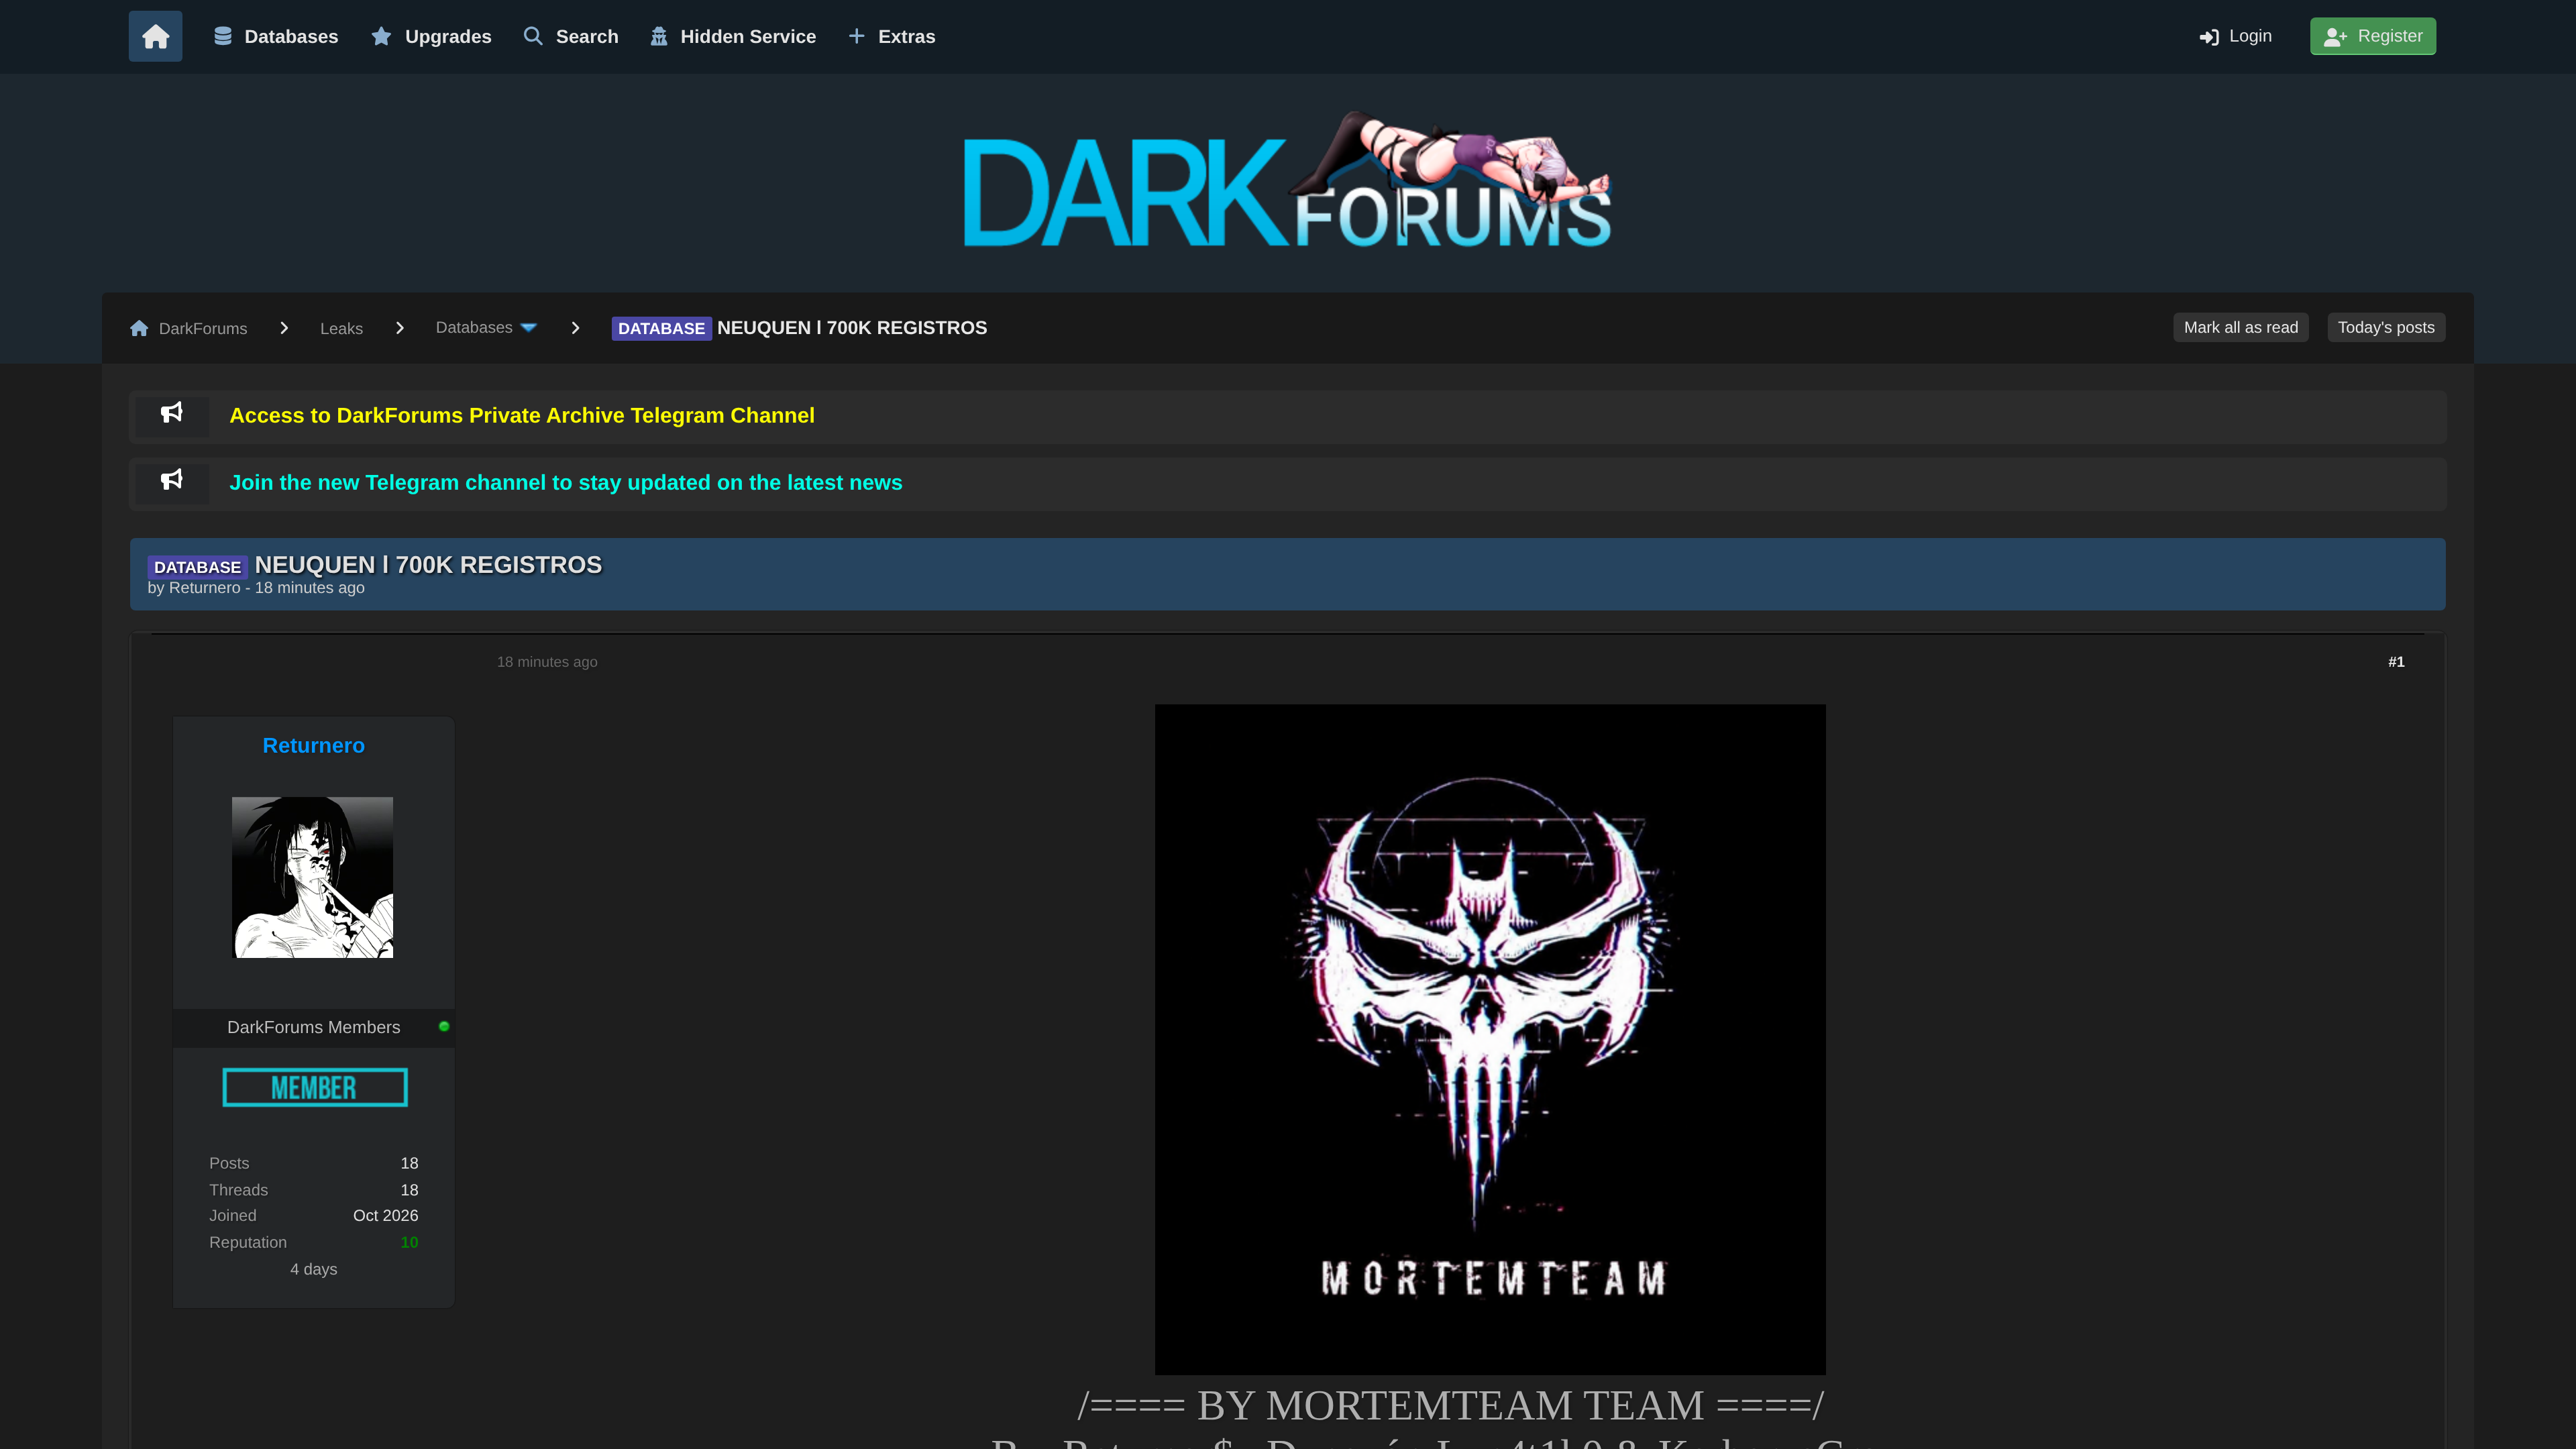
Filtración de base de datos de la provincia de Neuquén (700K registros)
Provincia de Neuquén (Argentina)
A database of roughly 700,000 records attributed to Argentina's Neuquén province is being offered/leaked on a darkweb forum just minutes ago. Neuquén is a strategic jurisdiction due to energy (Vaca Muerta) and critical infrastructure, so exposure could affect citizens, public employees and provincial services. The volume and freshness make this a high-priority alert for regional defenders.
Filtración de base de datos de la Secretaría de Salud de México
Secretaría de Salud del Gobierno de México
A threat actor is exposing a database attributed to Mexico's federal Secretariat of Health, a core government body handling citizens' sensitive medical data. Such records typically include personal identifiers, clinical data and contact details, creating serious privacy and fraud risk. Posted minutes ago, this is a live, time-sensitive leak affecting Mexican government and healthcare defenders.
Filtración de 1,9 millones de registros del portal fiscal francés reduction-impots.fr
reduction-impots.fr
A 1.9M-record database tied to the French tax-reduction portal reduction-impots.fr (dated 2024) has resurfaced on leak forums. It relates to a government service, but the data is from 2024 and concerns France, so it is not a fresh AR-LATAM alert. Useful mainly as historical context for victim notification and identity-theft monitoring.
Base de datos de la empresa turca Tera publicada en foro de filtraciones
Tera
A threat actor posted a database allegedly belonging to the Turkish company Tera on DarkForums, just minutes before discovery. Scale is unconfirmed and the victim is outside Latin America, but any real corporate dataset leak can feed credential replay and fraud. Worth monitoring for scope and confirmation.
Doxeo de un empleado de la NSA publicado en foro clandestino
NSA
A threat actor posted a dox of an alleged NSA employee on DarkForums roughly seven hours before discovery. Doxxing government personnel exposes personal data that enables harassment, social engineering and physical targeting. It is US-focused rather than AR-LATAM, but relevant to government/military threat monitoring.
Ransomware Redact publica a la energética estadounidense ONEOK
ONEOK, Inc.
The Redact ransomware group listed ONEOK, Inc., a major US oil & gas pipeline and energy operator with ~$39.4B revenue, on its leak site. A confirmed listing signals data theft and potential operational disruption across critical energy infrastructure. Energy-sector defenders should treat this as a live extortion threat and watch for downstream/supply-chain impact.
Venta de webshells para abuso de posicionamiento SEO
The actor is selling bulk web shells advertised for SEO abuse, indicating compromised sites resold as a commodity. Buyers can inject spam, redirects and malware into the hijacked sites. Site owners should monitor for unauthorized content and indicators of compromise.